Troubleshooting Tip: IPSec tunnel with certificate-based authentication between two FortiGates
| Description | This article demonstrates an example IPSec tunnel configuration with certificate-based authentication using a default certificate. |
| Scope | FortiGate. |
| Solution | When certificate-based authentication is used for IKE, the default FortiGate built-in certificate can be used for testing.
Warning: The following configuration cannot be considered secure for production environments, since any peer certificate signed by the same internal Fortinet_Sub_CA would be accepted, including other FortiGate devices using their own Fortinet_Factory certificates. Use trusted, privately or publicly signed certificates for production environments.
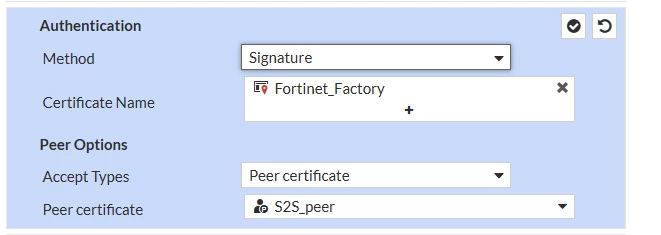
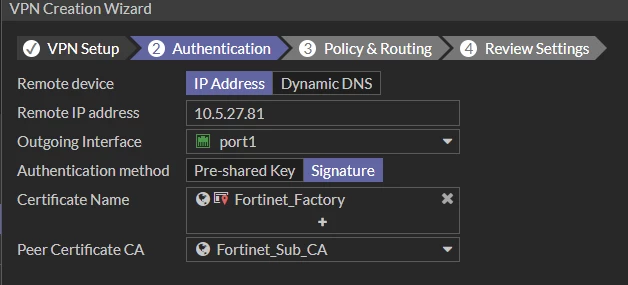
In the above configuration, the local certificate used is Fortinet_Factory, and the Peer CA certificate is built-in Fortinet_Sub_CA.
Since the keys and dependencies for these built-in certificates are available with the firewall, there is no need to import additional key files here.
Once the configuration is done, phase1 status will be up.
LAB # diagnose vpn ike gateway list name S2S
vd: root/0
id/spi: 4 7f307ee05619b343/e0329706744c1643
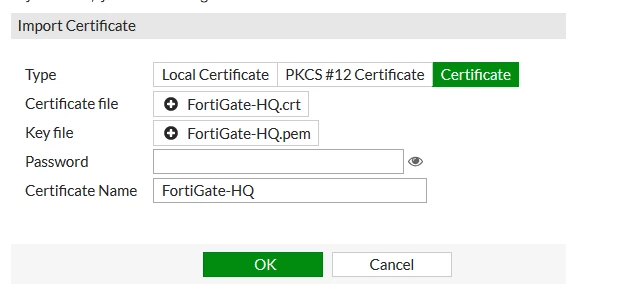
It is recommended to use a certificate signed by a trusted private or public CA for IPsec signature authentication. See Import a Certificate for steps to import a third-party CA-signed certificate.
It is also necessary to import the CA certificate on both the VPN endpoints.
Note: The Fortinet_Factory certificate cannot be used in configuration on FortiGate-200G devices and any other FortiGate devices where the private key of this certificate is stored in the Trusted Platform Module (TPM), see FortiGate identity stored in TMP. If a default certificate is required in this case, the new 'Fortinet_Default_SSL' certificate can be used.
Related article: |