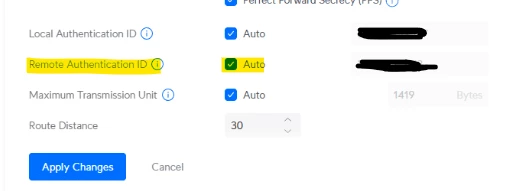
Troubleshooting Tip: IPsec phase 2 tunnel down between Unifi gateway and FortiGate behind NAT router
| Description | This article describes the steps to troubleshoot and resolve the issue of the IPsec Phase 2 tunnel being down between Unifi Gateway and FortiGate behind the NAT Router. |
| Scope | FortiGate. |
| Solution | To resolve the issue of the IPsec Phase 2 tunnel being down between Unifi Gateway and FortiGate behind the NAT Router, follow these steps:
Troubleshooting Steps:
diagnose vpn ike log filter rem-addr4 <Remote_Peer_IP>
Phase_1:
diagnose vpn ike gateway list name <Phase1_Name>
Phase_2:
diagnose vpn ike gateway list name <Phase2_Name>
If issues persist, submit a technical case to Fortinet TAC Support. See this article: Technical Tip: How to create a ticket for Fortinet TAC. |