



Troubleshooting Tip: IPS engine manual update failing with error 'Failed to upgrade database'
Description | This article describes how to resolve a scenario where the manual upgrade of the IPS engine fails with the error 'Failed to upgrade database'. |
Scope | FortiGate, BIOS security level set to High (Level 2). |
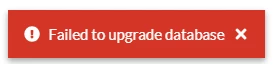
Solution | If the BIOS security level is set to 'High', the firewall will reject the manually uploaded unsigned engine and give the following error:
Verify the BIOS security level using the 'get system status' command on the CLI:
To change the security level:
Note: Some FortiGate models do not provide the U option in the BIOS and use a physical security switch instead. Check the hardware-specific documentation before changing the security level.
After executing the command, upload the required IPS engine file, and once the IPS upgrade has completed successfully, revert the setting to its default state by running the command:
Additional Information: In some environments, downtime for rebooting the device to lower the security level is not acceptable. In such cases, if the firewall is managed by FortiManager, the device administrator can import the required IPS engine package into FortiManager and install it directly. For the FortiOS v7.6 and v8.0 branches, before attempting to downgrade the BIOS version, first disable GUI CDN Usage and admin-http-rate-limit under the global settings, then retry the IPS engine upgrade. Disabling GUI CDN Usage will automatically log out the administrator from the existing session. This does not impact data traffic or production traffic.
Note: Related document: Technical Tip: Change security level on FortiGate G series models |
