Solution | In this example, two FortiGate firewalls (FW1 and FW2) are connected via a site-to-site IPsec tunnel and a FortiClient dial-up client behind FW1 is unable to connect to a remote access IPsec VPN on FW2.
Both tunnels are configured to use IKEv2.
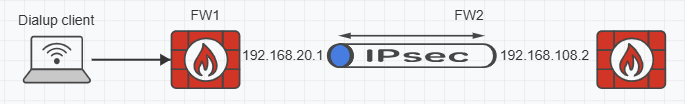
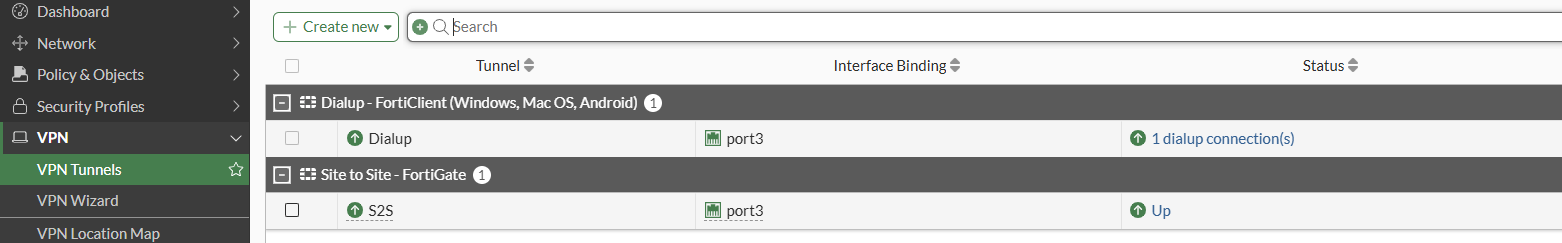
On FW2, dial-up and site-to-site tunnels are configured on the same interface (port3) and remote gateway of the site to site tunnel is 192.168.20.1.
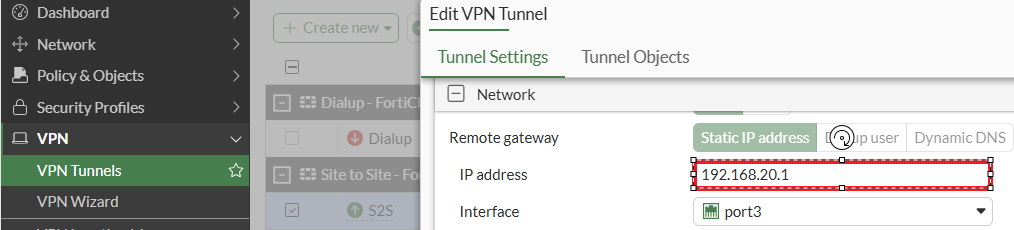
Negotiation attempts from the dial-up client are NAT-ed to the same IP address as the remote gateway of the site-to-site tunnel (192.168.20.1). As a result, FW2 matches the connection to the site-to-site (S2S) tunnel rather than the dial-up tunnel, as shown in the debug output below (output truncated):
diagnose debug reset
diagnose debug application ike -1
diagnose debug enable

ike V=root:0: comes 192.168.20.1:1012->192.168.108.2:500,ifindex=5,vrf=0,len=369....
ike V=root:0: IKEv2 exchange=SA_INIT id=dcbc31830aa4bc48/0000000000000000 len=369
ike V=root:0:dcbc31830aa4bc48/0000000000000000:2: responder received SA_INIT msg
ike V=root:0:dcbc31830aa4bc48/0000000000000000:2: NETWORK ID : 0
ike V=root:0:dcbc31830aa4bc48/0000000000000000:2: incoming proposal:
ike V=root:0:dcbc31830aa4bc48/0000000000000000:2: proposal id = 1:
ike V=root:0:dcbc31830aa4bc48/0000000000000000:2:   protocol = IKEv2:
ike V=root:0:dcbc31830aa4bc48/0000000000000000:2:      encapsulation = IKEv2/none
ike V=root:0:dcbc31830aa4bc48/0000000000000000:2:         type=ENCR, val=AES_CBC (key_len = 128)
ike V=root:0:dcbc31830aa4bc48/0000000000000000:2:         type=INTEGR, val=AUTH_HMAC_SHA_96
ike V=root:0:dcbc31830aa4bc48/0000000000000000:2:         type=PRF, val=PRF_HMAC_SHA
ike V=root:0:dcbc31830aa4bc48/0000000000000000:2:         type=DH_GROUP, val=ECP384.
ike V=root:0:dcbc31830aa4bc48/0000000000000000:2: proposal id = 2:
ike V=root:0:dcbc31830aa4bc48/0000000000000000:2:   protocol = IKEv2:
ike V=root:0:dcbc31830aa4bc48/0000000000000000:2:      encapsulation = IKEv2/none
ike V=root:0:dcbc31830aa4bc48/0000000000000000:2:         type=ENCR, val=AES_CBC (key_len = 256)
ike V=root:0:dcbc31830aa4bc48/0000000000000000:2:         type=INTEGR, val=AUTH_HMAC_SHA2_256_128
ike V=root:0:dcbc31830aa4bc48/0000000000000000:2:         type=PRF, val=PRF_HMAC_SHA2_256
ike V=root:0:dcbc31830aa4bc48/0000000000000000:2:         type=DH_GROUP, val=ECP384.
ike V=root:0:dcbc31830aa4bc48/0000000000000000:2: matched proposal id 2
ike V=root:0:dcbc31830aa4bc48/0000000000000000:2: proposal id = 2:
ike V=root:0:dcbc31830aa4bc48/0000000000000000:2:   protocol = IKEv2:
ike V=root:0:dcbc31830aa4bc48/0000000000000000:2:      encapsulation = IKEv2/none
ike V=root:0:dcbc31830aa4bc48/0000000000000000:2:         type=ENCR, val=AES_CBC (key_len = 256)
ike V=root:0:dcbc31830aa4bc48/0000000000000000:2:         type=INTEGR, val=AUTH_HMAC_SHA2_256_128
ike V=root:0:dcbc31830aa4bc48/0000000000000000:2:         type=PRF, val=PRF_HMAC_SHA2_256
ike V=root:0:dcbc31830aa4bc48/0000000000000000:2:         type=DH_GROUP, val=ECP384.
ike V=root:0:dcbc31830aa4bc48/0000000000000000:2: lifetime=86400
ike V=root:0:dcbc31830aa4bc48/0000000000000000:2: SA proposal chosen, matched gateway S2S
ike V=root:0: invalid IKE request SPI dcbc31830aa4bc48/a040c11ecd77017c:00000001
To resolve this issue, configure different network ID for the dial-up and site-to-site tunnels. Network ID is used in FortiOS IPsec phase1 interface to help distinguish and manage multiple overlay tunnels. By default, all tunnels have a network ID of 0. In this scenario, the network ID of the site to site tunnel will be changed to 1.
Go to VPN -> VPN Tunnels and Edit the site to site tunnel. Under Authentication, enable 'Network overlay' and enter a number e.g. 1.
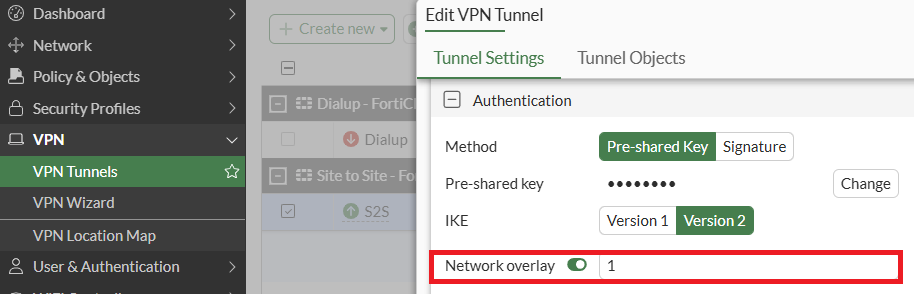
Select 'OK' to save the changes and test the VPN connection.
To configure network ID in the CLI:
config vpn ipsec phase1-interface
    edit "S2S"
        set network-overlay enable
        set network-id 1
    next
end
Note: The network-id value must match on both ends of the site-to-site tunnel. Configure the same network-overlay enable and network-id 1 on FW1's corresponding phase1-interface as well; a mismatched network-id can cause the tunnel to match unexpectedly instead of resolving the conflict. Valid values for network-id are 0-255, with a default of 0 (as seen in the debug output above).
Alternatively, it is possible to change the network ID of the dial-up tunnel. However, the network ID must also be updated on the FortiClient as per this article:
Technical Tip: How to configure Network ID for distinguishing IKEv2 IPsec VPN tunnels using FortiClient XML file.
After applying this change, the client successfully establishes the dial-up tunnel. On FW2, both the dial-up and site-to-site tunnels are up concurrently:
 |