Troubleshooting Tip: How to troubleshoot SNMP traps not getting generated from the firewall
| Description | This article describes how to troubleshoot an issue where SNMP traps do not get generated from the firewall. |
| Scope | All FortiGate firewalls. |
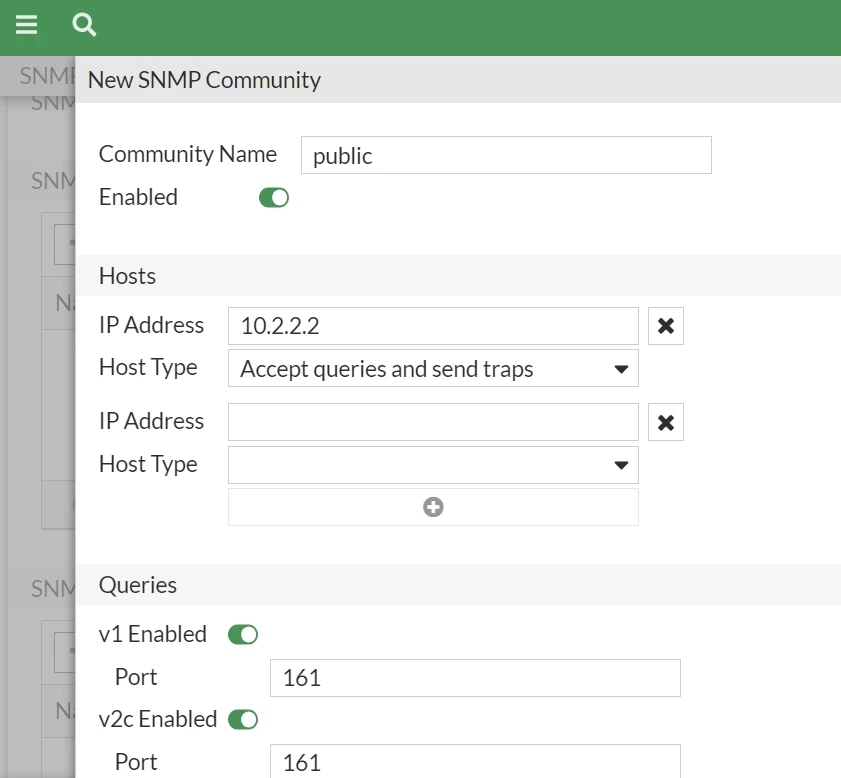
| Solution | The first step is to verify if there is an SNMP manager server configured in the firewall as shown below:
config system snmp sysinfo set status enable end
If the route is over a VPN tunnel, consider configuring the Source IP as referenced in the following article:
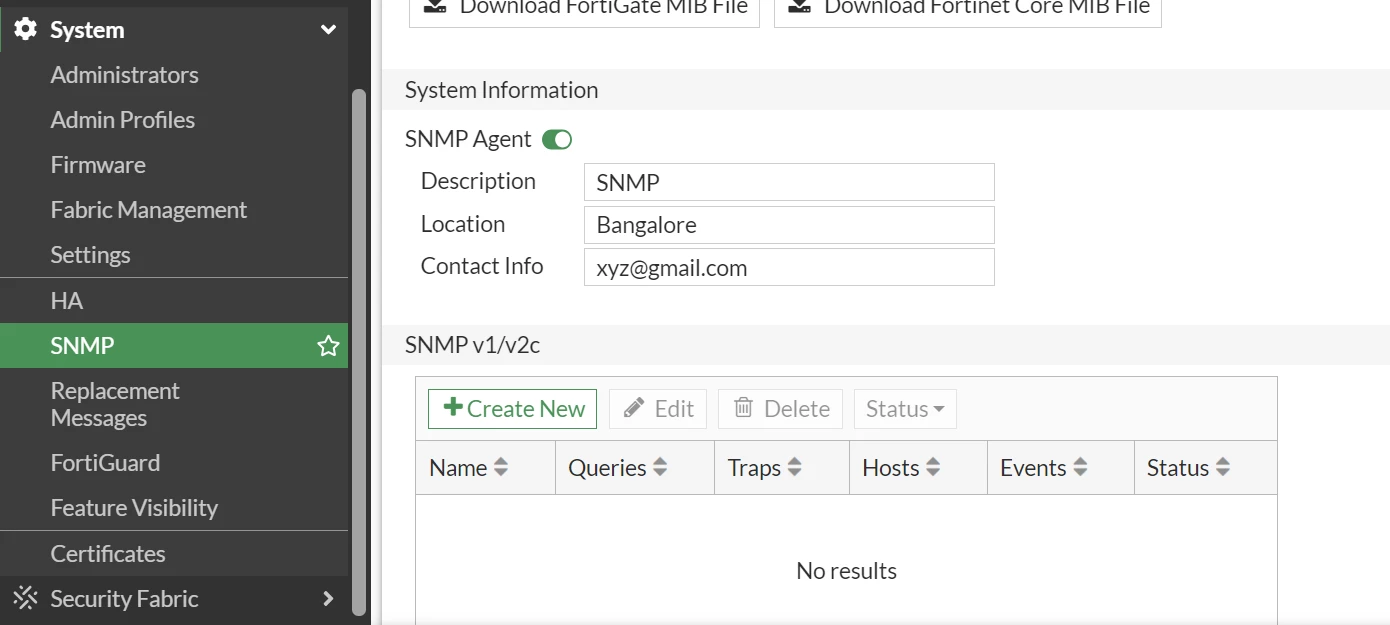
Make sure that under System -> SNMP, the agent option is enabled and the description fields are filled as shown below:
If it is still not generating, execute these commands:
After executing these commands, try to disable some interfaces in the downtime. Logs should be centered. Execute 'diagnose debug disable'.
FortiOS provides a mechanism to generate a test SNMP trap which is sent to a configured SNMP server :
diagnose snmp trap send
To see if that test SNMP trap is sent to the remote server, it is possible to open 3 SSH sessions :
SSH No1:
diagnose debug console timestamp enable diagnose debug enable
SSH No2:
diagnose snmp trap send
SSH No3:
diagnose sniffer packet any "host x.x.x.x and port abc " 6 0 l <- Where x.x.x.x is the IP address of the SNMP server and ABC is the port used for SNMP traps in the configuration (default 162).
A packet capture can also be taken from the GUI. See Troubleshooting Tip: Packet Capture on FortiOS GUI.
If it is impossible to view traps being sent toward the hosts on SSH No3, try restarting the SNMP daemon:
Note: If the environment is running in HA, HA direct needs to be enabled. See Technical Tip: SNMP communication working scenario with respect to FortiGate device in HA and ha-direct options.
If the issue persists, share the logs when opening the TAC ticket. |