It is recommended to inspect traffic on both the FortiClient and FortiGate sides to identify the root cause.
Note:
Packet captures and debug sessions should be run simultaneously.
Packet capture. Open a PuTTY session and make sure to save the Logs for future review. In PuTTY, under Category, select Logging, All Session output, and select the Folder location to save the File. Run the following command to capture IPsec traffic.
diagnose sniffer packet any " host <PublicIP of the Host getting disconnected> and port (500 or 4500) " 6 0 l
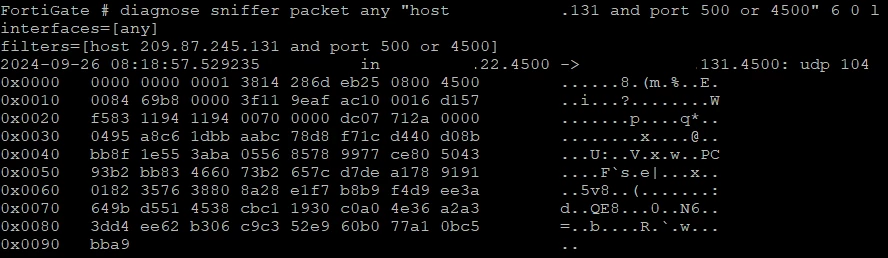
Note: If the sniffer does not show any packets, make sure to temporarily disable npu-offload under phase1.
Once the disconnection happens, press Ctrl + C to stop the sniffer and convert the output to PCAP.
Refer to the following article to convert the sniffer to PCAP: Technical Tip: How to import 'diagnose sniffer packet' data to WireShark.
Install Wireshark on the remote Host and start a packet capture using the following filter. It is important to select the correct interface when VPN signaling traffic is send out.
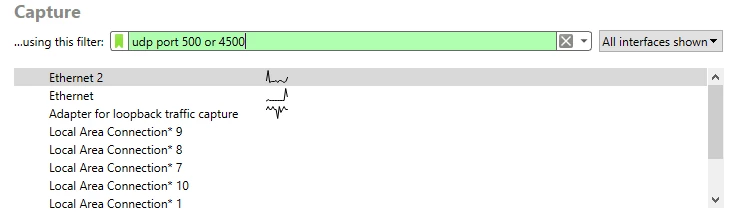
After having successfully captured a disconnection, follow the steps in Technical Tip: Decrypt ESP packets to decrypt the ESP packets.
Debugging:
Run the following debug process in PuTTY to make sure the session does not get disconnected from the FortiGate.
Using the CLI in the GUI to collect the debug output may result in a file containing wrong formatting or a timeout disconnection from the session.
diagnose vpn ike log filter clear
diagnose vpn ike log filter rem-addr4 <PublicIP of the Host getting disconnected>
diagnose debug console timestamp enable
diagnose debug application ike -1
diagnose debug application fnbamd -1
diagnose debug enable
To stop the debugging process:
diagnose debug disable
diagnose debug reset
The command 'timestamp enable' debug can help filter the debug by looking at a specific time if the time and date of the disconnection are already known.
The command 'ike log-filter dst-addr4' can help filter for a host having a disconnection issue.
Note:
Starting from v7.4.1, the 'diagnose vpn ike log filter dst-addr4' command has been changed to 'diagnose vpn ike log filter rem-addr4'.
Firmware compatibility.
Release notes show the compatibility version between FortiGate and FortiClient software. It is recommended review versions compatibility to avoid issues related to this.
Example for FortiClient compatibility for version 7.4.7: Product integration and support.
VPN FortiGate debug logs:
VPN Logs can be useful to review for more information about the time of disconnection and the possible root cause.
From the FortiGate GUI, navigate to Log & Report -> System Events -> VPN Events.
VPN FortiClient debug logs:
FortiClient Endpoint Logs can also be collected: however, debug log level has to be selected.
Before any VPN connection attempt, VPN module and debug log level must be enabled:
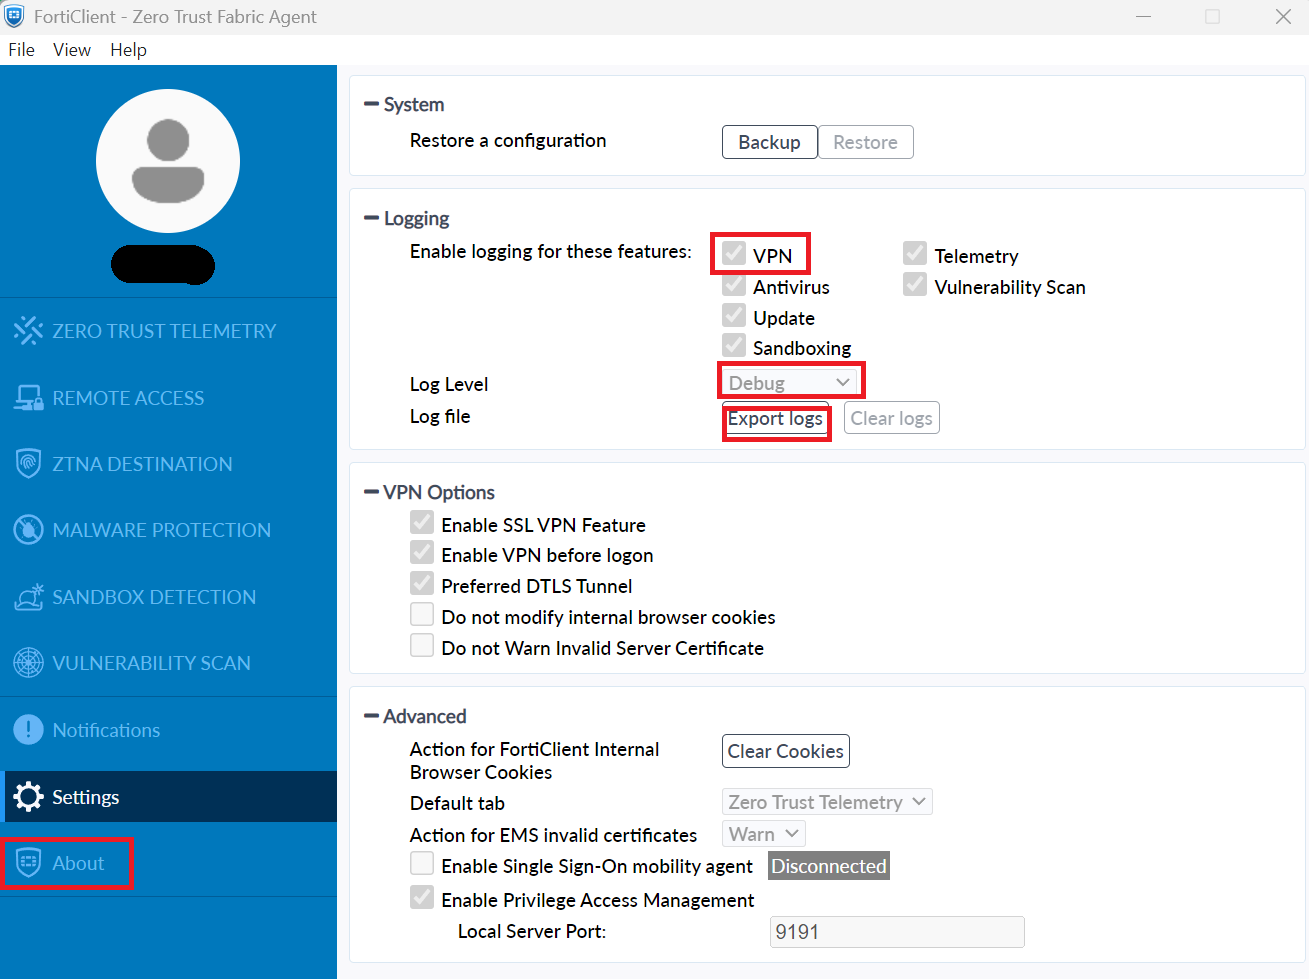
For a complete FortiClient Endpoint log analysis, the run diagnostic tool is recommended:
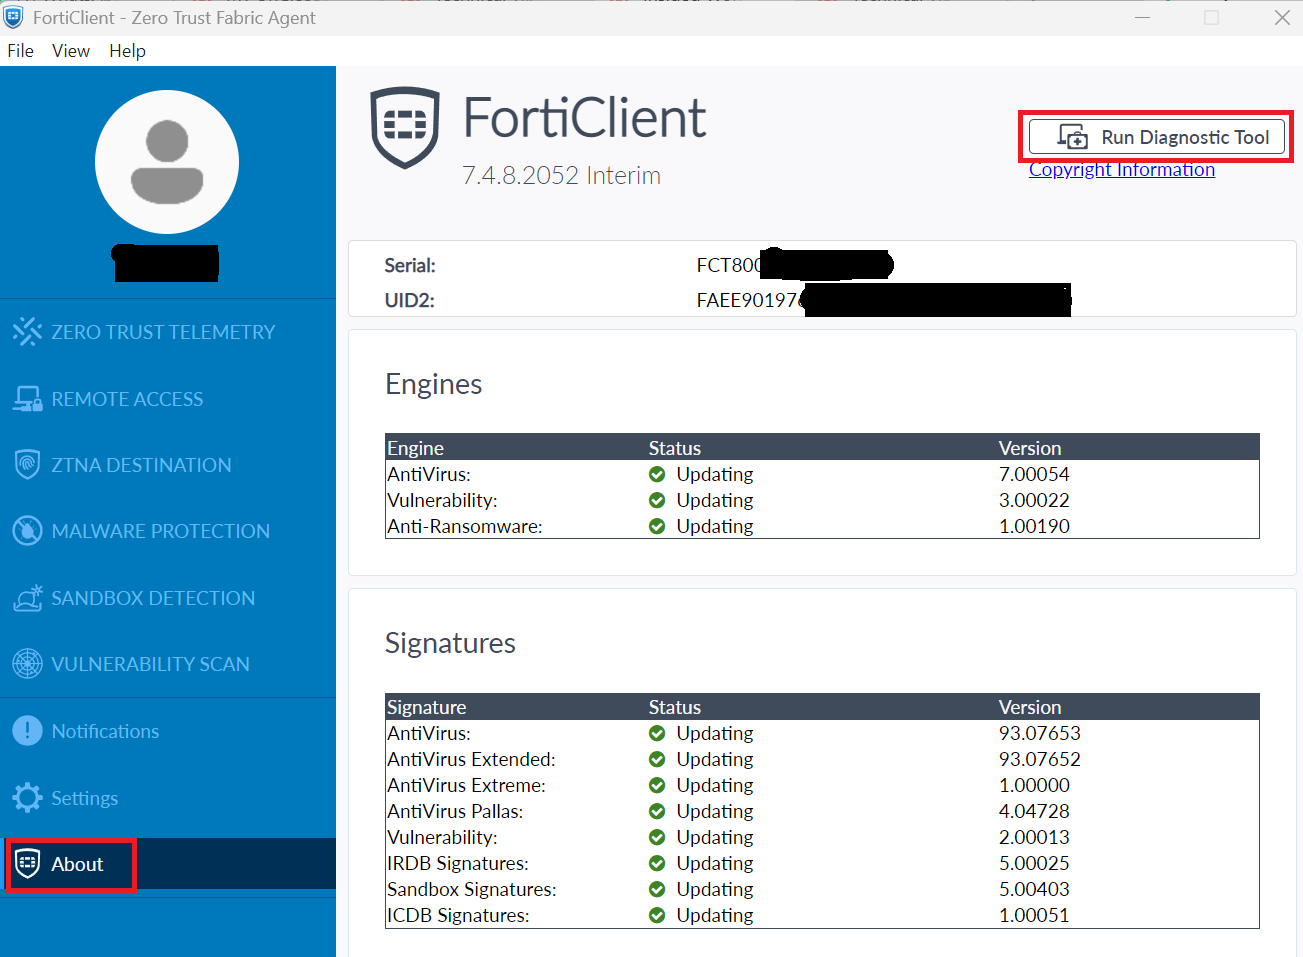
FortiClient collection log details can be found in the articles below:
NPU Offload:
IPsec traffic entering the FortiGate is offloaded to the NPU, meaning it can sometimes be a cause of the disconnection.
To rule out the possibility of this issue being related to NPU offload, temporarily disable NPU offload under phase1: Disabling NP offloading for individual IPsec VPN phase 1s.
The tunnel is going down.
Check the Phase 2 settings and enable Autokey Keep Alive if the VPN tunnel frequently goes down.
DoS policy configuration.
DoS policy configuration should be verified on the specific interface where the IPsec dial-up VPN is bound if it is configured. It can be examined in Anomaly logs (Log & Report -> Security Events -> Anomaly logs) to determine if a DoS policy is incorrectly identifying VPN traffic as a threat and causing intermittent disconnections/slowness.
Related articles: |