



Troubleshooting Tip: How to identify if traffic received is Tagged or untagged on VLAN Interfaces
| Description | This article describes how to troubleshoot if the VLAN Gateway is not pingable on FortiGate. |
| Scope | FortiGate. |
| Solution | In some cases, VLAN interfaces are configured under an aggregate interface which is connected to LAN Network. If VLANs are not configured correctly on the switch side, FortiGate may receive traffic as tagged instead of untagged, and hence there will be no ARP reply from FortiGate.
To verify that, take a sniffer to check if the ARP request is hitting the VLAN interface or the Aggregate/Physical Interface. If the the ARP request is not hitting the VLAN interface then this traffic is a tagged traffic and an ARP reply may not be seen from FortiGate.
dia sniffer packet any "arp" 4 0 l 2024-08-13 19:18:41.004473 internal in arp who-has 192.168.1.113 tell 192.168.1.99
It is also possible to capture packets using a sniffer on the underlying interface and specifically capture the tagged traffic by using 'vlan <id>' in the sniffer filter:
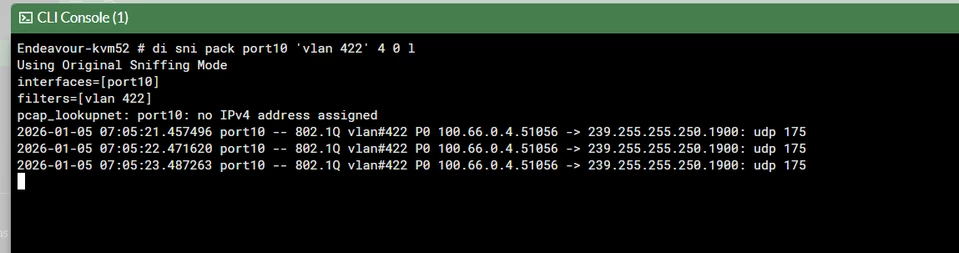
For more information, see Technical Tip: How to filter traffic with VLAN ID using packet sniffer |

