Felizardo
Staff
Staff
December 31, 2025

Troubleshooting Tip: How to exempt a domain from Explicit Proxy Authentication

  • December 31, 2025
  • 0 replies
  • 717 views
Description

This article describes how to allow a particular domain to bypass the Explicit Proxy Authentication process.

Scope FortiGate.
Solution

Consider a situation where the domain (e.g., www.example.com) should be exempted from Explicit Proxy Authentication. To accomplish the goal from the CLI, follow these steps:


  1. Create an FQDN Address Object (for the domain to exempt):


config firewall address

    edit "example_com"

        set type fqdn

        set fqdn "www.example.com"

    next

end


  1. Create a new authentication rule with no authentication method:


config authentication rule

    edit "no_authentication"

        set srcaddr "all"

        set dstaddr "example_com"

        set ip-based disable

    next

end


  1. Move the No-Auth Rule to the Top (above any authenticating rules):


config authentication rule

    move "no_authentication" before “kerberos_rule”

end


  1. Create a dedicated Proxy Policy (accepts traffic without triggering auth):


config firewall proxy-policy

    edit 20

        set name "no_authentication"

        set srcaddr "all"

        set dstaddr "example_com"

        set action accept

        set service "webproxy"
        set schedule always
        set logtraffic all

    next

end


  1. Ensure Policy Order: Proxy policies are evaluated top-down. Place this policy above general policies.


The steps to perform this in the GUI are mainly the same:


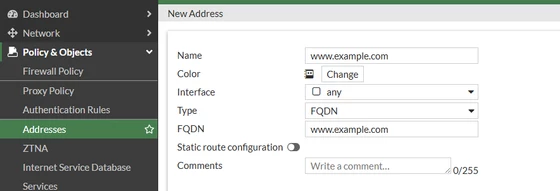
  1. Create the FQDN object:
                                               
    fqdnobject.PNG                                                       
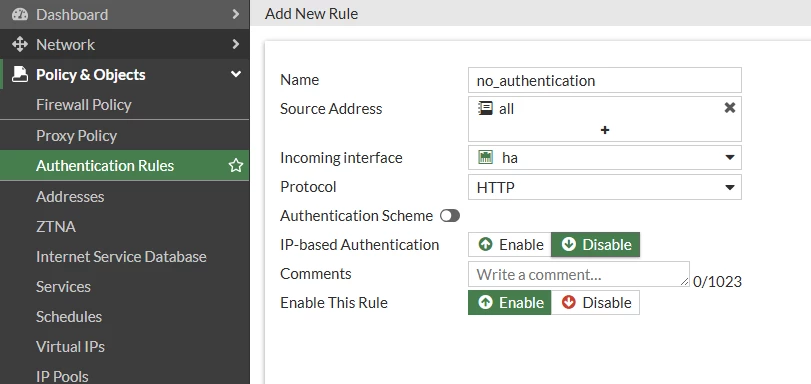
  2. Create a new authentication rule with no scheme and 'IP-based Authentication disabled'. It is only possible to specify the source address in the GUI; the destination will be added after:
                                                                           
    rule.PNG
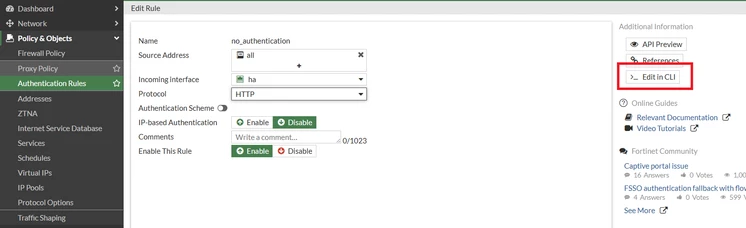
    Once the rule is saved, edit it again. There will be an 'Edit in CLI' button on the right:
                                                                                           
    editincli.PNG
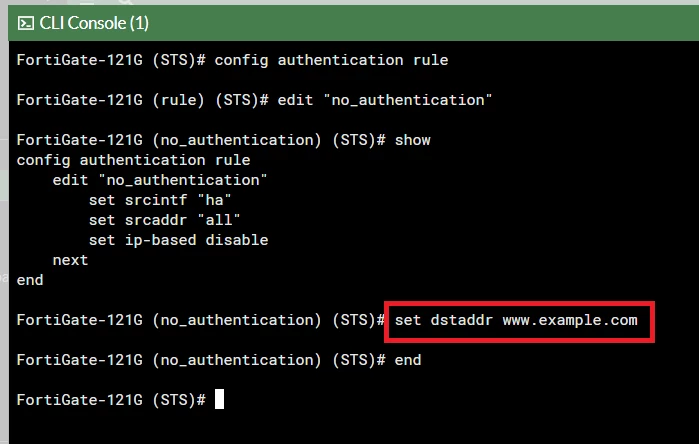
    Select that button, then do 'set  dstaddr <fqdn object>':

    cliedit.PNG
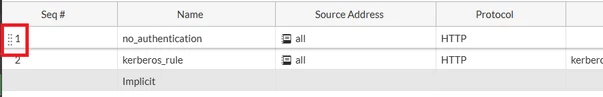
  3. Ensure that the rule is at the top (or at least above the rules with authentication) using the handle at the left:
                                                                                        
    handle.PNG
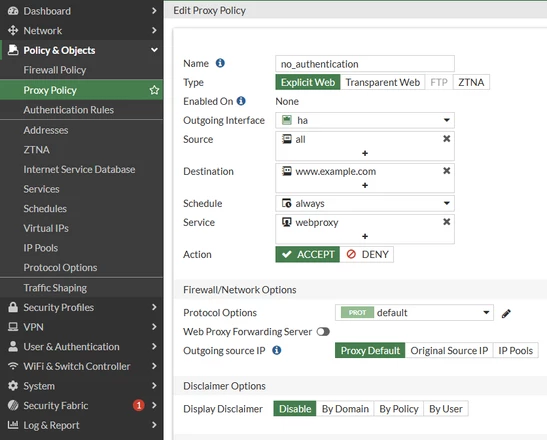
  4. Create a proxy policy with no user group specified, with the destination as the FQDN object:
                                                     
    policyproxy1.PNG                                       
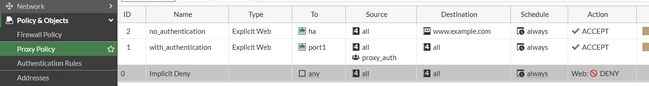
  5. Ensure the rule is at the top of the list, using the handle at the left if needed:
                                                                           
    policyproxy.PNG


Result:

The traffic to the domain (www.example.com) will be allowed to bypass the explicit proxy authentication.

Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
Thought Leadership. Security Summit. Thursday, October 8th. Disney's Grand Californian Hotel & SPA, Anaheim, CA.
Security Operations Summit: Modernize SecOps. Operate AI-Native.AMER: November 4 | 9:00 AM PST. India and SAARC: November 5 | 10:00 AM IST. EMEA: November 5 | 10:30 AM CET. APAC: November 5 | 11:00 AM SGT