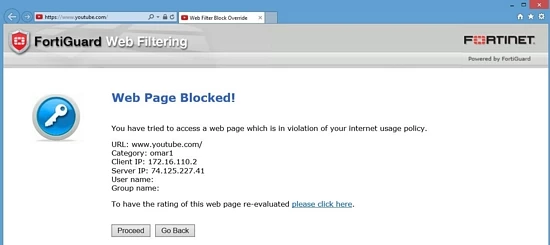
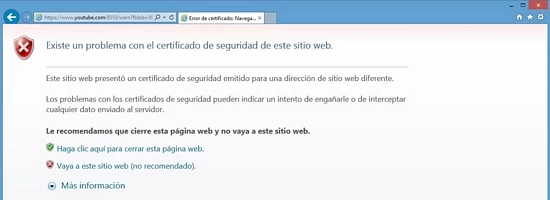
After the rating override is configured (web filter override, firewall policy and override users) it is necessary to configure on the following settings on the FortiGate:
config webfilter fortiguard
    set cache-mode ttl
    set cache-prefix-match enable
    set cache-mem-percent 2
    set ovrd-auth-port-http 8008
    set ovrd-auth-port-https 8010
    set ovrd-auth-port-warning 8020
    set ovrd-auth-https enable
    set warn-auth-https disable
    set close-ports disable
    set request-packet-size-limit 0
    set ovrd-auth-hostname ''
    set ovrd-auth-cert "Fortinet_Firmware"
end
Note: If set ovrd-auth-port-https is not available, first enable set ovrd-auth-https enable. The HTTPS authentication port can then be configured using set ovrd-auth-port-https.
The certificate used on the SSL inspection is 'Fortinet_CA_SSLProxy', so this certificate must be configured on the webfilter FortiGuard web filter:
config webfilter fortiguard
    set ovrd-auth-cert Fortinet_CA_SSLProxy
end
The certificate for the users settings must also be defined:
config user setting
    set auth-ca-cert Fortinet_CA_SSLProxy
end
The correct operation can now be checked. Use a web site where the FortiGuard web filter alert is shown. For example:
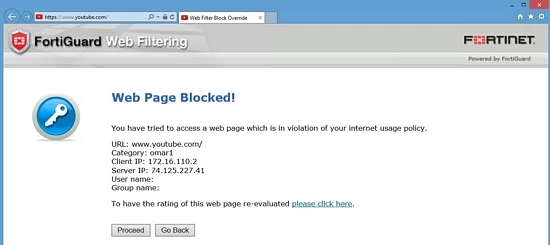
After selecting Proceed with the override the portal, it is possible to enter a username and password without any certificate error:
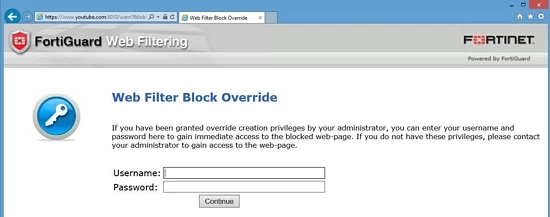
After entering the correct data, browsing of the webpage will be permitted:
 |