Troubleshooting Tip: Hostname is missing for devices connected via IPsec VPN
| Description | This article describes an issue related to the hostname, which is missing on the logs of the DHCP server, when users connect via IPsec VPN using IKEv2 and SAML, and FortiGate is configured as a DHCP relay. |
| Scope | FortiGate. |
| Solution | The devices are connected as follows:
Client (FortiClient) --- (connected via IPsec VPN to FortiGate) --- FortiGate (DHCP relay) - DHCP server.
The FortiGate configuration used for this issue is:
config vpn ipsec phase2-interface config sys interface config system settings
When the clients connect trough IPsec VPN using IKEv2 and SAML, the connection is successful. However, the hostname is not shown on the DHCP server logs as shown in the image below.
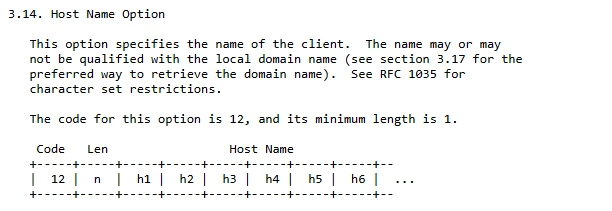
The hostname is sent using Option 12, as defined in RFC 2132 (screenshot below is taken from) RFC 2132: https://www.ietf.org/rfc/rfc2132.txt.
This behavior is noticed in environments with IPsec VPN using IKEv2 and SAML. This is currently not supported on FortiOS, and it is addressed to the engineering team through NFR: 1217216. |