Symptoms and cause: Check the FortiGate IPSEC tunnel status. In this example, it will show 2 tunnels: VPN_to_WQD and VPN_WQD. get ipsec tunnel list
NAME=VPN_to_WQD REMOTE-GW=60.50.220.14:0
P2NAME=VPN_to_WQD PROXY-ID-SOURCE=0.0.0.0/0.0.0.0 PROXY-ID-DESTINATION=0.0.0.0/0.0.0.0 STATUS=down
NAME=VPN_WQD REMOTE-GW=60.50.220.14:0
P2NAME=VPN_WQD PROXY-ID-SOURCE=172.27.16.0/255.255.240.0 PROXY-ID-DESTINATION=172.27.0.0/255.255.240.0 STATUS=down
Check the FortiGate IKE debug logs, and it will show this error: could not locate phase1 configuration.
IKE debug command:
diagnose debug disable
diagnose debug reset
diagnose vpn ike log filter clear
diagnose debug application ike -1
diagnose debug enable
IKE debug output:
ike V=root:0:VPN_to_WQD:VPN_to_WQD: IPsec SA connect 62 180.74.240.29->60.50.220.14:0
ike V=root:0:VPN_to_WQD: could not locate phase1 configuration.
ike V=root:0:VPN_to_WQD:VPN_to_WQD: IPsec SA connect 62 180.74.240.29->60.50.220.14:0
ike V=root:0:VPN_to_WQD: could not locate phase1 configuration.
ike V=root:0:VPN_WQD:VPN_WQD: IPsec SA connect 62 180.74.240.29->60.50.220.14:0
ike V=root:0:VPN_WQD: could not locate phase1 configuration.
ike V=root:0:VPN_WQD:VPN_WQD: IPsec SA connect 62 180.74.240.29->60.50.220.14:0
ike V=root:0:VPN_WQD: could not locate phase1 configuration.
This is because FortiGate's 2 IPSEC tunnels are reaching the same remote destination gateway IP (in this example: 60.50.220.14). In this example, the FortiGate has 2 IPSEC tunnels configured. The tunnel named VPN_WQD is using a static remote gateway IP: 60.50.220.14:
config vpn ipsec phase1-interface
    edit "VPN_WQD"
        set interface "wan1"
       set peertype any
        set net-device disable
        set proposal aes256-sha256
        set remote-gw 60.50.220.14
        set psksecret ENC xxxxxxx
     next
end
The tunnel named VPN_to_WQD uses the DDNS address as a remote gateway, which will be resolved to the same IP: 60.50.220.14.
config vpn ipsec phase1-interface
    edit "VPN_to_WQD"
        set type ddns
       set interface "wan1"
       set peertype any
        set net-device disable
       set proposal aes256-sha256
        set dhgrp 14
        set remotegw-ddns "RPG2-WQD.fortiddns.com"
        set psksecret ENC xxxxxxx
     next
end
Available solutions to address this issue: Remove the configuration of either one of the IPsec tunnels; then the remaining IPsec tunnel will be able to establish successfully. If it is required to have more than one IPSEC tunnel with the same remote gateway IP, the following additional settings are required to enable network-overlay and specify a different network-id for the remote gateway to differentiate these 2 site-2-site VPN tunnels.
config vpn ipsec phase1-interface
  edit "VPN_WQD"
        set network-overlay enable
        set network-id 100
  next

config vpn ipsec phase1-interface
  edit "VPN_to_WQD"
        set network-overlay enable
        set network-id 200
  next
end
This issue, or the log, can also be observed in a scenario in which the interface that is being used under IPsec is not configured with any IP address.
In the attached image, port 2 is being used for IPsec:
 No IP address is assigned to that interface: 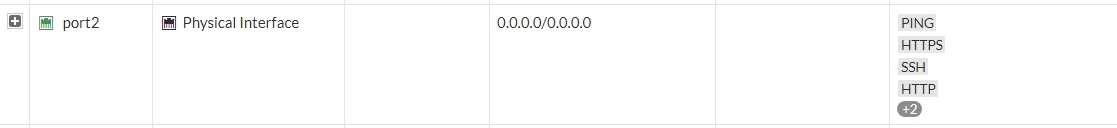 Similar IKE debugs can be seen:
FG5H1E-1 # ike V=root:0:500E-GURUGRAM:IPSEC: IPsec SA connect 10 10.5.52.80->10.5.205.176:0
ike V=root:0:500E-GURUGRAM: could not locate phase1 configuration.
Assign an IP address on the interface to fix this issue. Additionally, if the above workarounds are already applied but the issue still exists, it is recommended to set the 'local-gw' in phase1 interface settings, which might resolve the issue.
config vpn ipsec phase1-interface
    edit "IPSec-VPN"
        set interface "WAN"
        set local-gw x.x.x.x
    next
end
Related articles: Troubleshooting Tip: IPsec tunnel troubleshooting (IKE negotiations debugging) Technical Tip: Configuring multiple Site-to-Site IPsec VPNs between the same gateway IP address | 




