Troubleshooting Tip: FSSO Collector Agent Not Receiving User Information from DC Agent
| Description | This article describes an issue with the FSSO Collector Agent not being able to receive user information. |
| Scope | FortiGate, FSSO Collector Agent in Advanced access mode, DC Agent. |
| Solution | The FSSO Collector Agent can be used with or without TLS enabled.
In this scenario, there is a mismatch of the TLS settings. Debug logs from the FSSO Collector Agent report the following:
ldaplib::ldap_connect failed to connect to:x.x.x.x:3268 with error code 0x51
TCP/3268 is non-TLS, while TCP/3269 is TLS.
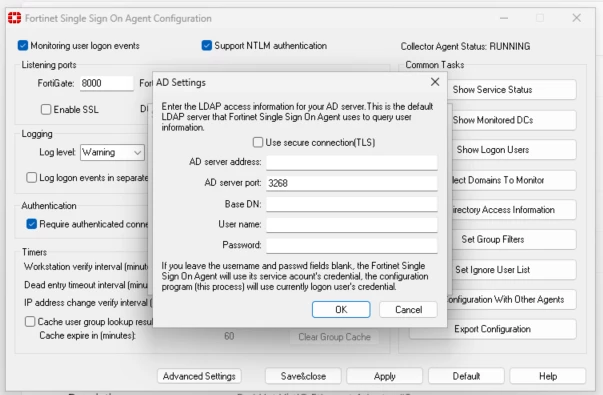
On the FSSO Collector Agent for AD Settings, check or uncheck the 'Use secure connection(TLS)' box.
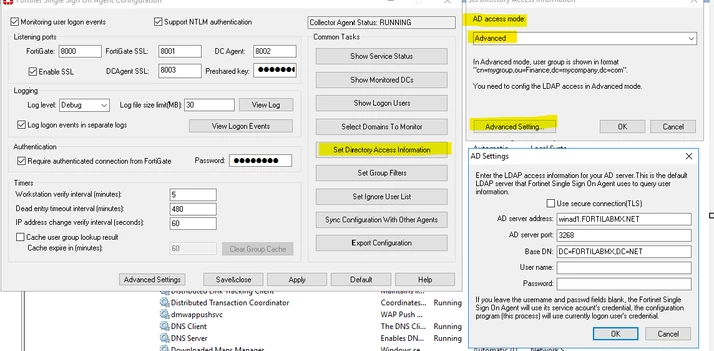
In order to open the AD setting window, the Admin needs to select 'Set Directory Access Information', choose Advanced in AD access mode, and select the Advanced Setting button.
|