FortiGate Wi-Fi configuration with Google SAML authentication and how to troubleshoot:
'FortiGate' will be acting as 'Service Provider' (SP) and 'GOOGLE' will be acting as 'Identity Provider' (IdP). In v7.0.5 and above, it is possible to configure Wi-Fi Access with SAML authentication. By default, FortiGate will use port 1000 to authenticate HTTP and 1003 to HTTPS traffic. config system global
set auth-http-port 1000
set auth-https-port 1003
end
Template: config user saml
edit "Wi-Fi-GOOGLE-SAML"
set entity-id "https://FGT-IP:1000/saml/metadata/"
set single-sign-on-url "https://FGT-IP:1003/saml/login/"
set single-logout-url "https://FGT-IP:1003/saml/logout/"
set idp-entity-id "https://accounts.google.com/o/saml2?idpid=YOUR_ID"
set idp-single-sign-on-url "https://accounts.google.com/o/saml2/idp?idpid=YOUR_ID"
set idp-single-logout-url "https://accounts.google.com/logout"
set idp-cert "Google_SAML_cert"
set user-name "Username"
set group-name "Groupname"
set digest-method sha1
next
end
Replace FortiGate-IP with the SSID Interface IP address.
For example:
The SSID interface IP will be 10.200.220.1.

Replace FortiGate-IP with the SSID interface IP 10.200.220.1.
set entity-id "https://10.200.220.1:1000/saml/metadata/"
set single-sign-on-url "https://10.200.220.1:1003/saml/login/"
set single-logout-url "https://10.200.220.1:1003/saml/logout/"
View the IdP details at admin.google.com:
Go to Security -> Authentication -> SSO with SAML applications.
Copy and paste the SSO URL and Entity ID into the template and download the Certificate.
 config user saml
edit "Wi-Fi-GOOGLE-SAML"
set entity-id "https://10.200.220.1:1000/saml/metadata/"
set single-sign-on-url "https://10.200.220.1:1003/saml/login/"
set single-logout-url "https://10.200.220.1:1003/saml/logout/"
set idp-entity-id "https://accounts.google.com/o/saml2?idpid=THE_ID"
set idp-single-sign-on-url "https://accounts.google.com/o/saml2/idp?idpid=THE_ID"
set idp-single-logout-url "https://accounts.google.com/logout"
set idp-cert "GOOGLE-IDP"
set user-name "Username"
set group-name "Groupname"
set digest-method sha1
next
end
Import the certificate from the Google IDP into the FortiGate. Go to System -> Certificates -> Import -> Remote Certificate.
 In the 'Upload', choose the certificate downloaded from the Google IDP and select 'OK'.  To rename the certificate, open the CLI console: config certificate remote
rename REMOTE_Cert_2 to GOOGLE-IDP
end
Paste the preconfigured template into the FortiGate Firewall via SSH CLI. Because some links contain a special character (GOOGLE IDP links containing '?), it is not possible to just copy/paste the SAML configuration, as it will break the link as a special character will be missing.
1st way: via SSH (GUI CLI Console – do not perform the trick and use SSH). If the link has a value '?' in the string: to enter the value '?' in the CLI, press 'Ctrl + V' before entering '?'.
For example:
set idp-entity-id: 'https://accounts.google.com/o/saml2?idpid=THE_TENANT_ID'
Copy and paste:
set idp-entity-id 'https://accounts.google.com/o/saml2
Press CTRL+V and use '?', then copy and paste 'idpid=THE_ID'.
2nd way: correct missing characters from the GUI (it is possible to configure SAML in the GUI starting from FortiOS 7.0+) or just configure it from the GUI. config user saml
edit "Wi-Fi-GOOGLE-SAML"
set entity-id "https://10.200.220.1:1000/saml/metadata/"
set single-sign-on-url "https://10.200.220.1:1003/saml/login/"
set single-logout-url "https://10.200.220.1:1003/saml/logout/"
set idp-entity-id "https://accounts.google.com/o/saml2?idpid=THE_ID"
set idp-single-sign-on-url "https://accounts.google.com/o/saml2/idp?idpid=THE_ID"
set idp-single-logout-url "https://accounts.google.com/logout"
set idp-cert "GOOGLE-IDP"
set user-name "Username"
set group-name "Groupname"
set digest-method sha1
next
end
Configure SAML group: In the example, the Group Name will be IT-Support.
config user group
    edit "Wi-Fi-GOOGLE-SAML-grp_IT-Support"
        set member "Wi-Fi-GOOGLE-SAML"
            config match
                edit 1
                    set server-name "Wi-Fi-GOOGLE-SAML"
                    set group-name "IT-Support"
                next
            end
        next
    next
end
Configure SSID for the Captive portal and select the SAML groups under WiFi Settings. Go to Security mode -> Captive portal -> Authentication portal -> Local User groups -> it will be the SAML groups (for example, 'Wi-Fi-GOOGLE-SAML-grp_IT-Support').
 config wireless-controller vap
edit "GRAKOV NETWORK"
set ssid "GRAKOV NETWORK"
set security captive-portal
set selected-usergroups "Wi-Fi-GOOGLE-SAML-grp_IT-Support"
next
end
Configure two policies. The first policy to allow authentication via Google IDP.
This policy for exemption from the captive portal internet-service-name: 'Google-Web' 'Google-DNS'. It is required for the authentication process and DNS resolution. The Google-Web ISDB allows users to access Google services (Gmail, Google search) before captive portal authentication.  If the user wants to restrict Google services like Gmail and Google Search before captive portal authentication, add only the URL below to the firewall policy destination: *.gstatic.com. accounts.google.co.in. accounts.google.com. dns.google.com. play.google.com.

In the following:
'GRAKOV_NETWORK' is the SSID. 'WAN_LAG' is the WAN interface. 'set internet-service-name "Google-Web" "Google-DNS"' is for DNS resolution and authentication. 'set captive-portal-exempt enable' is to allow authentication on IDP Google, for non-authenticated users.
config firewall policy
    edit 0
        set name "GOOGLE EXEMPT SAML and DNS"
        set srcintf "GRAKOV NETWORK"
        set dstintf "WAN_LAG"
        set action accept
        set srcaddr "all"
        set internet-service enable
        set internet-service-name "Google-Web" "Google-DNS"
        set schedule "always"
        set inspection-mode proxy
        set logtraffic all
        set nat enable
        set comments "SAML exclude policy for Google with DNS"
        set captive-portal-exempt enable
    next
end
The second policy is for the rest traffic once authenticated:
config firewall policy
    edit 0
        set srcintf "GRAKOV NETWORK"
        set dstintf "WAN_LAG"
        set action accept
        set srcaddr "all"
        set dstaddr "all"
        set schedule "always"
        set service "ALL"
        set inspection-mode proxy
        set logtraffic all
        set nat enable
        set groups "Wi-Fi-GOOGLE-SAML-grp_IT-Support"
    next
end
 At this point, the FortiGate portion (SP portion) is done.
Configure the IdP side (Google). Upon logging in to the admin portal (admin.google.com), go to the Application, select the 'Web and mobile app', select 'Add app', and choose 'custom SAML app'.  In Application details: Give 'App name' and, if required, 'Description'. In this example, the aApp name is 'Alpha Wi-Fi'. Select 'CONTINUE'.  Google will provide IDP details, the same details as in Security -> Authentication -> SSO with SAML applications.
 In the Google Identity provider details, select 'CONTINUE'; there are already all the necessary links and certificates.
In Service provider details, copy the value from the entity-id field ('https://10.200.220.1:1000/saml/metadata/') and paste it into the Entity ID string, then copy the value from single-sign-on-URL ('https://10.200.220.1:1003/saml/login/') and paste it into the ACS URL string.

Select 'CONTINUE'.
In 'Attribute mapping', add the proper mapping to use.
For example, Primary Email will be used as a username, and 'Google groups' will be used as Groupname.

Select 'FINISH'.
Once the configuration is done, the default action for the User Access is 'off' for everyone. Select User Access and change the service status to ON for everyone and select 'SAVE'.
 To configure, go to Google groups -> Directory -> Groups -> Configure Group -> Create group with members.

Test it. Connect to the SSID, and the user will be redirected to the Google IDP. Enter the credentials. After that, it will be authenticated.
Verification:

diagnose firewall auth filter method fw
diagnose firewall auth list
10.200.220.2, agrakov@myDomain.my
        src_mac: a8:64:f1:e4:d3:3d
        type: fw, id: 0, duration: 329, idled: 0
        expire: 300, allow-idle: 300
        flag(100): wsso
        server: Wi-Fi-GOOGLE-SAML
        packets: in 53776 out 89084, bytes: in 15918171 out 117613581
        group_id: 24
        group_name: Wi-Fi-GOOGLE-SAML-grp_IT-Support

----- 1 listed, 0 filtered ------
The SAML debug portion will be the same as for SSL VPN: see Troubleshooting Tip: Companion for troubleshooting SSL VPN with SAML Authentication.
With a debug level of -1 for detailed results:
diagnose debug application samld -1
diagnose debug enable

diagnose firewall auth filter method fw
diagnose firewall auth list
A common issue with this setup:
When applying the following configuration, it may be noticed that Android phones are unable to reach the Google authentication portal. After connecting to the Wi-Fi, they encounter a certificate error on the browser and are unable to reach anything on the internet.
When a client connects to an SSID, it performs an HTTP GET unencrypted request to check if there is a proxy or a captive portal on the network. In the case of Android phones, this request is sent to 'http://connectivitycheck.gstatic.com/generate_204'. This URL is contained in the 'GOOGLE-WEB' Internet Server Database object that was exempt from the captive portal with the first firewall policy created that allowed for reaching the Google authentication page.  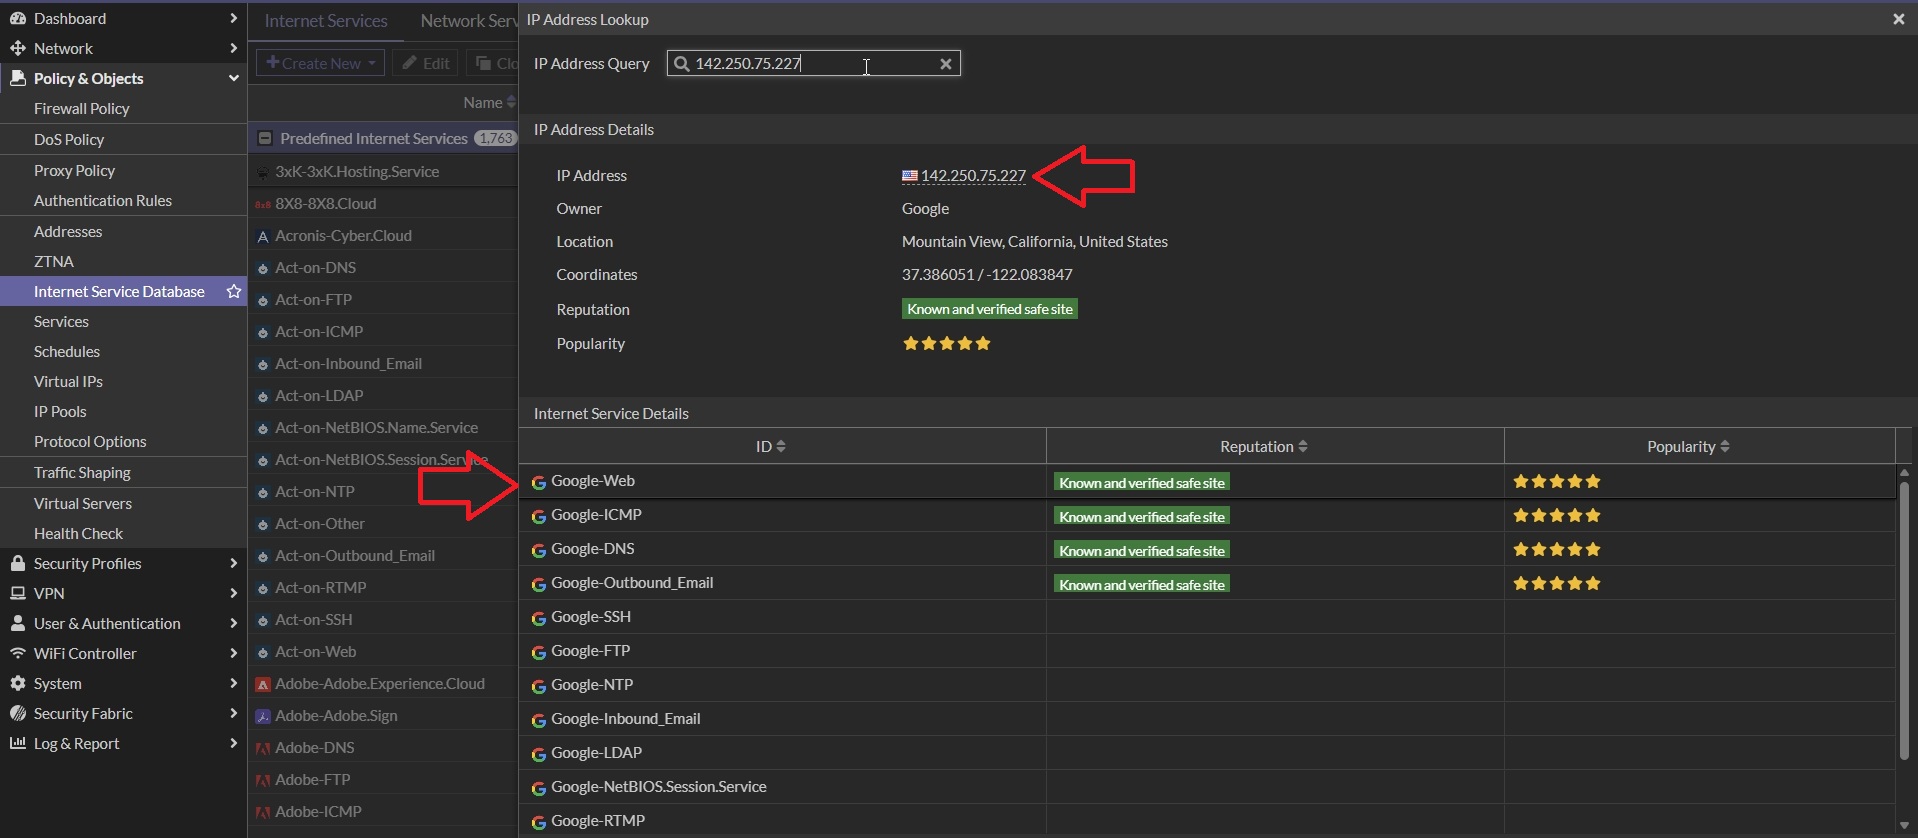 As a result, the FortiGate will not perform a redirection to the Google authentication page.
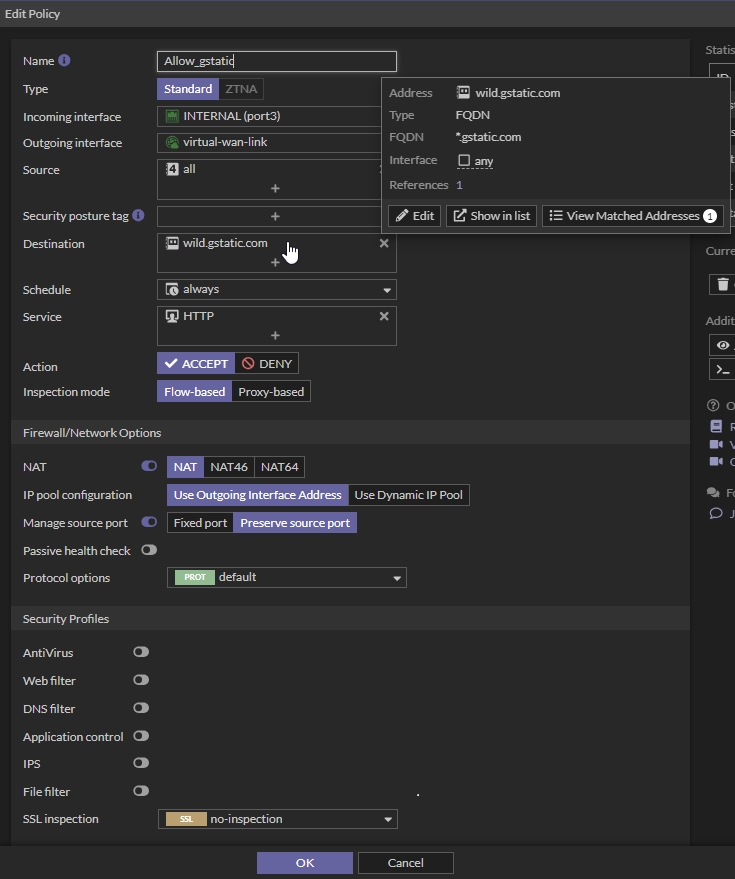
To overcome this issue, create an FQDN address object for *.gstatic.com and create a third policy which will be placed above the 'GOOGLE EXEMPT SAML and DNS' with the destination set to the FQDN object. Make sure that the policy is not exempt from the captive portal.
Example:
 Important note:
This gstatic policy MUST have services set to HTTP: otherwise, the Google authentication portal will become unresponsive.
This happens because a JavaScript resource that is handling the portal interactions is being fetched from gstatic.com.
By setting the service to 'ALL', for instance, the request from the client to https://www.gstatic.com/portal.js will be blocked from the captive portal.
Related article:
Technical Tip: Configure SAML SSO for WiFi SSID over Captive Portal with Azure AD as IdP | 




