Troubleshooting Tip: FortiGate is using management interface IP to NAT outgoing traffic via internet interface
| Description | This article describes the FortiGate behavior when outgoing traffic exits via an interface without an assigned IP, and the policy has 'Use Outgoing Interface Address' as NAT. |
| Scope | FortiGate. |
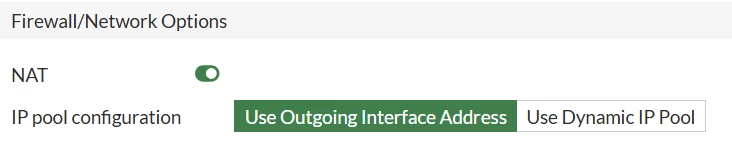
| Solution | When an interface is selected as the exit interface for the traffic, and 'Use Outgoing Interface Address' is used as the NAT behavior in the policy:
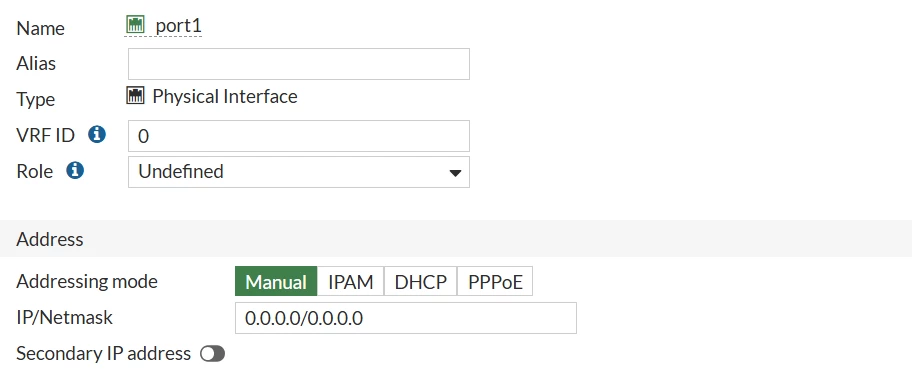
But the interface does not have an assigned IP address:
FortiGate will try to NAT using a seemingly random or management IP:
2026-01-07 18:45:08 id=65308 trace_id=102 func=__ip_session_run_tuple line=3406 msg="SNAT 10.176.22.31->192.168.1.99:62099"
In this case, the IPPOOL IP-192.168.1.99 is from the default addressing of the management interface, but in case the management interface is configured without an IP address (0.0.0.0/0), the next interface will be used. It is possible to verify the interface selection order using the command: diagnose netlink interface list.
FG200F-7 # diagnose netlink interface list if=lo family=00 type=772 index=1 mtu=16436 link=0 master=0 if=dummy0 family=00 type=1 index=2 mtu=1500 link=0 master=0 if=mgmt family=00 type=1 index=3 mtu=1500 link=0 master=0 if=ha family=00 type=1 index=4 mtu=1500 link=0 master=0 if=nturbo_rx family=00 type=1 index=5 mtu=1500 link=0 master=0 if=nturbo_tx family=00 type=1 index=6 mtu=1500 link=0 master=0 if=port1 family=00 type=1 index=7 mtu=1500 link=0 master=0
Excluding the software interfaces, the first in selection order is mgmt, thus the IP of the mgmt interface will be used.
A similar behavior and example of this is when the traffic is traversing through an IPsec tunnel. By default, the overlay interface of the IPsec VPN has no assigned IP interface. Further discussion and samples can be found in the articles below: Technical Tip: Implement Source-NAT for IPsec interface Technical Tip: Source IP for self-originating IPsec tunnel traffic |