

lmassip
Staff
Staff
September 9, 2026

Troubleshooting Tip: FortiGate in HA cluster repeatedly logs out of FortiGate Cloud shortly after registration

  • September 9, 2026
  • 0 replies
  • 814 views

Description

This article describes a scenario where a FortiGate in an HA cluster registers to FortiGate Cloud and automatically gets logged out after a second.

  • The FortiGate registers to FortiGate Cloud and loses the registration almost immediately.

  • diagnose test application forticldd 1 alternates between acct_st=OK (with account ID) and acct_st=Logged Out (empty acct_id):


diagnose test application forticldd 1
System=FGT
Platform=FG4H0F
Connection vdom: root, id=0, ha=primary.
acct_id=test@fortinet.com
acct_st=OK


diagnose test application forticldd 1
System=FGT
Platform=FG4H0F
Connection vdom: root, id=0, ha=primary.
acct_id=
acct_st=Logged Out


Debug  (diagnose debug application forticldd -1) shows a successful activation followed a few seconds later by a backend response reverting the device to local management.

Scope

FortiGate.

Solution

Root cause:

Only the primary is provisioned to the FortiGate Cloud account. The secondary is not.
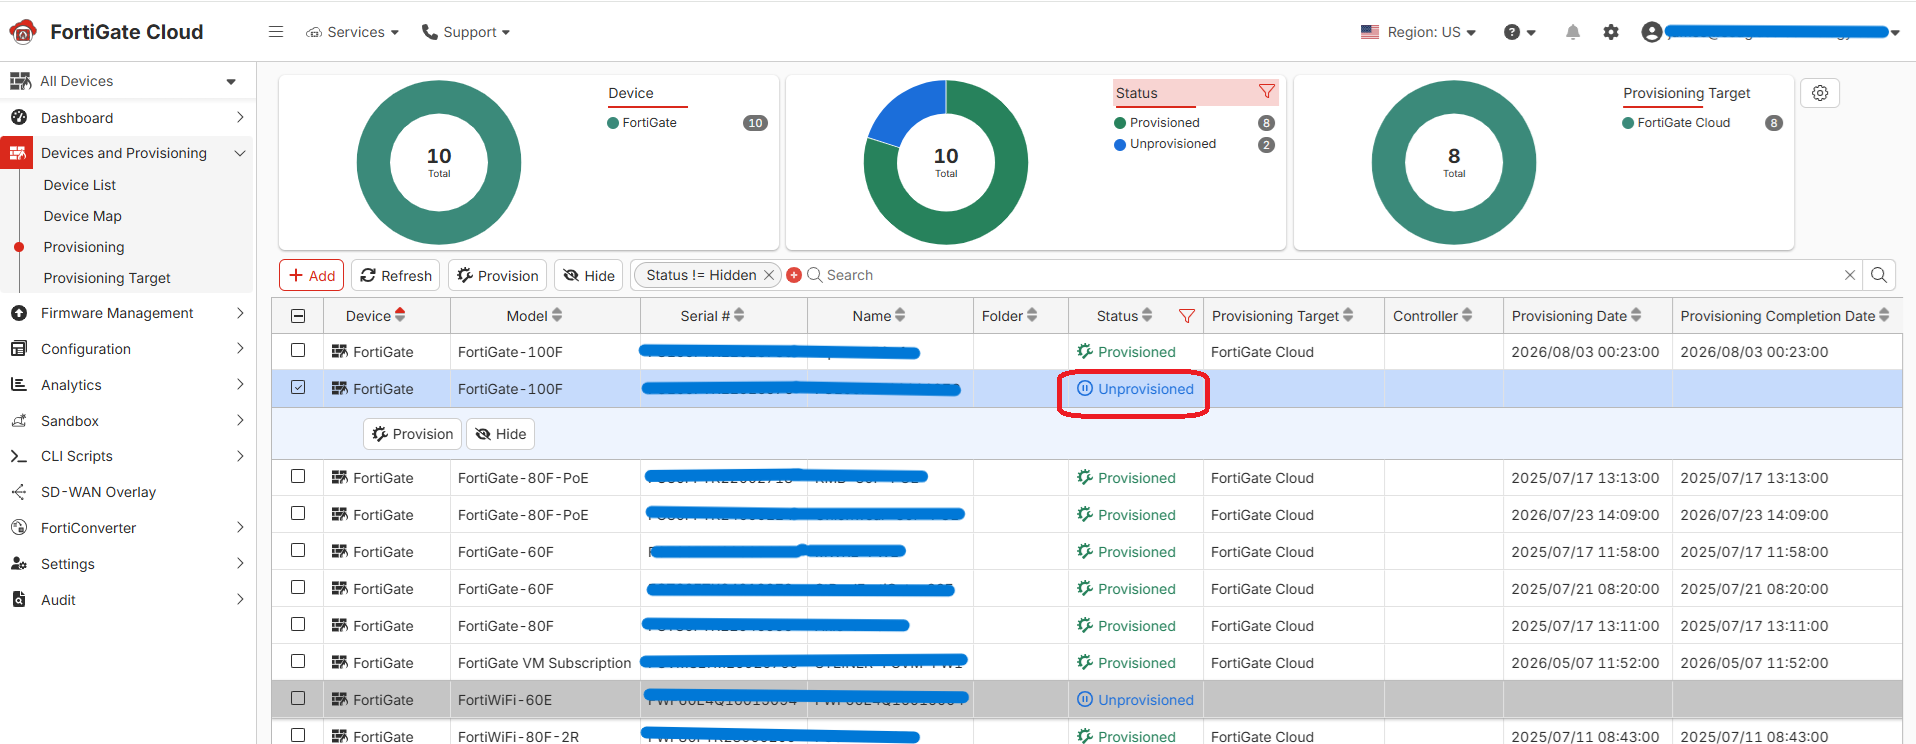
For an HA pair, FortiGate Cloud requires that all cluster members are provisioned to the same FortiGate Cloud account before activation is performed on the primary unit. When activation runs on the primary while the secondary is missing from the account, the backend detects an incomplete cluster record and instructs the unit to revert to local management.

In the FortiGate Cloud portal, check under Provisioning whether both the primary and secondary serials are listed under the same account. In this scenario, only the primary appears.

32da1dc3.png


Go to Provisioning, select the secondary unit, and select Provision. Confirm both serials are listed under the same FortiCloud account.

FortiGate devices can be also be provisioned using a FortiCloud Key and FortiCloud Inventory. Refer toCloud provisioning for more details.

The FortiCloud key can only be added once. If the key added previously was deleted, it cannot be re-used or re-added.

To fix the issue, open a FortiCare Ticket with the 'Customer Service' type to request to re-generate the FortiCloud key. Refer to Customer Service Tip: How to create a ticket for Fortinet TAC.

Once both members are provisioned, re-activate FortiGate Cloud.

Verification:

After both members are provisioned and FortiGate Cloud is re-activated, wait a few minutes (the original revert happened only seconds after activation) and re-run the command below to confirm acct_st stays at OK rather than reverting to Logged Out:

diagnose test application forticldd 1


Related Article:

Technical Tip: Activate FortiCloud account in a FortiGate High Availability cluster

    Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
    Thought Leadership. Security Summit. Thursday, October 8th. Disney's Grand Californian Hotel & SPA, Anaheim, CA.

