There are a few solutions to overcome this issue with an unrated category for IP address based access. Â Create a static URL filter to exempt that particular URL, as follows: Web Filter -> Default (relevant profile that applied to policy) -> Static URL Filter -> URL Filter.
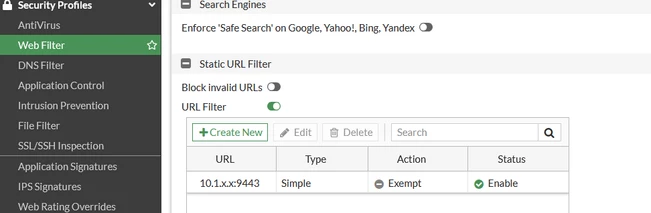
  To configure URL filters in the CLI:
config webfilter urlfilter
edit <ID>
    config entries
      edit 1
        set url <url>
        set referrer-host <url>
        set type {simple | regex | wildcard}
        set action {block | allow | monitor | exempt}
        set status {enable | disable}
     end
   end
end
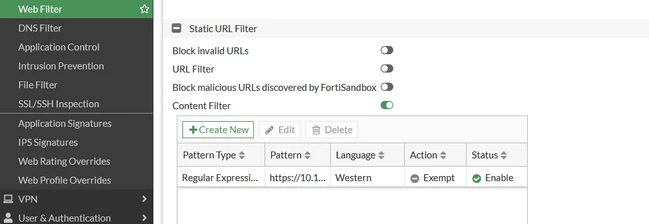
Create a regular expression and exempt that URL if the static URL filter does not work: Web Filter -> Default(relevant profile that applied to policy) -> Static URL Filter -> Content Filter.
   To configure web content filter in the CLI:
config webfilter content
edit <ID>
set name "webfilter"
config entries
edit <URL Name>
set pattern-type regexp
set status enable
set lang western
set score 10
set action exempt
next
end
next
end
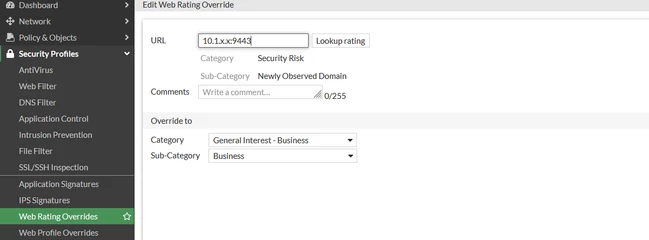
Move the URL to another category that allows connection (such as moving the URL to General Interest -> Business -> Business-> Web rating Override -> create new -> paste URL in lookup rating and override to relevant allowed category.
   Related articles: Technical Tip: How to allow a website with an Unrated Category Technical Tip: How to configure Web Rating Overrides for specific web sites using the FortiGate |