Symptoms when starting a packet capture in the GUI of a FortiGate that indicate an issue with the capture is present: Packet capture will not start. Packet capture started showing only a few packets captured and stopped working. Packet capture started downloading, showing 0 bytes.
Before starting with the troubleshooting process, first, verify whether NPU offloading is disabled on the relevant firewall policy; otherwise, just the first packets will be shown, and after the traffic is offloaded, it will appear as if the sniffer is no longer working:
config firewall policy
    edit <number of the firewall policy>
        set auto-asic-offload disable
    end
For more information about this, see Technical Tip: FortiGate - Disable Hardware Acceleration.
Possible troubleshooting process, starting from the solution: if the issue persists, move to the next solution:
Solution 1: Change to a different browser, clear the cache of the browser, and use a private window.
How to clear the browser cache:
Open browser settings: Navigate to the browser settings menu (usually with three dots or lines in the top right corner). Find 'Clear browsing data': Select the option related to clearing browsing history or data. Choose time range: Select 'All time' to clear the entire cache. Select 'Cache': Ensure the 'Cache' option is checked. Select 'Clear data': Confirm and clear the browser cache.
Solution 2: Kill the HTTPSD using the below command (have local access in case the HTTPSD daemon has an issue):
diagnose sys process pidof httpsd
167
8607
diagnose sys kill 11 167
diagnose sys kill 11 8607
diagnose sys process pidof httpsd
The alternative command can be used below:
fnsysctl killall httpsd
Solution 3: Delete all the sniffers currently in the GUI.
Solution 4: Delete all the sniffers in the FortiGate using the command line, as some sniffers are not showing under the GUI when the sniffer has been done using CLI previously. Use the command below:
config firewall sniffer
    show
        delete 1,2,3,4....
end
Solution 5: Format the log disk. This action will wipe the local disk logs and ensure that FortiAnalyzer or any other logging store system is available. Use this KB article: Technical Tip: Standard procedure to format a FortiGate Log Disk, log backup from disk.
After following the steps in the article above to format logs, check whether the issue persists.
Solution 6: Follow the following KB article to scan the disk, keep in mind the command highlighted in the article will require a FortiGate reboot: Technical Tip: File System check recommended message.
If none of the above solutions fixed the issue, raise the case with Support for further investigation.
Notes: When the following error is displayed while running a diagnostic sniffer packet:
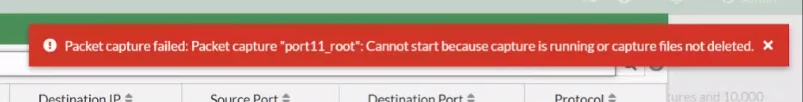
Run the following command to end the sniffer sessions stuck on the FortiGate, as mentioned previously in step 4:
config firewall sniffer
    show
    delete 1,2,3,4....
end
Packet capture function, also called 'Diagnose' after version 7.2, can be found under 'Network' -> 'Diagnose'. This is not visible under the Global VDOM when FortiGate is running a multi-VDOM environment, as shown in the screenshot below.
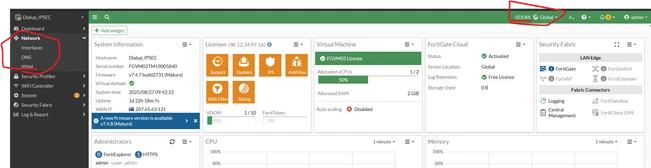 This is expected behavior because the global VDOM does not process traffic in a multi-VDOM environment. Switch to the traffic VDOM to access the Diagnose function. 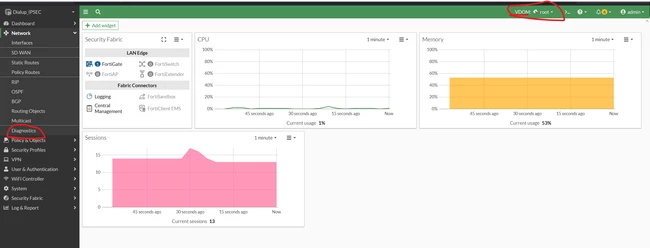 | 





