JordAnge
Staff
Staff
February 9, 2026

Troubleshooting Tip: FortiGate does not send the Certificate chain (Handshake_Type=Certificate) on connection to VIP in FlowMode

  • February 9, 2026
  • 0 replies
  • 444 views
Description

This article describes the use of multiple certificates in an SSL profile in replace mode, allowing multiple sites to be deployed on the same protected server IP address.

The SSL inspection is going to be based on matching the SNI in the certificate.


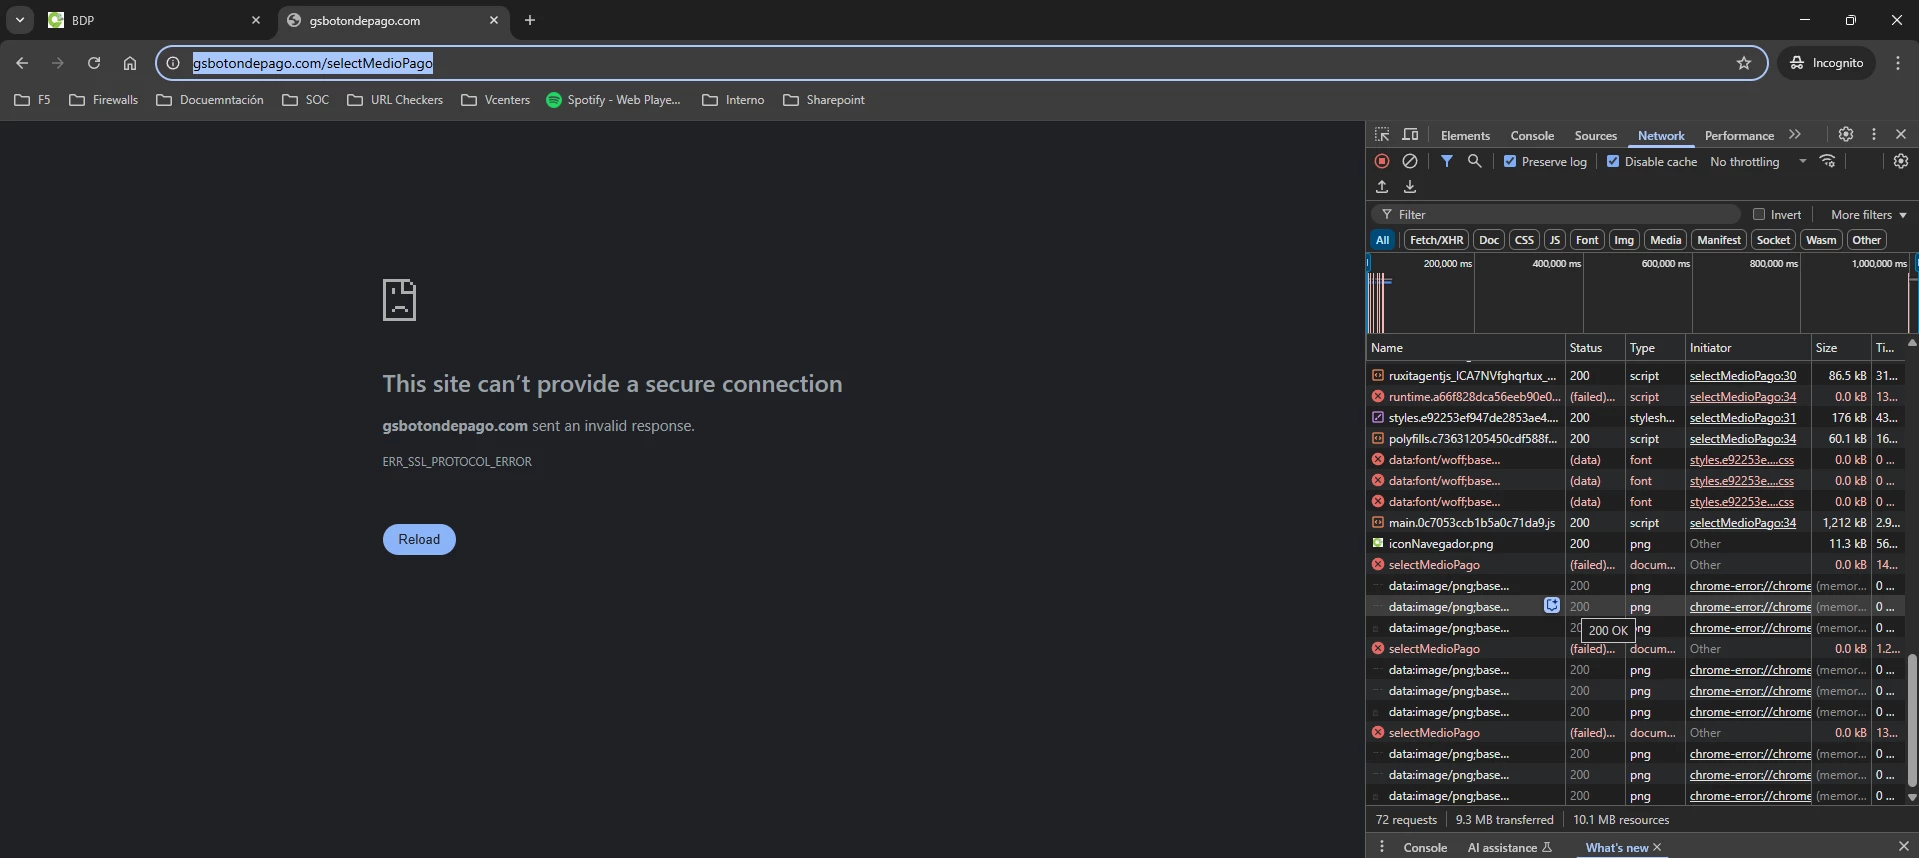
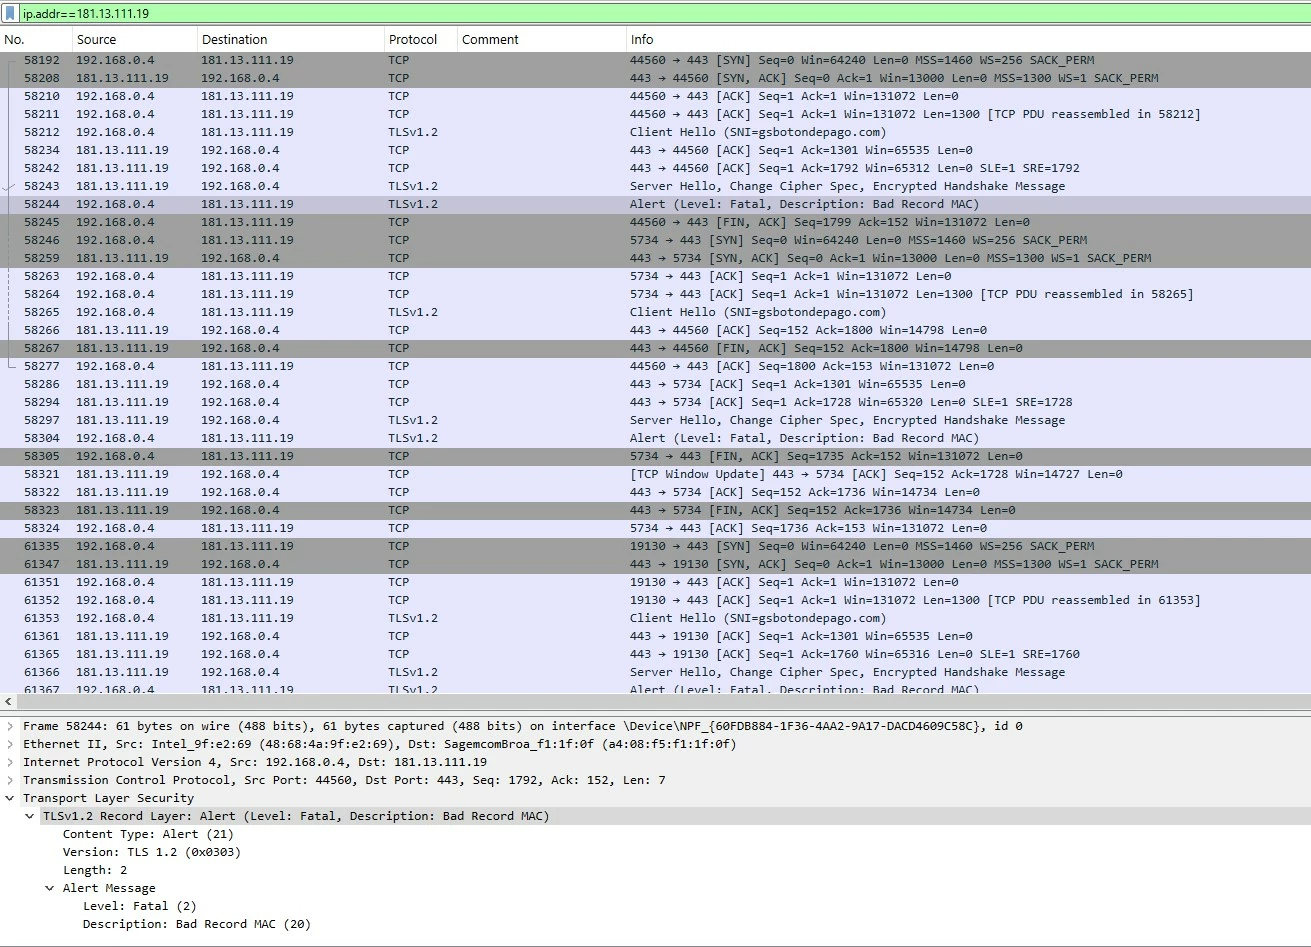
But in this scenario, most of the TLS/SSL connection fails against a VIP ('NAT-181.13.111.19:443/TCP').

Scope

FortiOS v7.2.10,build1706.

IPS Attack Engine 7.00356.

Solution

Configuration:


config firewall vip
    edit "NAT-181.13.111.19:443/TCP"
        set comment "VS-PCI"
        set extip 181.13.111.19
        set mappedip "172.16.0.111"
        set extintf "Vlan 150"
        set nat-source-vip enable
        set portforward enable
        set extport 443
        set mappedport 443
    next
end


config firewall ssl-ssh-profile
    edit "SSL Inspection test"
        set comment "SD-120582"
            config https
                set ports 443
                set status deep-inspection
            end
            ...
        set server-cert-mode replace <------
        set server-cert "pagar.rapipago.com.ar" "tokenizacion_gire_com" "star_api_gire_com" "gsbotondepago_com" <------
        set ssl-negotiation-log enable
        set ssl-server-cert-log enable
        set ssl-handshake-log enable
    next
end


config firewall policy
    edit 637
        set name "PCI"
        set srcintf "virtual-wan-link"
        set dstintf "Vlan 60"
        set action accept
        set srcaddr "IPs-DYNATRACE" "BORRAR-IPPUBLICA" "borrar-ippulboca02" "borrar-03"
        set dstaddr "NAT-181.13.111.19:443/TCP"
        set schedule "always"
        set service "HTTPS" "HTTP"
        set utm-status enable
        set ssl-ssh-profile "SSL Inspection test"
        set ips-sensor "IPS_PCI-SIGNS"
        set logtraffic all
        set auto-asic-offload disable
        set np-acceleration disable
    next
end


TLS-Handshake fails:

 CSS-11088563__ERR_SSL_PROTOCOL_ERROR (1).png


TLS-Fails.jpg


Expected behavior: Gets the 'Certificates' from FortiGate, based on the SNI connection requested by Client.


Solution: Upgrade IPS engine to build v7.0364.

    Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
    Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!