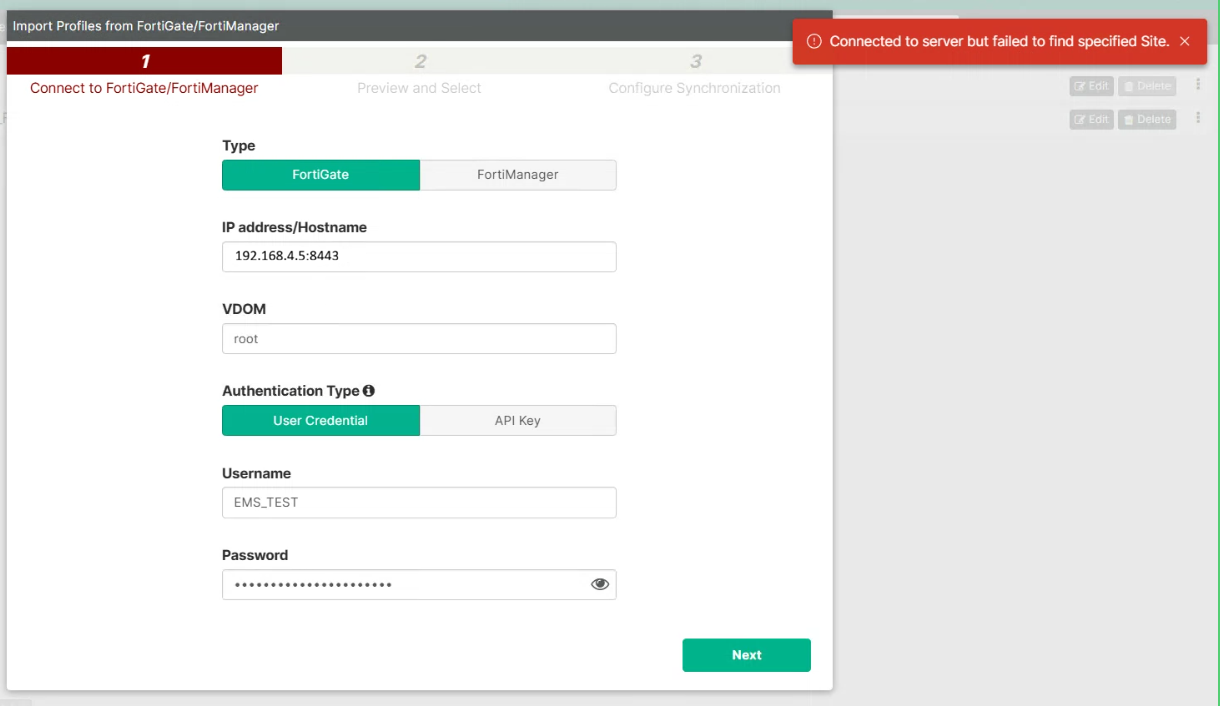
Importing a Web Filter profile from FortiOS requires HTTPS access on the FortiGate interface.
FortiClient EMS displays the error message 'Connected to server but failed to find specified Site' if HTTPS access is not enabled on the FortiGate interface facing the FortiClient EMS or if the configured HTTPS port does not match the FortiGate HTTPS administrative port.
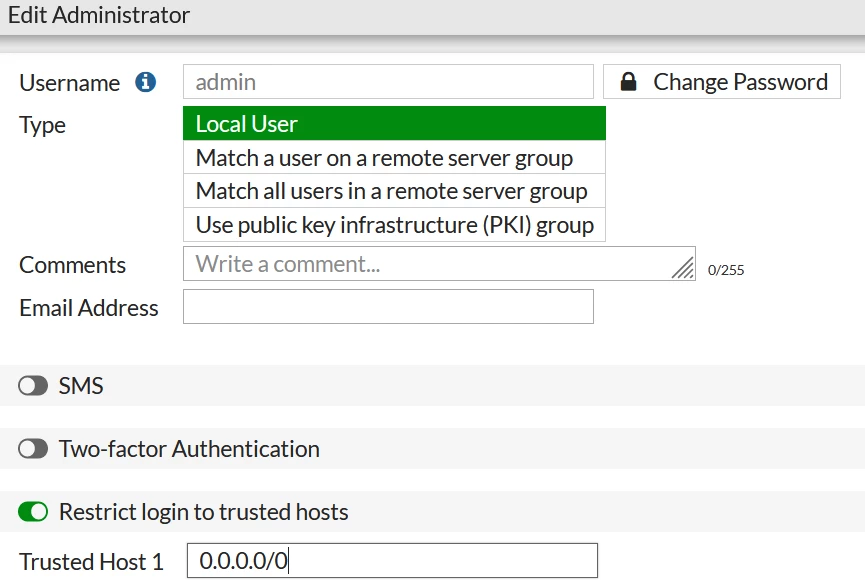
In cases where trusted hosts are configured for the user, it is necessary to add the EMS IP to the trusted host list.
To identify the trusted hosts, go to System -> Administrators, select the administrator account to edit, check Restrict login to trusted hosts is enabled, and add, if it is necessary, the EMS IP addresses.
To do this in the CLI, run the following:
config system admin
    edit <administrator-name>
        set trustedhost1 <ip and subnet>
end
The FortiClient EMS is using the HTTPS admin port configured on the FortiGate to import the profile. Go to System -> Settings -> Administrator Settings and check the HTTPS port. 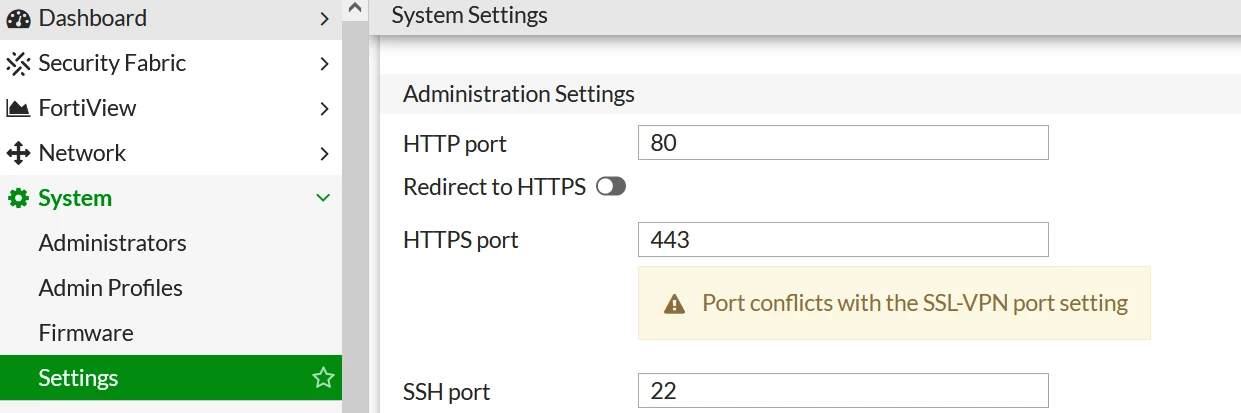 To do this in the CLI, run the following: config system global
set admin-sport <port>
end
Related article:
Importing a Web Filter profile from FortiOS or FortiManager |