jprokic
Staff
Staff
August 21, 2024

Troubleshooting Tip: FortiGate blocks Apple Product Updates due to an untrusted certificate

  • August 21, 2024
  • 0 replies
  • 7521 views
Description This article describes how to resolve an issue where FortiGate blocks Apple Product Updates due to an untrusted certificate.
Scope FortiGate, Apple devices.
Solution

When installing FortiGate into the network, Apple devices (such as iPhones and iPads) may cease updating properly. 
For update purposes, the Apple devices use certificates not trusted by FortiGate, by default.

Even though all Apple-related FQDNs are exempted from SSL deep inspection, they are still being dropped by the certificate inspection which, by default, blocks traffic with untrusted certificates.


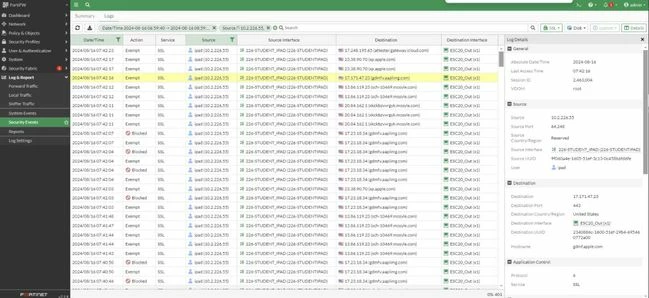
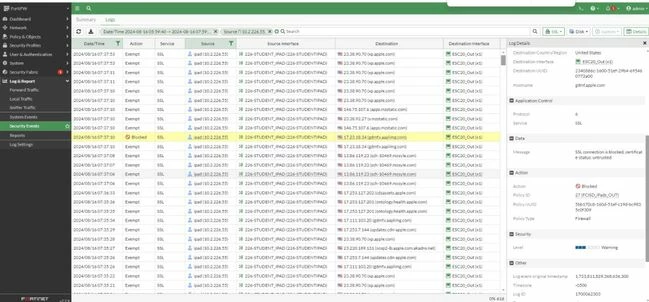
The Security Events SSL logs show the following:

After traffic is exempted from the Deep SSL inspection, it is blocked by the certificate inspection:
 

Apple_Cert_Update_I.JPG


The solution:


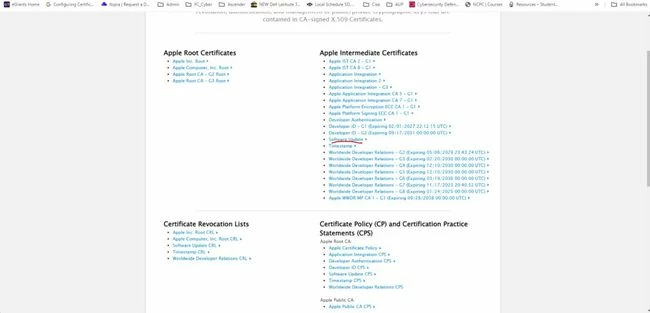
  1. Download the Apple Root certificate and Software Update certificate from the Apple website: https://www.apple.com/certificateauthority/


Apple_Cert_Update_IV.JPG


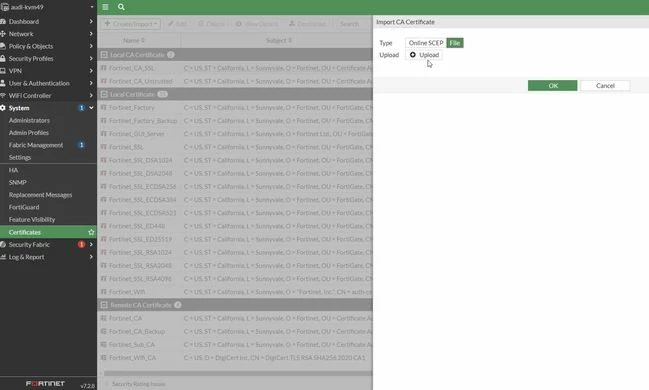
  1. Upload those newly downloaded certificates to FortiGate as a CA certificate:

    System -> Certificates -> Create/Import -> CA Certificate -> File -> Upload.


CA_Cert_Upload.jpg


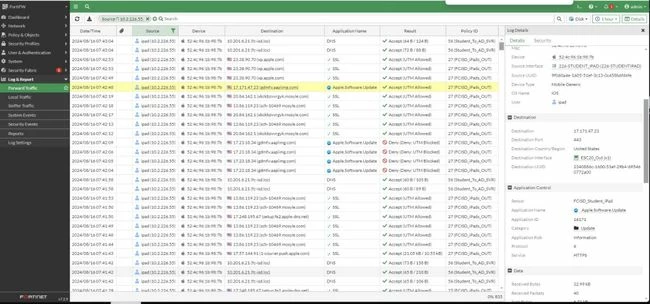
  1. After FortiGate has corresponding CA certificates from Apple, it trusts the 'update' traffic and allows it.
    Both Forward Traffic logs and Security Events logs confirm it:


Apple_Cert_Update_II.JPG
Apple_Cert_Update_III.JPG


    Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
    Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!