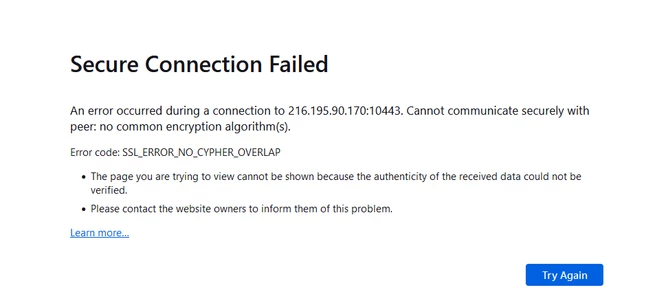
| From the config file, under SSL VPN settings, the server cert is 'Fortinet_Factory'. GortiGate-1500D is a CP8 platform and the 'Fortinet_Factory' is 1024-bit. FortiOS was upgraded to OPENSSL 3.0.2 since v7.2.1 0752141, the 'Fortinet_Factory' does not fit OPENSSL 3.0 requirement, which causes the SSL handshake to fail. Debugs: FortiGate-1500D # 2022-12-02 13:22:58 [357:root:2]allocSSLConn:306 sconn 0x7f8ba56b1800 (0:root)
2022-12-02 13:22:58 [357:root:2]SSL state:before SSL initialization (10.10.170.16)
2022-12-02 13:22:58 [357:root:2]SSL state:fatal decode error (10.10.170.16)
2022-12-02 13:22:58 [357:root:2]SSL state:error:(null)(10.10.170.16)
2022-12-02 13:22:58 [357:root:2]SSL_accept failed, 1:unexpected eof while reading
2022-12-02 13:22:58 [357:root:2]Destroy sconn 0x7f8ba56b1800, connSize=0. (root)
2022-12-02 13:22:59 [358:root:2]allocSSLConn:306 sconn 0x7f8ba56b1800 (0:root)
2022-12-02 13:22:59 [358:root:2]SSL state:before SSL initialization (10.10.170.16)
2022-12-02 13:22:59 [358:root:2]SSL state:before SSL initialization (10.10.170.16)
2022-12-02 13:22:59 [358:root:2]no SNI received
2022-12-02 13:22:59 [358:root:2]client cert requirement: no
2022-12-02 13:22:59 [358:root:2]SSL state:fatal handshake failure (10.10.170.16)
2022-12-02 13:22:59 [358:root:2]SSL state:error:(null)(10.10.170.16)
2022-12-02 13:22:59 [358:root:2]SSL_accept failed, 1:no shared cipher
2022-12-02 13:22:59 [358:root:2]Destroy sconn 0x7f8ba56b1800, connSize=0. (root)
2022-12-02 13:22:59 [359:root:2]allocSSLConn:306 sconn 0x7f8ba56b1800 (0:root)
2022-12-02 13:22:59 [359:root:2]SSL state:before SSL initialization (10.10.170.16)
2022-12-02 13:22:59 [359:root:2]SSL state:before SSL initialization (10.10.170.16)
2022-12-02 13:22:59 [359:root:2]no SNI received
2022-12-02 13:22:59 [359:root:2]client cert requirement: no
2022-12-02 13:22:59 [359:root:2]SSL state:fatal handshake failure (10.10.170.16)
2022-12-02 13:22:59 [359:root:2]SSL state:error:(null)(10.10.170.16)
2022-12-02 13:22:59 [359:root:2]SSL_accept failed, 1:no shared cipher Creating an SSL VPN cert on FortiGate will resolve the issue: config vpn ssl settings
set ssl-max-proto-ver tls1-2
set ssl-min-proto-ver tls1-0
set servercert "Fortinet_Factory"<-----
set algorithm low
set idle-timeout 14400 end To create a certificate, Go to VPN -> SSL VPN Settings -> Server Certificate -> Create Certificate -> Generate Certificate. 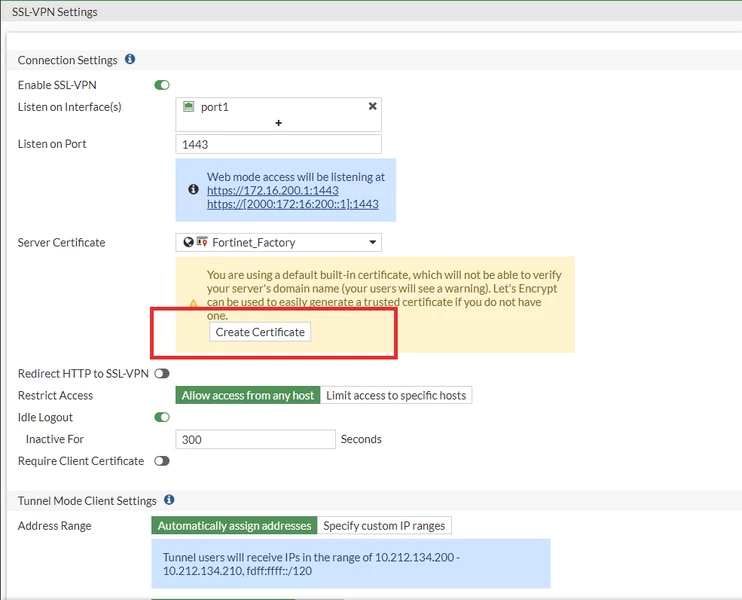
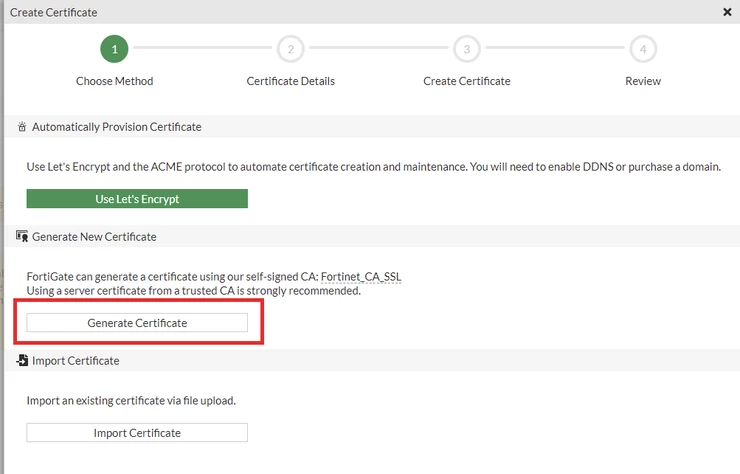
Once generated, replace the old SSL VPN certificate with the new one. |