



Troubleshooting Tip: FortiCloud connection failure
Description
Scope
FortiCloud, FortiGate.
Solution
- Check the Internet connectivity, and make sure that it can resolve the hostname 'logctrl1.fortinet.com'.
FGT # execute ping logctrl1.fortinet.com
PING logctrl1.fortinet.com (208.91.113.103)
- Check the DNS cache for 'logctrl1.fortinet.com'.
diagnose test application dnsproxy 7
vfid=0, name=logctrl1.fortinet.com, category=255, ttl=10386:9724:1138
208.91.113.103 (ttl=10412)
- Check the FortiGuard Log setting.
config log fortiguard setting
set status enable
set ssl-min-proto-version default
set source-ip 0.0.0.0
set interface-select-method auto
set upload-option 5-minute
set priority default
set max-log-rate 0
set enc-algorithm high
set conn-timeout 10
end
Note:
If there is no successful FortiCloud activation, it cannot adjust the settings above, and the status will be set to disabled.
- The following command can be used to check if the unit has a basic subscription or a paid subscription:
diagnose test application forticldd 2
Server: log-controller, task=0/10, watchdog is off
Domain name: globallogctrl.fortinet.net
Address of log-controller: 1
173.243.132.25:443
Source IP: 0.0.0.0
Source IP6: [::]
Statistics: total=357, discarded=8, sent=349, last_updated=45705 secs ago
http connection: is not in progress
Current address: 173.243.132.25:443
Source IP: 0.0.0.0:0
Calls: connect=1072, rxtx=1459
Current tasks number: 0
Account: name=account@domain.com, status=200, type=paid
Current volume: 0B
Current tasks number: 0
Update timer fires in 85698 secs
Daily volume reset timer fires in 32664 secs
- Check the FDS status for the account ID.
FGT # diagnose test application forticldd 1
System=FGT Platform=Fortigate_Model
Management vdom: root, id=0, ha=master.
acct_id=User_ID@company_id.com
acct_st=OK
FortiGuard log: status=enabled, full=overwrite, ssl_opt=3, source-ip=0.0.0.0
Centra Management: type=FGD, flags=000000bf.
active-tasks=0
- Validate the FortiCloud log state: The server status is 'Down'. For v7.2.3 and below:
diagnose test application miglogd 20
For v7.2.4 and above:
diagnose test application fgtlogd 20
Home log server:
Address: 208.91.113.241:514, st: down
oftp status: connecting
spos: 0, slen: 0
rpos: 0, rlen: 12
Alternative log server:
Address: 208.91.113.201:514, st: down
oftp status: connecting
spos: 0, slen: 0
rpos: 0, rlen: 12
Active log server: ALTER
Number of log task: 1024
Number of task in list: 1024
Debug zone info:
Server IP: 208.91.113.241
Server port: 514
Server status: down
Log quota: 102400MB
Log used: 224MB
Daily volume: 20480MB
FDS arch pause: 0
fams archive pause: 0
stats: total=95970, acked=0, discard=94946, rejected=0
Other examples:
diagnose test application forticldd 3
Debug zone info:
Domain:GLOBAL
Home log server: 173.243.132.171:514
Alt log server: 173.243.132.132:514
Active Server IP: 173.243.132.132
Active Server status: unknown
Log quota: 3145728MB
Log used: 0MB
Daily volume: 20480MB
fams archive pause: 0
APTContract : 0
APT server: 0.0.0.0:0
APT Altserver: 0.0.0.0:0
Active APTServer IP: 0.0.0.0
Active APTServer status: unknown
- Change the FortiGuard Log setting: Change 'set enc-algorithm high' from 'High' to 'default'.
- Validate the FortiCloud log state. The server status is 'UP'.
diagnose test application fgtlogd 20
Home log server:
Address: 208.91.113.194:514, st: up
oftp status: established
spos: 521, slen: 521
rpos: 24, rlen: 24
Alternative log server:
Address: 208.91.113.101:514, st: unknown
oftp connection haven't been established
Active log server: HOME
Number of log task: 0
Number of task in list: 0
Debug zone info:
Server IP: 208.91.113.194
Server port: 514
Server status: up
Log quota: 102400MB
Log used: 394MB
Daily volume: 20480MB
FDS arch pause: 0
fams archive pause: 0
stats: total=610774, acked=610774, discard=0, rejected=0 - From the FortiGate, test connectivity to TCP port 514 on the FortiGate Cloud servers using the Home log server IP obtained from the 'diagnose test application forticldd 3' command. A successful telnet confirms that TCP port 514 is open and reachable.
diagnose test application forticldd 3
Debug zone info:
Domain:GLOBAL
Home log server: 173.243.132.171:514
Alt log server: 173.243.132.132:514
Active Server IP: 173.243.132.132
...
FGT # execute telnet 173.243.132.171 514
Trying 173.243.132.171...
Connected to 173.243.132.171. <----- The console may freeze for a few moments, then drop the connection with the following message.
Connection closed by foreign host.
A failed telnet connection indicates that TCP port 514 is being blocked before reaching the FortiGateCloud server.
FGT # execute telnet 173.243.132.171 514
Trying 173.243.132.171...
Timeout!
Failed to connect to specified unit.
If there is no response from the server, change the outgoing interface.
config log fortiguard setting
set interface-select-method specify
set interface port1 <----- Specify the outgoing interface.
end
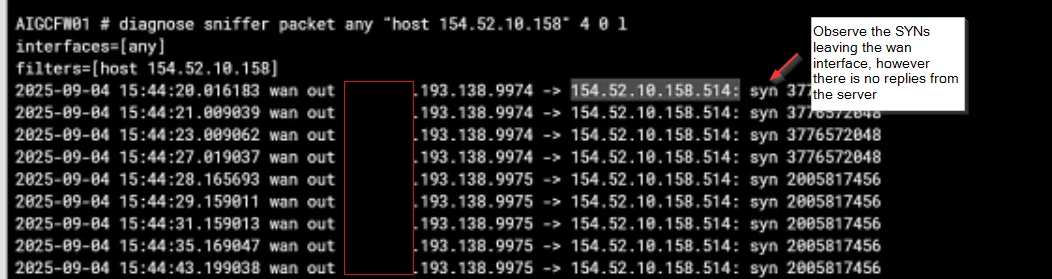
Also, the ISP might be blocking or filtering port 514 (image below). Contact the ISP to determine if port 514 is filtered or blocked.
- The FortiGate is using its routing table to route the self-originated traffic to FortiGate Cloud. If the configured default route does not allow Internet access, and the traffic must originate from the specific network to be routed, for example, via an IPsec tunnel, a source IP can be specified in the log settings in CLI, to allow the FortiGate unit to reach the FortiGateCloud servers:
config log fortiguard setting
set status enable
set ssl-min-proto-version default
set source-ip <IP-address (0.0.0.0 by default)>
set interface-select-method auto
end
Note: If SD-WAN is enabled, it is strongly recommended to configure the following command:
set interface-select-method sdwan
This source must be the IP address of some of the FortiGate interfaces. Other useful troubleshooting information can be collected using the following commands:
diagnose debug reset
diagnose debug console timestamp enable
diagnose debug application forticldd -1 or 255
diagnose debug enable
To disable the debug processes:
diagnose debug disable
When the debug output appears as shown below, it indicates that the connection between the FortiGate and the FDS servers is failing.
2026-02-12 14:39:22 [263] fds_svr_default_on_error: message-controller: Conn failes 1/1
2026-02-12 14:39:22 [286] fds_svr_default_on_error: message-controller: req-id=101, num_try=1, read=0, reason=4
2026-02-12 14:39:22 [109] fds_mctrl_update_done: update task was not successful.
To mitigate the issue, adjust the MTU value on the interface to an optimal setting.
config system interface
edit <interface_name>
set vdom "root"
set mtu-override enable
set mtu 1400
next
end
Verify system time and NTP sync.
Why:
Incorrect system time can cause SSL/TLS handshake failures, OCSP/CRL validation errors, and even logging/authentication problems.
Commands:
Check the current system time:
get system status | grep Time
Check NTP sync status:
diagnose sys ntp status
Recommendation:
Ensure NTP is configured and reachable:
config system ntp
set status enable
set ntp sync enable
set server "pool.ntp.org"
end
Note:
From the debug, if the following error 'FATAL: Status checking failed due to missing OCSP/CRL' was observed, try the following command to disable anycast:
config system fortiguard
set fortiguard-anycast disable
set protocol udp
set port 8888
end
After that, restart the FortiCloud process, and use the following command:
fnsysctl killall forticldd
Then, run these commands to restart the FortiCloud process. The first command will list the process ID, and replace the x's in the second command with the process ID:
diagnose sys process pidof forticldd
diagnose sys kill 11 xxx
Use the following commands to stop the debug, the console will take the keyboard input even while filling up:
diagnose debug disable <----- To disable.
diagnose debug reset <----- To reset the debug setup.
If the above commands do not resolve the issue and logs are still not sent to the FortiCloud, restart the FortiGate log daemon by running the commands below. The first command will list the process ID, and replace the x's in the second command with the process ID:
diagnose sys process pidof fgtlogd
diagnose sys kill 11 xxx
It is possible to use the IP information from the output in packet captures:
diagnose sniffer packet any 'host <IP from previous output>' 4 0 l
Note:
If all of the above settings are checked and the logs are still not received on the Cloud, make sure that FortiGate is running the latest firmware if using a Free Subscription with FortiGate Cloud.
Starting from February 28, 2025, a FortiGate without an active FortiGate Cloud subscription is required to upgrade to the latest firmware patch within 7 days of a new GA patch release, or FortiGate Cloud services will be paused for that device.
This will affect the cloud retention service, where logs will not be forwarded to FortiCloud until the device is updated to the latest firmware patch if using a Free FortiGate Cloud account: Technical Tip: Security enforcement change for FortiGates provisioned to FortiGate Cloud without active subscriptions.
Related articles:

