Peja
Staff
Staff
February 6, 2026

Troubleshooting Tip: FGSP cluster sandwiched between two cloud routers: achieving full ECMP load sharing across all members

Description

This article describes a situation in which an FGSP active-active cluster is placed between two cloud routers (full BGP mesh to all members), and ECMP is enabled. Traffic is consistently hashed to only one or two members, and when session-pickup-delay is enabled (non-default), new sessions are not visible to the other members for the first 30 seconds.

Scope
  • FortiGate running FortiOS v7.2/v7.4/v7.6 and later.
  • FGSP active-active cluster (not FGCP).
  • Cloud router ECMP topologies with full mesh to all cluster members.
  • Asymmetric routing paths.
  • session-pickup-delay enabled.
Solution

Observed behavior (before the fix):

  • ECMP hashed traffic to only 1 FortiGate consistently.
  • New TCP sessions were unknown to the other members for the first ~30 seconds (visible in flow traces).
  • Asymmetric return traffic during that window hit a member that had no session yet → drops or incorrect handling.


Fix: The root cause is that the session-pickup-delay is enabled. Disable the delay on all four cluster members:

 
config system ha
    set session-pickup enable
    set session-pickup-connectionless enable
    set session-pickup-expectation enable
    set session-pickup-nat enable
    set session-pickup-delay disable 
end
 

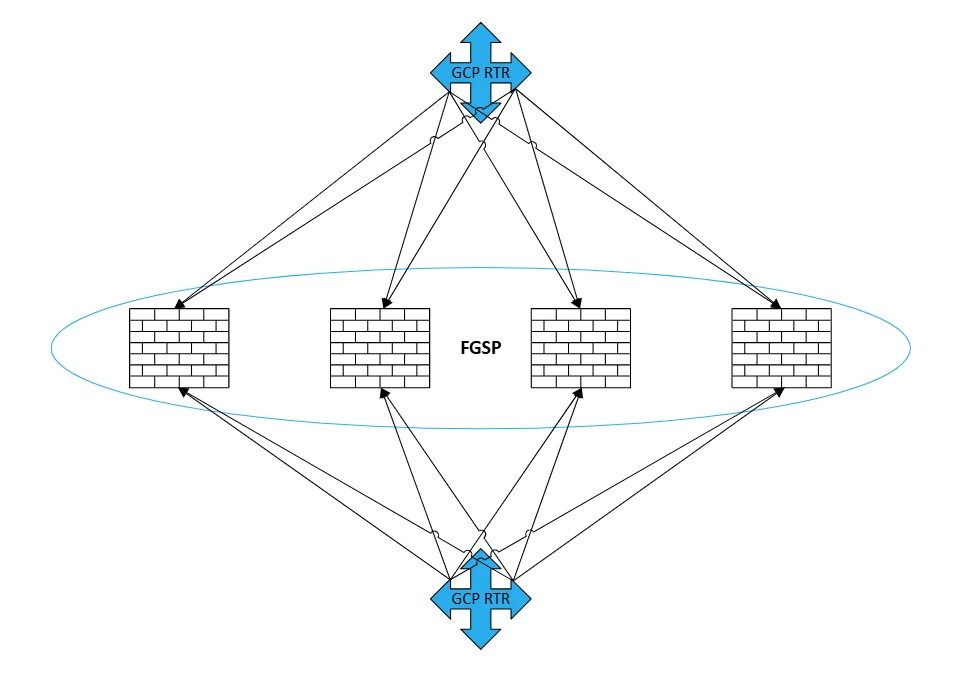
Topology:


FGSP active-active cluster sandwiched between two cloud routersFGSP active-active cluster sandwiched between two cloud routers


Non-working scenario (with session-pickup-delay enabled).

  1. New connection arrives → hashed to FortiGate #1.
  2. FortiGate #1 creates the session but waits 30 seconds before syncing to the cluster.
  3. Reply traffic returns → hashed to FortiGate #3 (normal ECMP).
  4. FortiGate #3 has no session yet → packet is dropped or handled incorrectly until the 30-second sync arrives.

Working scenario (after session-pickup-delay disable).

  1. New connection arrives → hashed to FortiGate #1.
  2. FortiGate #1 creates the session and syncs it immediately (first packet) to all other members.
  3. Reply traffic returns → hashed to FortiGate #3 (still normal ECMP).
  4. FortiGate #3 already knows the session → forwards correctly, no blind window.


After this change, asymmetric paths no longer cause drops, even if load distribution remains uneven due to ECMP hashing.


Note:

The session-pickup-delay option exists to reduce sync overhead for short-lived sessions. When enabled, the FortiGate that receives the first packet waits 30 seconds before syncing the TCP session. Short sessions that expire before 30 seconds are never synced.


Related documents:

Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
Thought Leadership. Security Summit. Thursday, October 8th. Disney's Grand Californian Hotel & SPA, Anaheim, CA.
Security Operations Summit: Modernize SecOps. Operate AI-Native.AMER: November 4 | 9:00 AM PST. India and SAARC: November 5 | 10:00 AM IST. EMEA: November 5 | 10:30 AM CET. APAC: November 5 | 11:00 AM SGT