| Consider the following example topology: 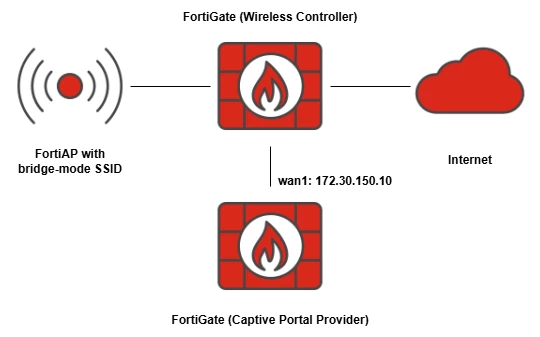
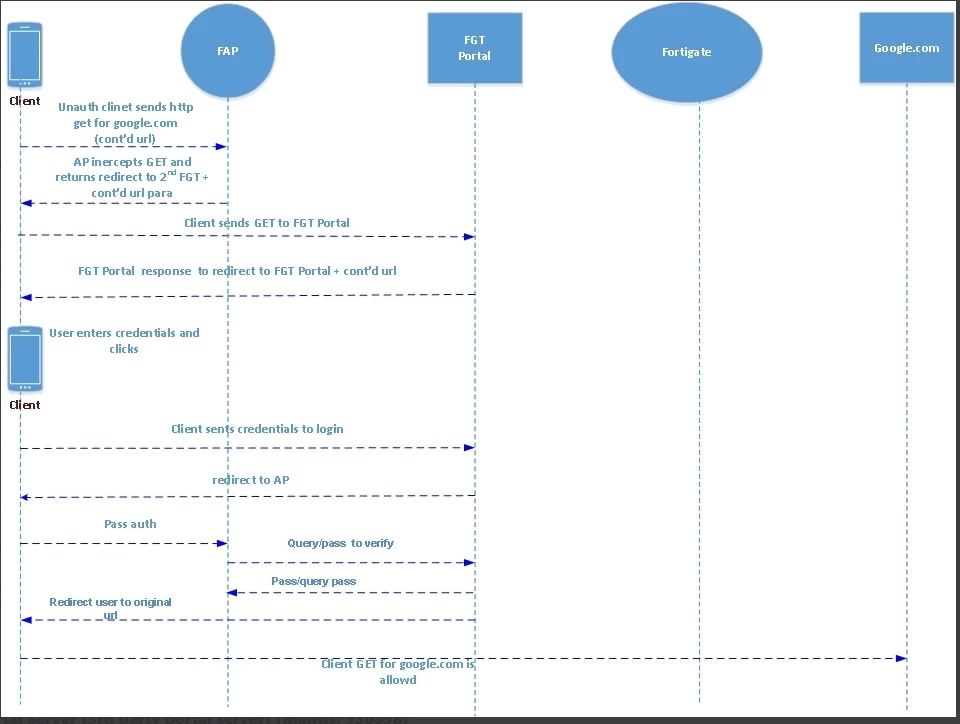
In the above diagram, the FortiGate (acting as the wireless LAN controller, or WLC) has pushed a bridge-mode SSID to the FortiAP that also has external captive-portal enabled. Notably, this SSID's external captive-portal URL is pointing to a secondary FortiGate whose listening IP address and port are http://172.30.150.10:1000. A sample CLI configuration for both the bridge-mode SSID as well as the secondary FortiGate's interface captive-portal settings can be found below. Take note that the CLI for this setup has changed after FortiOS v7.4.4, v7.6.0, and later, and so the before and after versions of the configuration are shown below. When a wireless client connects to the bridge-mode SSID on the FortiAP, the first HTTP(S) request from the client to the Internet will be intercepted by the FortiAP and redirected to the captive-portal FortiGate. The following is the generally expected workflow: - The client sends the first web request to reach the Internet.
- FortiAP intercepts the request and replies with an HTTP(S) redirect that includes the external captive-portal URL belonging to the captive-portal FortiGate.
- Client sends an HTTP GET request to the captive-portal FortiGate.
- Captive-portal FortiGate replies by pushing the captive portal login and/or disclaimer page back to the client.
- Client inputs credentials and/or accepts disclaimer as specified by the captive portal FortiGate.
- Captive portal FortiGate validates the credentials, then redirects the client back towards the original FortiAP authentication URL.
- Client connects to the FortiAP authentication URL to pass authentication.
- FortiAP queries the captive portal FortiGate (using the client's MAC and IP addresses as identifiers) to verify the authentication result.
- The captive-portal server sends the authentication result back to the FortiAP (allow/deny).
- If the authentication passes, then the FortiAP allows the client to send/receive traffic on the network. The FortiAP redirects the end-client to either the client's originally-requested URL or to the specified security-redirect-url.
 Sample Configuration: Bridge-mode SSID on FortiGate (v7.4.3 and earlier): config wireless-controller vap
edit "Example_WiFi"
set vdom "root"
set ssid "Captive Portal WiFi"
set security captive-portal <--- Open SSID with captive portal. set external-web "http://172.30.150.10:1000" <--- External captive portal URL of second FortiGate. set local-bridging enable <--- Enable bridge-mode for SSID.
set security-redirect-url "http://www.abcnews.com" <--- Redirect users to URL after captive portal.
set portal-type auth <--- Default setting, 'auth' specifically means FortiGate-based captive portal. set schedule "always"
next
end Bridge-mode SSID on FortiGate (v7.4.4, 7.6.0, and later): config wireless-controller vap
edit "Example_WiFi"
set vdom "root"
set ssid "Captive Portal WiFi"
set security open <--- Captive Portal is no longer handled in the security option. set external-web "http://172.30.150.10:1000" set local-bridging enable set captive-portal enable <--- New dedicated toggle for external captive-portal.
set security-redirect-url "http://www.abcnews.com" set portal-type auth set schedule "always"
next
end Secondary FortiGate captive-portal interface: config system interface
edit "wan1"
set vdom "root"
set ip 172.30.150.10 255.255.255.224
set allowaccess ping https ssh http telnet capwap
set type physical
set security-mode captive-portal
set security-groups "test"
next end Troubleshooting commands.
Debug log on FortiAP: FortiAP # cw_debug app fapportal 8 FortiAP # fapportal_diag -d sta Additional notes: - It is possible to combine external captive-portal authentication with other wireless authentication methods (such as WPA2-Personal) except for WPA2-Enterprise, WPA3-Enterprise, and OSEN.
- NAT should not be enabled between the end-client and the secondary FortiGate acting as the captive-portal server; otherwise, the authentication will not succeed. This is because the FortiGate only supports IP-based session authentication when used as a captive-portal server.
- Bridge-mode SSIDs only support external captive-portal authentication, whereas tunnel-mode SSIDs support both local (via the FortiGate) and external (via third-party) captive-portals.
- FortiOS and FortiAP v6.2.2 added support for true third-party captive portals for bridge-mode SSIDs, whereas before this, only another FortiGate could be used for the captive-portal server. This requires changing portal-type from auth to external-auth, and it also requires RADIUS authentication between the FortiAP and the third-party captive-portal provider.
Related documents: Configuring an external captive portal Technical Tip: Local Captive portal Bridge mode SSID Technical Tip: How to configure FortiGate Guest Wi-Fi Network using HPE Aruba ClearPass as external captive portal on Bridge mode SSID | 




