ssenthil
Staff
Staff
October 19, 2022

Troubleshooting Tip: DNS Filter profile: Redirect to Fortinet Secure DNS service portal shows error while 'Web Page Blocked!' page is displayed

  • October 19, 2022
  • 0 replies
  • 60466 views

Description

This article describes why the browser shows the error ‘Not secure’ or ‘Warning’ when the DNS Filter profile redirects to the ‘Fortinet Secure DNS service Portal’.
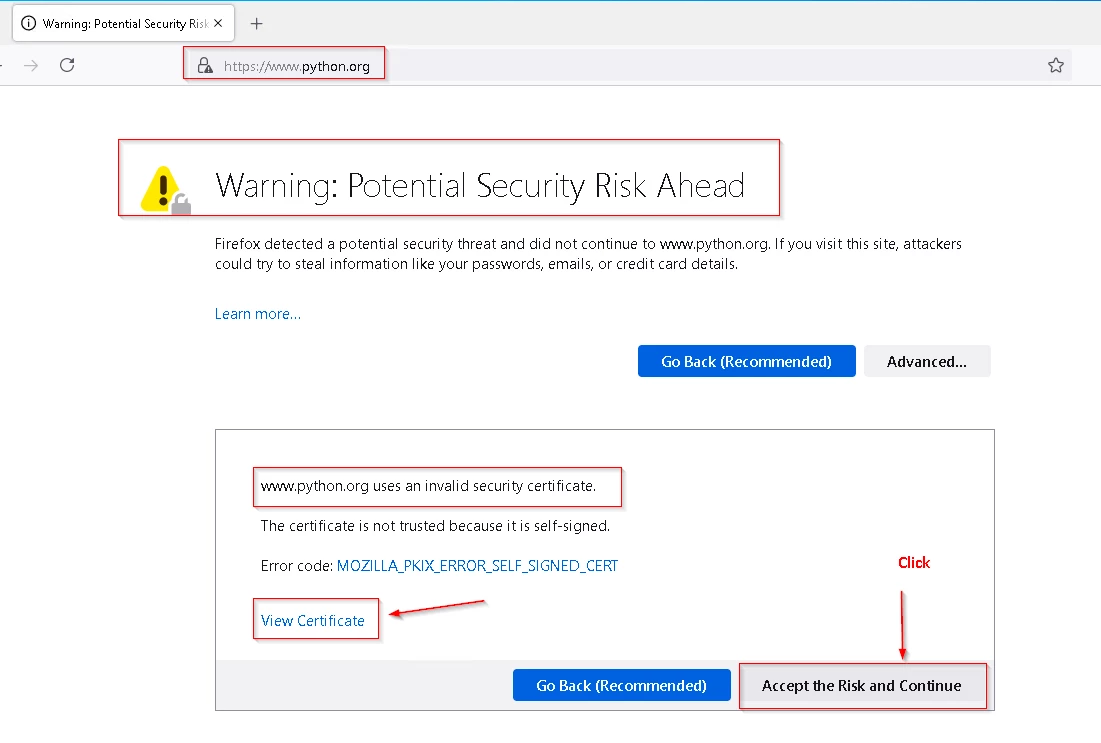
 

fortiraj_FTNT_0-1696270580848.png

Scope

FortiGate.

Solution

Sometimes, when users try to access a website, the following error may be seen:
'You have tried to access a web page which belongs to a category that is blocked.'.


If the browser tab has the label 'Fortinet Secure DNS Service Portal', one possible reason behind this is the FortiGate DNS filter.
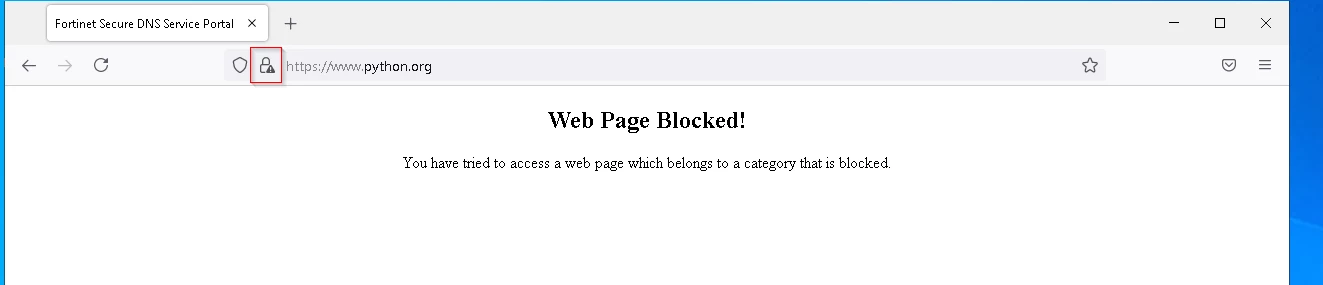
fortiraj_FTNT_1-1696270580849.png


To verify if it is blocked by the DNS filter, follow the steps below:
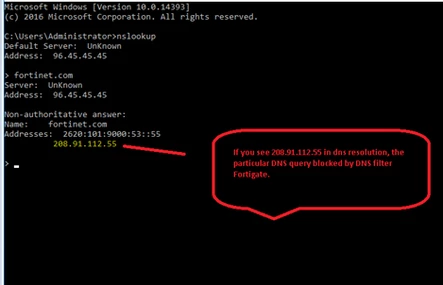
  1. From the PC exhibiting this behavior, go to the command prompt.

  2. Type nslookup.

  3. Enter the domain name. If the particular record resolves to FortiGate DNS block IP 208.91.112.55. It means, DNS filter block-action: redirect has replaced the DNS response.


ssenthil_1-1666202773766.png


The default behavior of the DNS filter profile for block action is redirect. It redirects the browser to the Fortinet Secure DNS service portal IP 208.91.112.55:


FortiGate-70F (default) # get
name                : default  
block-action        : redirect


When FortiGuard Category-Based Filter categories are set to Redirect to Block Portal, the DNS response will use this IP address in its response to the client. If the client is accessing the domain on a web browser, it will be redirected to the block portal page on this address.


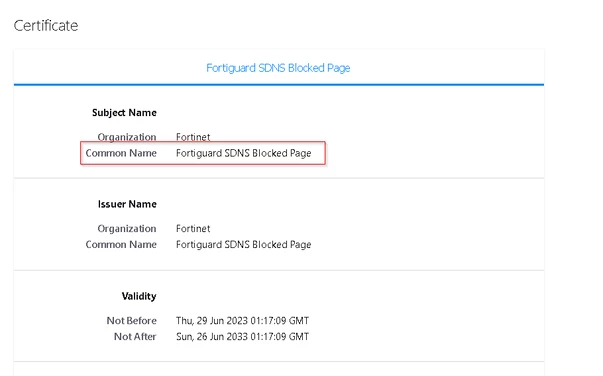
It is expected behavior that the browser cannot match the Common Name (CN) FortiGuard SDNS Blocked Page presented by the SDNS portal in the certificate against the blocked domain accessed by the user.


For example, when the user tries to access Python, which belongs to the FortiGuard-based category ‘Information Technology’, and it is blocked by the DNS filter profile, the browser will connect to 208.91.112.55 and receive a certificate with a CN that does not match the request it made.
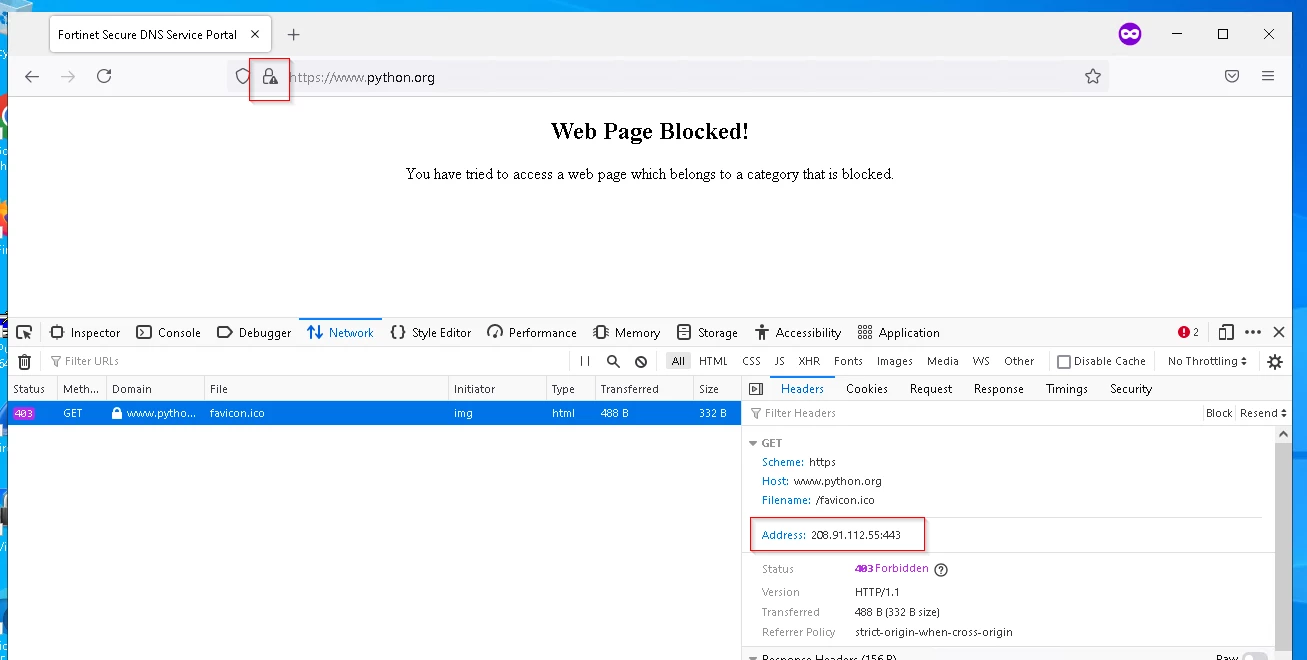
 

fortiraj_FTNT_2-1696270791163.png


certificate- FortiGuard SDNS blocked page.png


If the domain is not expected to be blocked, consider checking the expected action based on the DNS filter profile for the domain, or check the FortiGuard server connectivity by using the command diagnose debug rating.


More information on how to create static DNS filters to allow the traffic can be seen in Technical Tip: Static DNS filter to allow/block DNS queries.


More information on FortiGuard server connectivity can be found in Troubleshooting Tip: Resolving FDS Communication Issues (FortiGuard Distribution Servers).

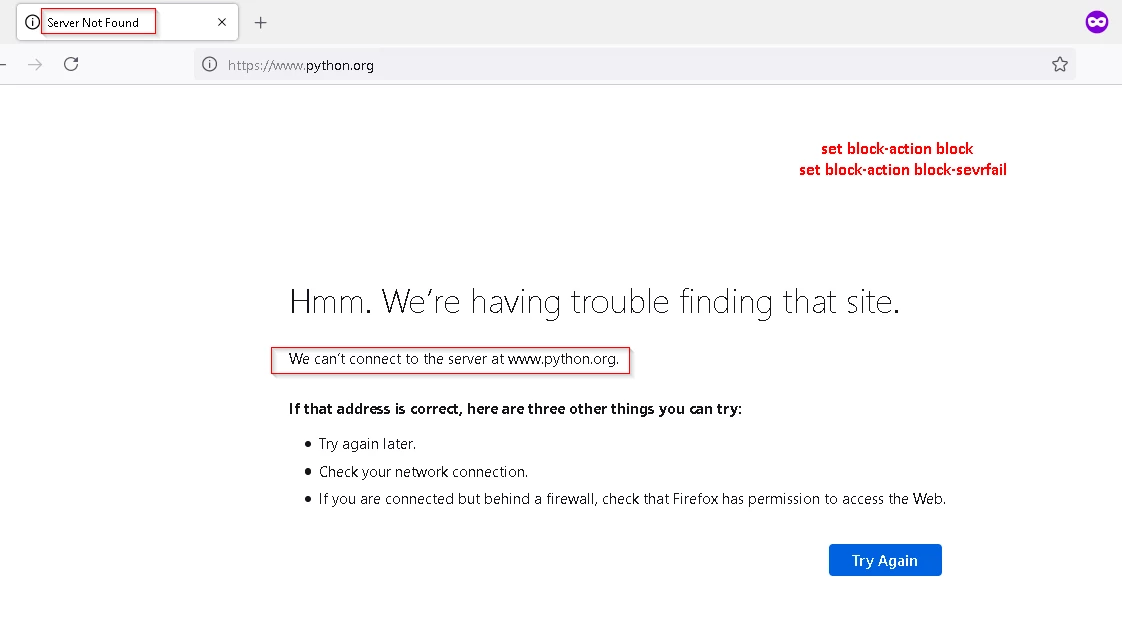
If there are concerns with presenting these errors/warnings to end-users, then consider other DNS Filter actions such as block or block-sevrfail. The downside is that users will not receive the 'Web Page Blocked' splash page and may be less clear on why the website could not be accessed. The browser tab will mention 'Server Not Found':

config dnsfilter profile
    edit <DNS profile name>
        set block-action redirect | block | block-sevrfail
block            Return NXDOMAIN for blocked domains.
redirect         Redirect blocked domains to SDNS portal.
block-sevrfail   Return SERVFAIL for blocked domains.


Set the block-action to Redirect.

config dnsfilter profile
    edit <DNS profile name
        set block-action redirect


fortiraj_FTNT_5-1696271421327.png


Workaround:

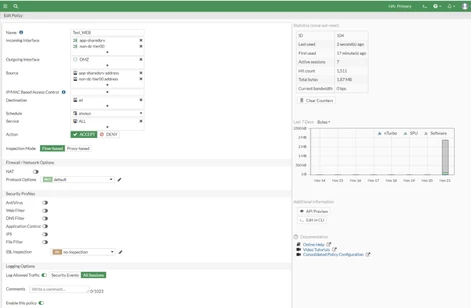
  • The DNS Filter is not enabled in the Firewall policy.


MicrosoftTeams-image (8).png


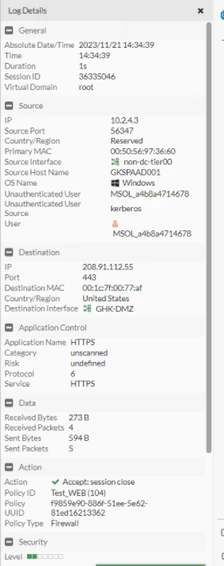
  • On the logs, the traffic matches the right policy and is 'Accepted'.


MicrosoftTeams-image (9).png


  • Change the configuration on the FortiGuard part:


config system fortiguard
    set fortiguard-anycast disable
    set protocol udp
    set port 8888
    set sdns-server-ip 208.91.112.220 173.243.140.53 210.7.96.5
    set sdns-options include-question-section
    set sdns-server-port 53
end


The 'Fortinet Secure DNS service Portal' will not block the web page.
Sometimes, while using port 8888 still gives an error, it is worth attempting to switch it over to 53.

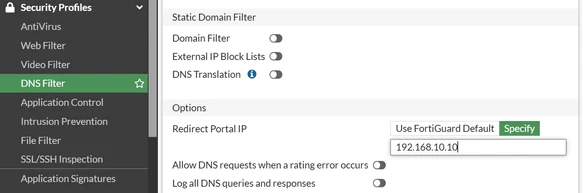
Users can use a customized redirect portal:

config dnsfilter profile
   edit <profile name>
       set redirect-portal 192.168.10.10
end


The IP 192.168.10.10 is the user's private web portal.


kb-02-14.PNG


For any specific website being blocked where the SDNS page is presented, verify the hostname cache with the following command on FortiGate. In the example below, the aajtak website has a DNS cache with an SDNS block page IP:

diagnose test application dnsproxy 13
208.91.112.55 (domain=aajtak-e4bc1-6cb21.firebaseio.com, ttl=86278)


For more DNS filter troubleshooting assistance, see Troubleshooting for DNS filter.


Related document:

Configuring a DNS filter profile

    Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
    Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!