The user cannot connect to a dial-up IPsec VPN with FortiToken and encountered the 'FortiClient Wrong Credentials EAP failed connecting' error.
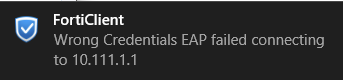
While successful when connecting without FortiToken. Another error that commonly appears is 'EAPPasswordError':


RADIUS authentication:
The setup is a dial-up IPsec VPN IKEv2 using RADIUS authentication, where FortiGate is the RADIUS client while the FortiAuthenticator is the RADIUS server.
Enable ‘Allow OTP for EAP-MSCHAPv2 Authentication with FortiClient’ on the RADIUS Service policy of FortiGate on the FortiAuthenticator to fix these errors.
 MSCHAP2 is a prerequisite of this setup.
Note: Similar error messages may also be observed when the user account is locked, the password is expired, or the authentication request is rejected by the external authentication server. If enabling this option does not resolve the issue, review FortiGate and authentication server debug logs to identify the exact cause of the rejection.
SAML Authentication.
The setup is a dial-up IPsec VPN IKEv2 using SAML authentication, where FortiGate is the SAML Service Provider (SP).
Verify the 'set user-name' and 'set group-name' settings under 'config user saml' to ensure that the assertion statements match the attributes configured on the SAML Identity Provider (IdP).
config user saml
    edit <name>
        set user-name <value>
        set group <value>
end
Alternatively, verify Attribute Name and AttributeValue from the SAML debug output.
diagnose debug application samld -1
diagnose debug enable
In the line beginning with 'samlp:Response ID', check the Attribute Name and AttributeValue for user-name and group-name to confirm a match with the values configured on the FortiGate.
Related articles:
| 




