



Troubleshooting Tip: DHCP Request from PC is not received when switch-controller-dhcp-snooping is enabled on FortiLink VLAN interface
Description
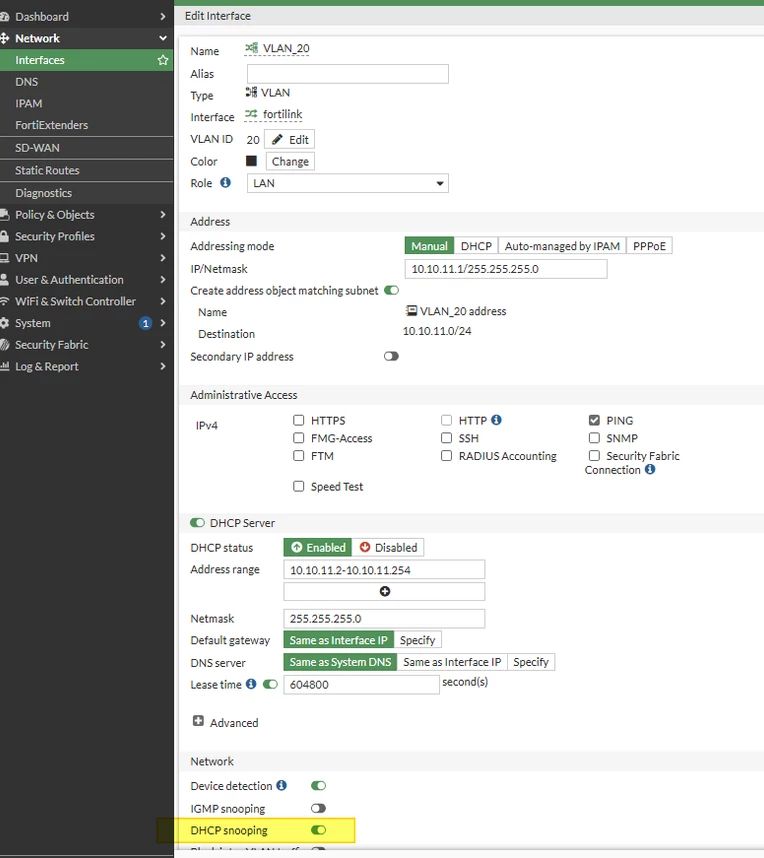
The article describes how to fix DHCP when switch-controller-dhcp-snooping is enabled on a VLAN FortiSwitch interface. DHCP snooping can be used to prevent rogue DHCP servers.
Scope
FortiGate, FortiSwitch
Solution
On CLI:
FGT-NAT # show sys int VLAN_20
config system interface
edit "VLAN_20"
set vdom "root"
set ip 10.10.11.1 255.255.255.0
set allowaccess ping
set device-identification enable
set role lan
set snmp-index 34
set switch-controller-dhcp-snooping enable
set interface "fortilink"
set vlanid 20
next
end
On GUI:
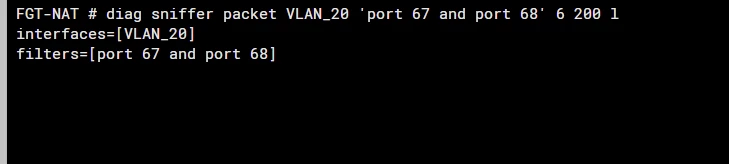
DHCP request is not received on the FortiGate.
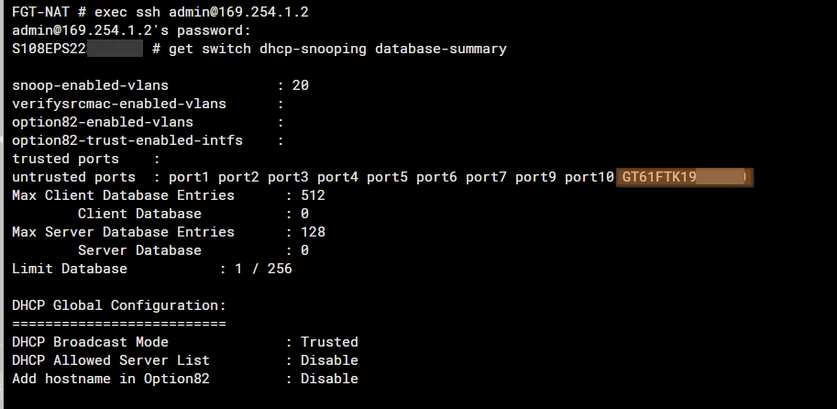
Access FortiSwitch from FortiGate under WIFI & Switch Controller -> Managed FortiSwitches -> 'Right-Click' a FortiSwitch -> Connect to CLI -> Enter password.
Enter the command 'get switch dhcp-snooping database-summary'. FortiSwitch trunk is showing on untrusted ports.
S108EPS223XXXXXX # get switch dhcp-snooping database-summary
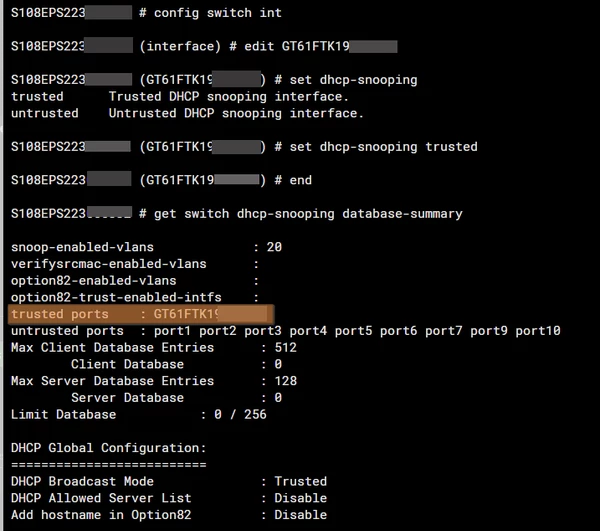
Configure FortiSwitch trunk to 'dhcp-snooping: trusted'.
S108EPS223XXXXXX # config switch int
S108EPS223XXXXXX (interface) # edit GT61FTK19XXXXXX
S108EPS223XXXXXX (GT61FTK19XXXXXX) # set dhcp-snooping
trusted Trusted DHCP snooping interface.
untrusted Untrusted DHCP snooping interface.
S108EPS223XXXXXX (GT61FTK19XXXXXX) # set dhcp-snooping trusted
S108EPS223XXXXXX (GT61FTK19XXXXXX # end
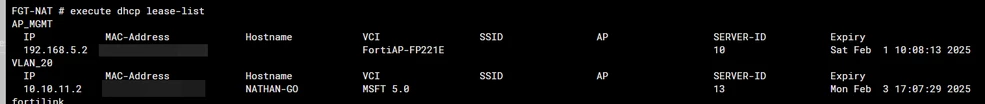
Verify on the FortiGate that the PC received an IP address.
Related articles:
Technical Tip: Understanding DHCP Server and DHCP Relay functionality on FortiGate
Troubleshooting Tip: Wireless clients do not receive IP through DHCP from Bridged SSID
Troubleshooting Tip: Check DHCP Messages with VLAN Tag using Wireshark Packet Capture
