



Troubleshooting Tip: Deleting a local certificate with no references that gives a 'Currently being used' error
| Description | This article explains how to delete a local certificate despite receiving the error 'Can't delete this certificate. It's currently being used.' on a certificate that is not being used. |
| Scope | FortiGate, all firmware. |
| Solution | Sometimes, a local certificate can't be deleted. Even after removing all references, it gives the following error:
Entry is used. Command_cli_delete:6740 delete table entry fgnw unset oper error ret=-23.
Upon attempting to delete the certificate through the CLI, the following error appears:
Can't delete this certificate. It's currently being used.
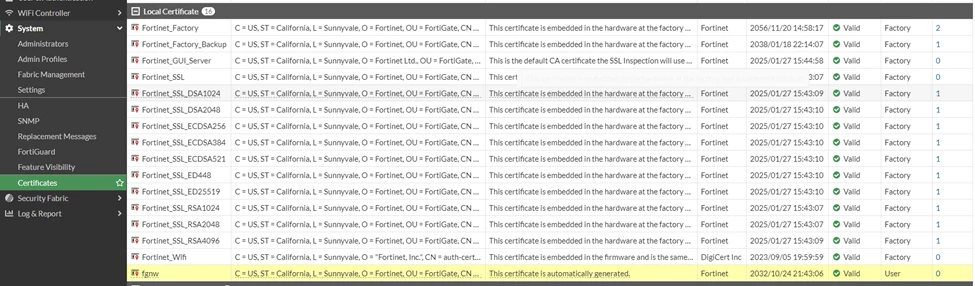
To find out where the certiifcate is being used on Fortigate, run the following commands in the CLI:
# config system global (global) # get | grep fgnw admin-server-cert : fgnw (global) # end
In this instance, the certificate is being used as an 'admin server certificate'. This information can be found in the GUI in System -> Settings under the Administration Settings section.
Check the value of the 'HTTPS server certificate' field:
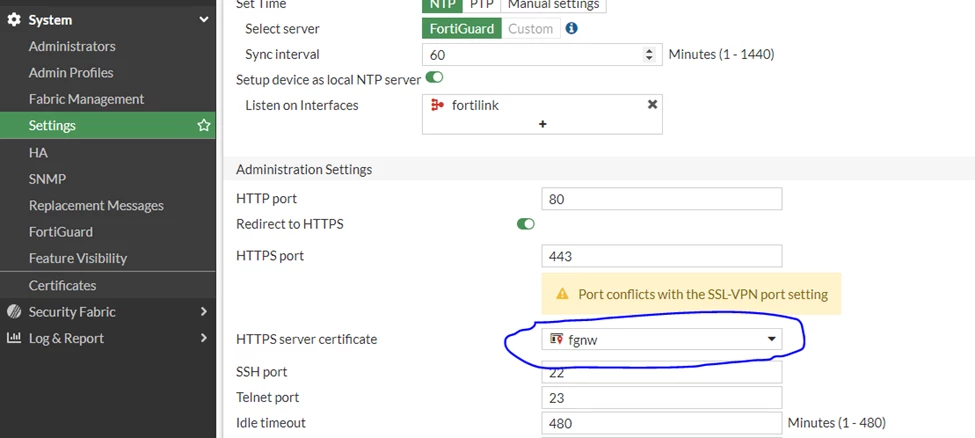
Change the certificate here. After that, the local certificate will be possible to delete.
Optionally, download the configuration file and run a search for 'certificate_name' to find where the certificate is being used in the configuration. |

