When seeing the output debug below when troubleshooting VIP: Debug output:
The first part of the flow trace shows destination NAT matched VID (Virtual IP ID 1).
FGT1 # 2024-10-08 13:10:37 id=65308 trace_id=1 func=print_pkt_detail line=5879 msg="vd-root:0 received a packet(proto=6, 10.10.10.10:56414->20.20.20.20:22) tun_id=0.0.0.0 from port1. flag [S], seq 2020481783, ack 0, win 64240"
2024-10-08 13:10:37 id=65308 trace_id=1 func=init_ip_session_common line=6063 msg="allocate a new session-08bacf6c"
2024-10-08 13:10:37 id=65308 trace_id=1 func=iprope_dnat_check line=5474 msg="in-[port1], out-[]"
2024-10-08 13:10:37 id=65308 trace_id=1 func=iprope_dnat_tree_check line=834 msg="len=2"
2024-10-08 13:10:37 id=65308 trace_id=1 func=__iprope_check_one_dnat_policy line=5337 msg="checking gnum-100000 policy-1"
2024-10-08 13:10:37 id=65308 trace_id=1 func=get_new_addr line=1265 msg="find DNAT: IP-30.30.30.30, port-0(fixed port)"
2024-10-08 13:10:37 id=65308 trace_id=1 func=__iprope_check_one_dnat_policy line=5429 msg="matched policy-1, act=accept, vip=1, flag=104, sflag=2000000"
2024-10-08 13:10:37 id=65308 trace_id=1 func=iprope_dnat_check line=5499 msg="result: skb_flags-02000000, vid-1, ret-matched, act-accept, flag-00000104"
Later in the debug flow, the intended firewall policy 94 is checked, but the matched VIP is not configured on the firewall policy.
2024-10-08 13:10:37 id=65308 trace_id=1 func=__iprope_check_one_policy line=2131 msg="checked gnum-100004 policy-94, ret-matched, act-accept"
2024-10-08 13:10:37 id=65308 trace_id=1 func=__iprope_check_one_policy line=2156 msg="failed to match vid-1"
2024-10-08 13:10:37 id=65308 trace_id=1 func=__iprope_check_one_policy line=2131 msg="checked gnum-100004 policy-95, ret-no-match, act-accept"
Since no other matching policy exists, the check eventually hits implicit deny and is dropped.
2024-10-08 13:10:37 id=65308 trace_id=1 func=__iprope_check_one_policy line=2131 msg="checked gnum-100004 policy-0, ret-matched, act-accept"
2024-10-08 13:10:37 id=65308 trace_id=1 func=__iprope_user_identity_check line=1894 msg="ret-matched"
2024-10-08 13:10:37 id=65308 trace_id=1 func=__iprope_check_one_policy line=2365 msg="policy-0 is matched, act-drop"
2024-10-08 13:10:37 id=65308 trace_id=1 func=__iprope_fwd_check line=844 msg="after iprope_captive_check(): is_captive-0, ret-matched, act-drop, idx-0"
2024-10-08 13:10:37 id=65308 trace_id=1 func=iprope_fwd_auth_check line=873 msg="after iprope_captive_check(): is_captive-0, ret-matched, act-drop, idx-0"
'Failed to match vid-N' indicates that the VIP matched is not present on the firewall policy.
For a list of iPrope table numbers that can assist in determining which firewall function is being checked at various stages in a debug flow, see this article: Technical Tip: iprope policies group.
Unintended match:
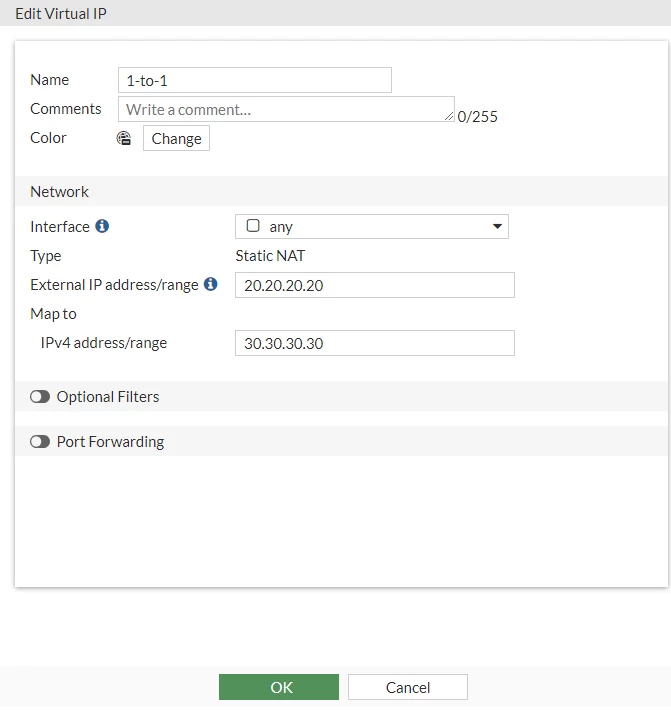 Intended VIP configured later: 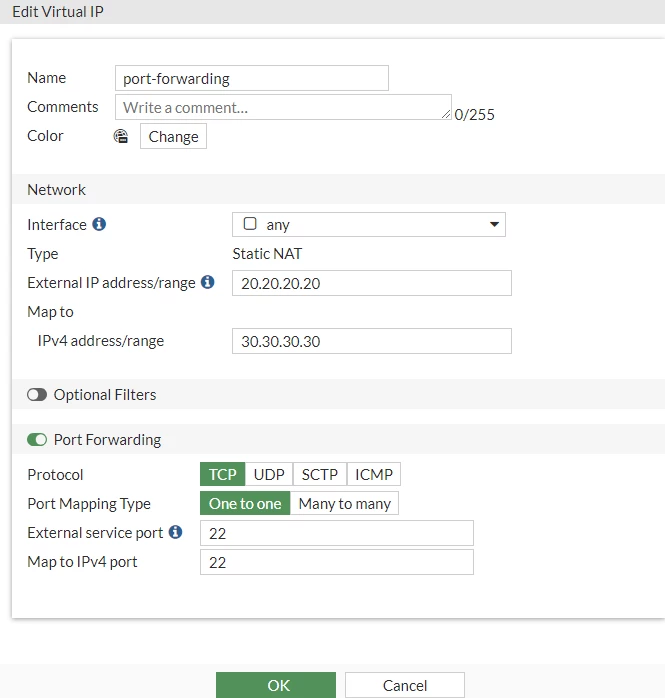 Policy: 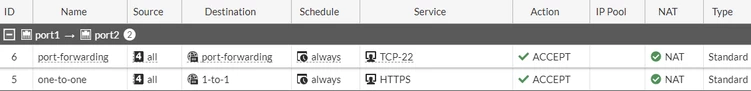
To resolve this issue, move the intended VIP above the original using the instructions in the article: Technical Tip: Virtual IP (VIP) port forwarding order of execution.
Other ways to resolve it include setting filters on VIPs as appropriate, see this article: Technical Tip: FortiOS Destination NAT (DNAT) logic when Central NAT is disabled.
Note: When multiple VIPs are configured with the same external IP address, it is recommended to configure a Source Interface Filter ('srcintf-filter') on each VIP. This allows FortiGate to uniquely identify the correct VIP based on the ingress interface and prevents ambiguous VIP selection during policy lookup. Without a 'srcintf-filter', the firewall may successfully perform DNAT but fail the subsequent firewall policy validation with messages similar to:
matched policy-2, act=accept, vip=2
result: vid-2, ret-matched
...
failed to match vid-2
...
Denied by forward policy check (policy 0)
In this scenario, the packet is translated using the correct VIP, but the forward policy lookup cannot validate the associated VIP ('vid-2'), causing the traffic to fall through to the implicit deny policy. Configuring 'srcintf-filter' on each VIP ensures deterministic VIP selection and allows the corresponding firewall policy to match correctly.
Related articles:
| 




