



Troubleshooting Tip: Connection status: ldap_-5
Description
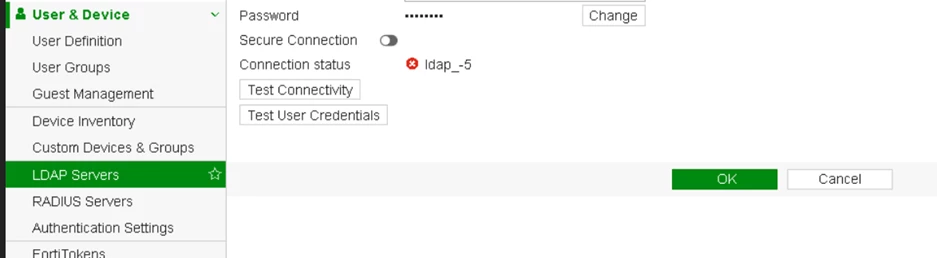
When setting up a new LDAP server in the FortiGate, an error like the one below might be displayed.
Solution
Normally, address any underlying issue that delays the response from the server; but can also increase the default timeout to a more suitable value.
When setting up a new LDAP server in the FortiGate, an error like the one below might be displayed.
Connection status: ldap_-5.
This usually indicates that the response from the LDAP server takes longer than the configured timeout.
This is due to a timeout in the connection, a delay in the network or a LDAP too big to browse in under 5 seconds.
The default has been set to 5 seconds in an attempt to improve security, but depending on the circumstances, 5 seconds may not be long enough to receive a response.
Solution
Normally, address any underlying issue that delays the response from the server; but can also increase the default timeout to a more suitable value.
# config system globalIf the problem persists after the change and LDAPS is being used, make a new attempt using LDAP instead.
set remoteauthtimeout >seconds<
end
Related Articles


