Hasnatriad
Staff
Staff
November 11, 2024

Troubleshooting Tip: Connection Status between FortiGate and MCLAG switches is down/flapping after an upgrade

  • April 16, 2026 at 12:04 PM
  • 0 replies
  • 3266 views
Description

This article describes how to handle connections that are down/flapping between FortiGate and MCLAG FortiSwitches after upgrading the switches.

Scope FortiGate, FortiSwitches.
Solution

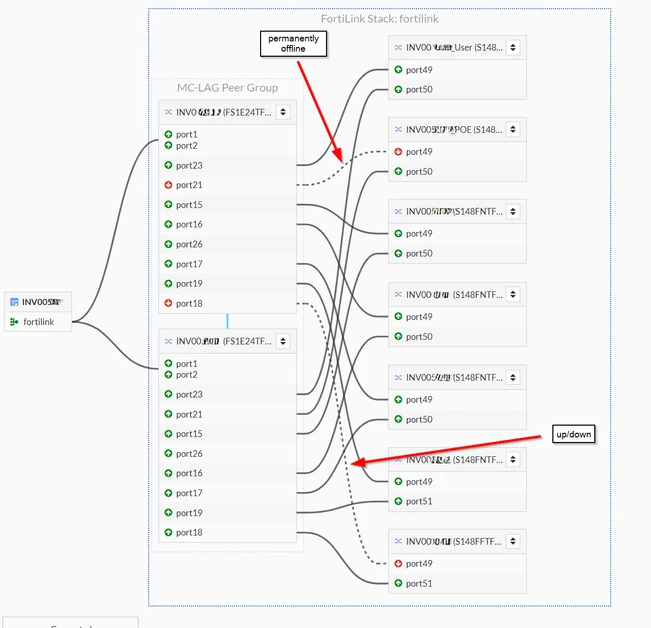
When FortiGate and FortiSwitches are connected and set up with MCLAG switches, after upgrading FortiSwitches, the connection status in the FortiGate GUI shows as down or flapping.


Switches_connection.png


The following logs need to be collected in the FortiGate:


diagnose switch mclag-peer-consistency check <mclag_trunk_name>
diagnose switch mclag icl


Output will show the details of config syn between the switches and port status:


diagnose switch mclag peer-consistency-check 8FFTF2304118

** Comparing "switch.trunk" config ....OK
** Comparing "switch.interface" config ....OK
** Comparing "switch.physical-port" config ....MISMATCH
admin-status <--
speed <--
flow-control <--
max-frame-size <--
** Comparing "switch.stp.instance" config ....MISMATCH
STP instances <--
STP Priority <--

Comparing "LAG state"
-------------------
local ports port21
local inactive ports port21 <--
Peer ports port21
Peer inactive ports none
LAG state FALLBACK


Comparing "STP state"
-------------------
Local active-LAG ports none
Local active ports DISCARDING
Remote active-LAG ports port21
STP-block-ports in instance (33):port21 <--
STP instance misconfiguration missing in instance-0 in remote config <--
STP instance misconfiguration missing in instance-12 in local config <--
STP instance misconfiguration missing in instance-15 in remote config <--

STP instance misconfiguration missing in instance-33 in local config <--


### diagnose switch mclag icl
_FlInK1_ICL0_
model                   FortiSwitch-1024E
peer model              FortiSwitch-1024E
software                v7.4.4,build0861,241004 (GA)
peer software           v7.4.2,build0801,231207 (GA) **peer software mismatch
icl-ports               26
egress-block-ports      none
interface-mac           38:c0:ea:xx:xx:xx
local-serial-number     FS1E24T000000000
peer-mac                38:c0:ea:yy:yy:yy
peer-serial-number      FS1E24T000000001
Local uptime            2 days 3h:35m: 0s
Peer uptime             238 days 5h:45m: 0s
MCLAG-STP-mac           38:c0:ea:9d:6d:0e
keepalive interval      1
keepalive timeout       60
dormant candidate       Peer
split-brain             Disabled

Counters

received keepalive packets              185547
transmited keepalive packets            183497


Solution: 

FortiSwitches in MC-LAG need to be on the exact same firmware. Fortinet recommends upgrading the switches at the same time. This can be done by following Switch and WiFi Controller -> Managed FortiSwitches, then pressing shift, and selecting two switches. After, select Upgrade on them.

Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
Thought Leadership. Security Summit. Thursday, October 8th. Disney's Grand Californian Hotel & SPA, Anaheim, CA.
Security Operations Summit: Modernize SecOps. Operate AI-Native.AMER: November 4 | 9:00 AM PST. India and SAARC: November 5 | 10:00 AM IST. EMEA: November 5 | 10:30 AM CET. APAC: November 5 | 11:00 AM SGT