

akomurlu
Staff
Staff
November 25, 2025

Troubleshooting Tip: Clients are not connected to the internet through FortiGate

  • November 25, 2025
  • 0 replies
  • 948 views


Description

This article describes the steps to troubleshoot and resolve the issue of a client not connecting to the internet through FortiGate. The article provides a detailed solution to help users identify and fix the root cause of the problem.

Scope

FortiGate.

Solution

To troubleshoot the issue of a client not connecting to the internet, follow these steps:

  1. Make sure the FortiGate is properly configured, and all cables are securely connected.

To verify the Layer-1 connectivity, make sure the interface status is green in the GUI and from the CLI, run the following commands to verify the connectivity.

diagnose hardware deviceinfo nic <interface name> 
fnsysctl ifconfig <interface name>


Example:

========== Link Status ==========
Admin :up
netdev status :up
autonego_setting :1
link_setting :1
speed_setting :1000
duplex_setting :0
Speed :1000
Duplex :Full
link_status :Up


  1. Check the routing and policies configured on the FortiGate to ensure they are correct and allow internet traffic.


get router info routing-table details <Source IP>
get router info routing-table details <Destination IP>


Based on the routing info, perform the policy lookup as mentioned in the article below:
Technical Tip: Firewall policy lookups


  1. Use a sniffer to check for ARP requests to the DNS servers and verify if there are any responses.


get system arp 


To collect sniffer output from FortiGate, run the following command in the CLI:

The example below is to check traffic to the DNS server from any interface, where x.x.x.x is the DNS server.

diagnose sniffer packet any 'x.x.x.x' 6 0 a 


Press Ctrl-C to stop the sniffer.


To collect sniffer output from FortiGate GUI, go to Network -> Diagnostics -> New packet capture -> Enable filter and fill in the information -> Start capture:
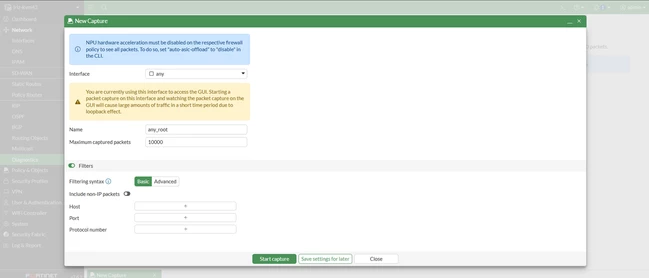
 

Image0.png


  1. If an internal DNS server is used and it is not responding (no reply to ARP request), check the subnet configuration on the FortiGate. Ensure the DNS server is included in the subnet of the LAN interface. If the DNS server is behind a different interface, change it to an interface that is included in the subnet of the LAN interface.

  2. If FortiGate is acting as a DHCP server, make sure the IP allocation is happening correctly.


execute dhcp lease-list


  1. After making the changes, verify that DNS and internet traffic are working correctly for the clients behind the FortiGate.

Related articles:

Technical Tip: Basic L2 connectivity troubleshooting before opening a TAC ticket

Troubleshooting Tip: Unable to load website on internal network connected to FortiGate

    Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
    Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!

