


Troubleshooting Tip: Browser redirects to SAML SSO login page despite SAML being disabled
Description
This article describes an issue where the browser continues redirecting to the SAML SSO login page, even though SAML SSO and related firewall policies are disabled.
Scope
FortiGate.
Solution
Despite SAML SSO and related firewall policies referencing the Azure-AD user group being disabled, the browser still redirects to the SAML SSO login page when attempting to browse any websites, such as google.com.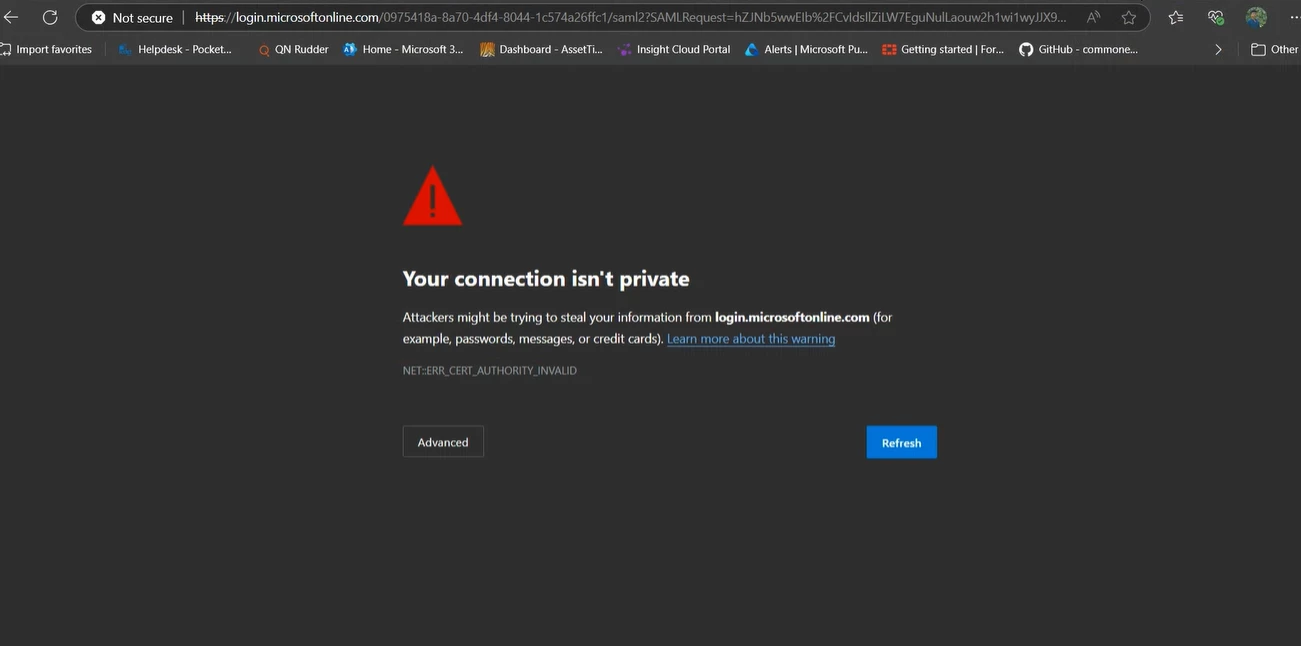
The following is the SAML configuration:
config user saml
edit "AZ"
set entity-id "https://yourinternalip:1003/saml/metadata"
set single-sign-on-url "https:// yourinternalip:1003/saml/login"
set single-logout-url "https:// yourinternalip:1003/saml/logout"
set idp-entity-id "https://sts.windows.net/some-string/"
set idp-single-sign-on-url "https://login.microsoftonline.com/some-string/saml2"
set idp-single-logout-url "https://login.microsoftonline.com/some-string/saml2"
set idp-cert "REMOTE_Cert_2"
set user-name "username"
set digest-method sha1
next
end
config user group
edit "Azure-AD"
set authtimeout 1
set member "AZ"
next
end
The LAN interface is configured with Captive Portal enabled and User access set to 'Restricted to Groups', with the Azure-AD user group assigned, causing the redirection to the SAML SSO login page.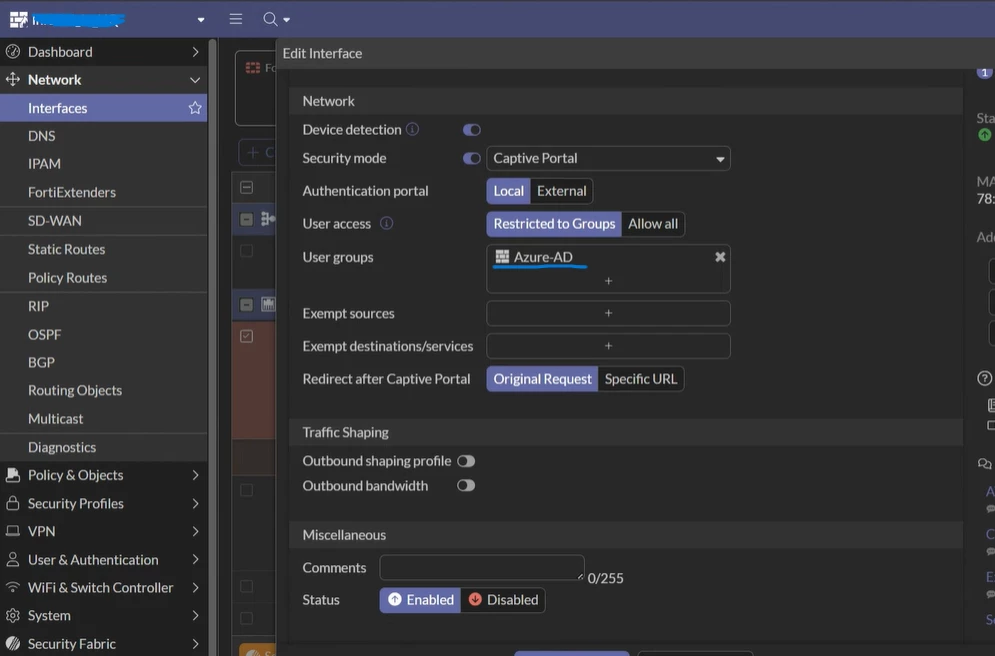
After removing the SAML Azure-AD group from the Captive Portal, traffic was correctly processed by the LAN-WAN firewall policy, resulting in successful access to all websites.


