
Troubleshooting Tip: Alert email send status failed shows in system event logs when user trying to send FortiToken activation code
| Description | This article describes how to resolve the issue when the user is not getting the activation code of FortiToken through email and sees an 'alert email sending status failed' in system event logs. |
| Scope | FortiGate. |
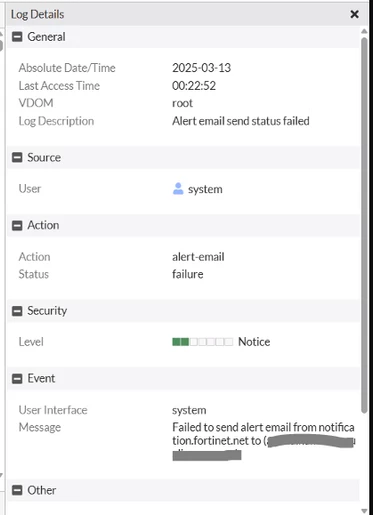
| Solution | After sending the FortiToken activation code through email, in the system event, it shows the Log Description as 'Alert email send status failed', and the user is not getting any activation code.
Review the email server configuration:
config system email-server Make sure the FortiGate can resolve the server FQDN fortinet-notifications.com, test using ping:
FGT (root) # execute ping fortinet-notifications.com
The above shows a working scenario as the FQDN resolves to an IP and is responding to ping. If it does not resolve to an IP Address, see this article, Technical Tip: DNS issues and commands to use, and/or the DNS server's reachability.
Run email alert, debug, and also a sniffer for port 465 that is used in the email server configuration.
Enable the Email alert debug with output: diagnose debug reset diagnose debug enable diagnose debug console timestamp enable diagnose debug application alertmail -1
Now generate a test email with the following command:
diagnose log alertmail test
Sample error shown in the debug output:
connecting to 208.91.114.151 port 465 --------> Email server IP address.
Run sniffer in another CLI window.
diagnose sniffer packet any " host 208.91.114.151 and port 465 " 4 0 l
Traffic is going over the IPsec tunnel because the IPsec tunnel and WAN interface are part of the same SD-WAN zone with the same default route. Not seen any response back to the syn packet over the IPsec tunnel.
config system email-server
After specifying the source IP in the configuration, check the traffic in the sniffer, and traffic for the email server goes over the WAN interface, and also the 3-way handshake is getting completed.
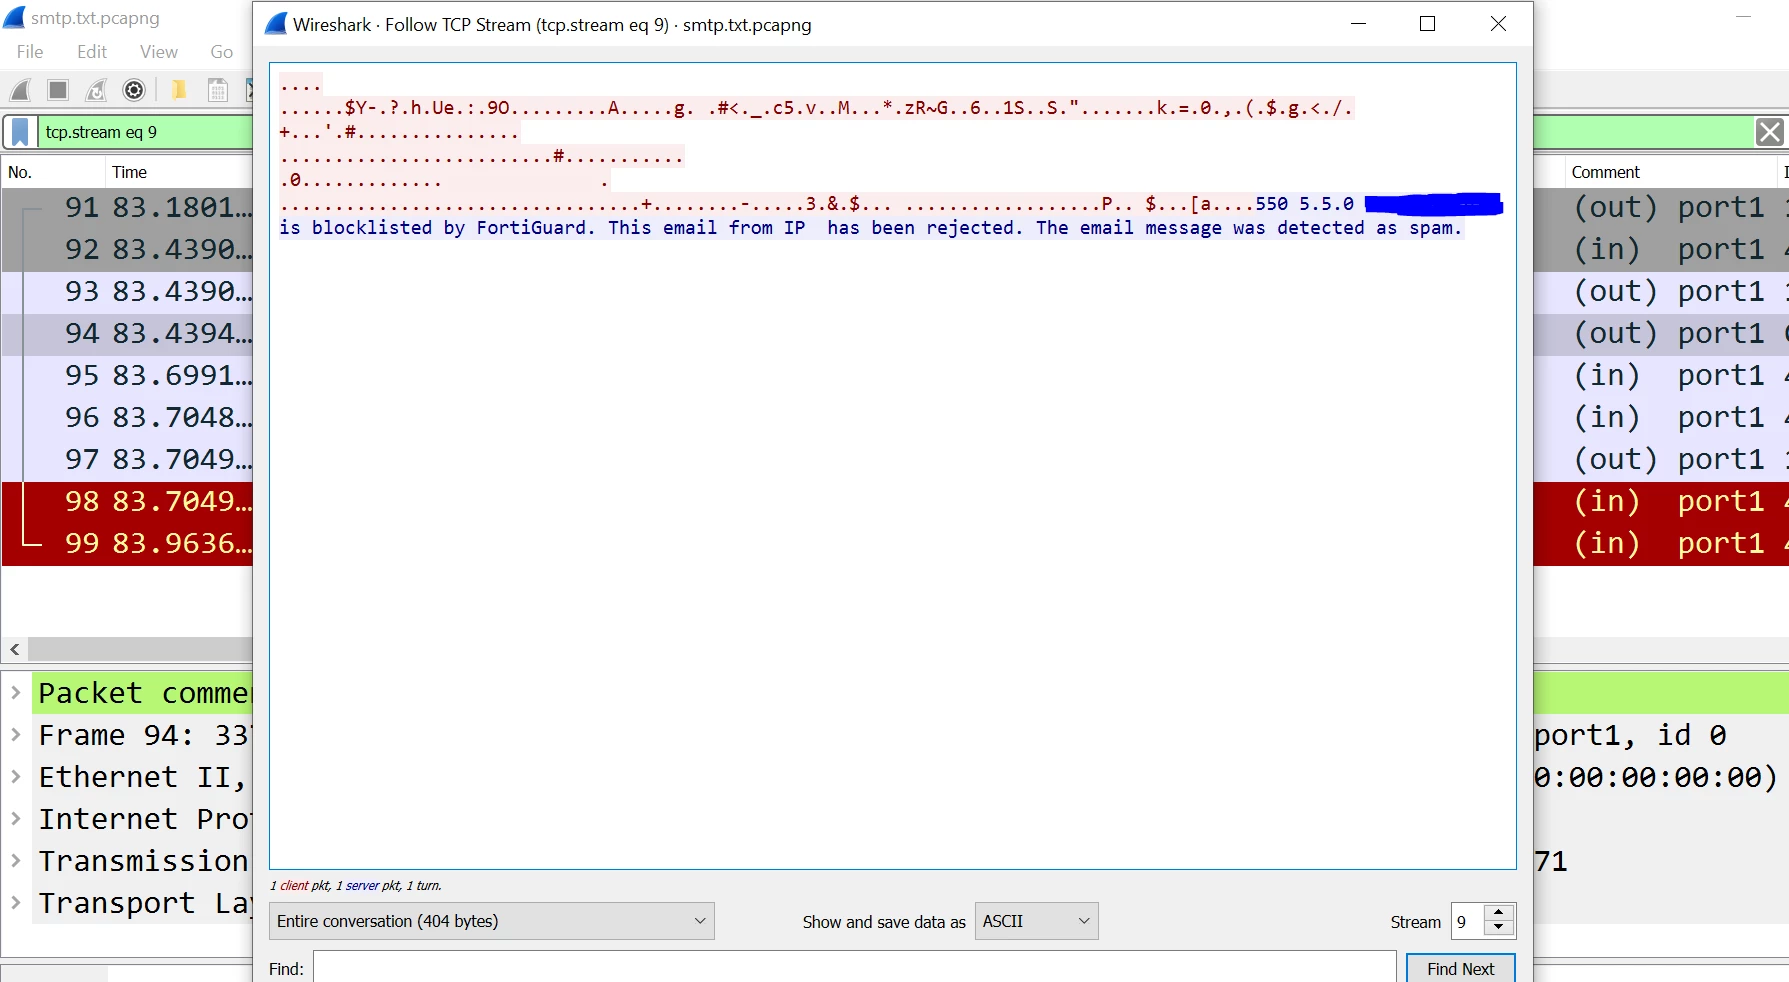
If the send mail failed error shows in the alert mail debug, run a pcap capture using the destination as the server IP, and check the client hello packet from the pcap, and follow the TCP stream as per the diagram below.
From the above diagram, the public IP is blocklisted by FortiGuard, and the email from the IP has been rejected. This email message was detected as spam. In that case, a form has to be submitted to the FortiGuard team to check and whitelist the IP address. The following form can be used for the same purpose: Anti-Spam Blocklist Appeal.
Note: When using another email-server instead of 'fortinet-notifications.com' (i.e., smtp.gmail.com), the same error can be observed when wrong credentials are supplied. Ensure that the account credentials are up to date. Refer to this article: Technical Tip: How to configure email alerts with Gmail.
config system email-server
In some scenarios, with the default Email Service, the following outputs can be seen in the alertmail debug. The 'code: 530' here means that the Authentication is required.
create session
When using port 25 with Security Mode 'None', Modern SMTP servers do not allow unauthenticated mail and are often blocked by ISPs to prevent spam, as it lacks mandatory security.
Using port 465 with 'SMTPS' as Security Mode should help mitigate this issue.
config system email-server
Related articles: Technical Tip: Unable to send FortiToken email using custom SMTP server starting v7.4.4 |