


Technical Tip: Workstation hostname character limit with FSSO scenario
Description
This article describes the workstation hostname character limit while using FSSO authentication when using Standard AD Access mode.
Scope
FortiGate.
Solution
While using FSSO authentication, FSSO collector agent will resolve the hostname to IP address. During this process workstation hostname characters should not exceed 15 characters. If it exceeds this limit, the DNS resolution will fail.
Expectations, Requirements:
FSSO configuration on FortiGate and FSSO collector agent is configured and working fine.
User from 10.40.9.42 will try to log in to the domain controller, the IP and hostname are as follows:
Windows IP Configuration:
Host Name . . . . . . . . . . . . : boson-kvm42-12345
Primary Dns Suffix . . . . . . . : dubailab.lab
Node Type . . . . . . . . . . . . : Hybrid
IP Routing Enabled. . . . . . . . : No
WINS Proxy Enabled. . . . . . . . : No
DNS Suffix Search List. . . . . . : dubailab.lab
Host Name . . . . . . . . . . . . : boson-kvm42-12345
Primary Dns Suffix . . . . . . . : dubailab.lab
Node Type . . . . . . . . . . . . : Hybrid
IP Routing Enabled. . . . . . . . : No
WINS Proxy Enabled. . . . . . . . : No
DNS Suffix Search List. . . . . . : dubailab.lab
IPv4 Address. . . . . . . . . . . : 10.40.9.42(Preferred)
Subnet Mask . . . . . . . . . . . : 255.255.240.0
Default Gateway . . . . . . . . . : 10.40.4.123
DHCPv6 IAID . . . . . . . . . . . : 50356847
DHCPv6 Client DUID. . . . . . . . : 00-01-00-01-21-AC-58-17-00-62-6F-73-2A-01
DNS Servers . . . . . . . . . . . : 10.40.9.78
8.8.8.8
Subnet Mask . . . . . . . . . . . : 255.255.240.0
Default Gateway . . . . . . . . . : 10.40.4.123
DHCPv6 IAID . . . . . . . . . . . : 50356847
DHCPv6 Client DUID. . . . . . . . : 00-01-00-01-21-AC-58-17-00-62-6F-73-2A-01
DNS Servers . . . . . . . . . . . : 10.40.9.78
8.8.8.8
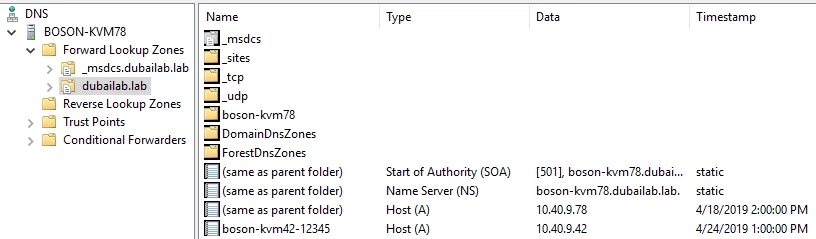
When user logs in from 10.40.9.42 to Domain controller 10.40.9.78, the DNS records is as follows:
From the FSSO collector agent logs:
resolve_ip_internal: workstation:BOSON-KVM42-123.dubailab.lab [10.40.9.42:0.0.0.0] time:0
04/24/2019 13:18:11 [ 5168] after DNS_checking:BOSON-KVM42-123.dubailab.lab
04/24/2019 13:18:11 [ 5168] after DNS_checking:BOSON-KVM42-123.dubailab.lab
From the DC agent logs:
4/24/2019 13:14:05.776: processing Logon (level=1, logonid=0-0) DUBAILAB\BOSON-KVM42-123$ (BOSON-KVM42-123$) from BOSON-KVM42-123
machine account:BOSON-KVM42-123$ is ignored.
machine account:BOSON-KVM42-123$ is ignored.
FSSO DC Agent only records the first 15 characters in the workstation name which causes the domain resolution to fail.
This issue is directly related to the Windows/NetBIOS limitation that NetBIOS only supports up to 15 characters in the computer name. If FSSO support for longer host names is required, change the FSSO collector agent to Advanced AD Access Mode, as shown in the article Technical Tip: How to switch FSSO operation mode from Standard Mode to Advanced Mode.


