

Technical Tip: Whitelist IP addresses and URLs using firewall policies
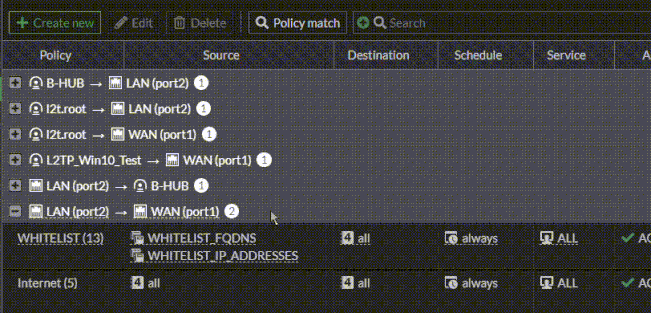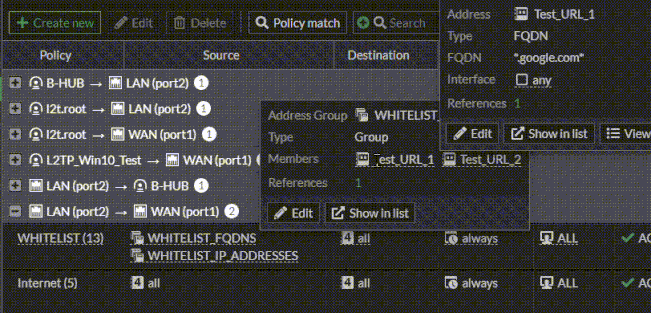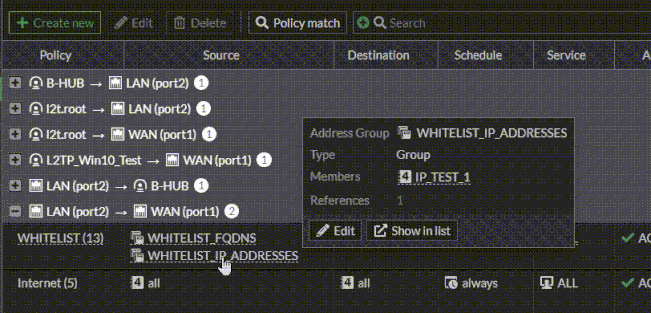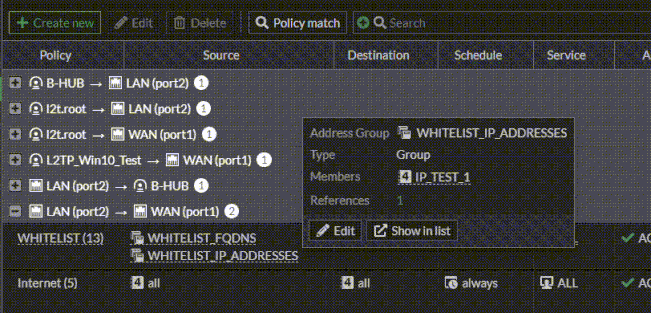
Description | This article describes how to create a rule to whitelist or bypass traffic that is required to not be inspected, namely by using an object group to easily populate the list in the GUI. |
Scope | FortiGate. |
Solution |
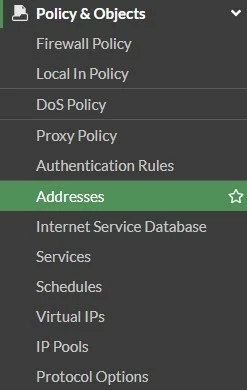
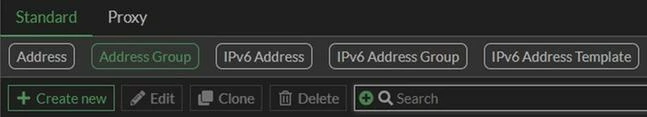
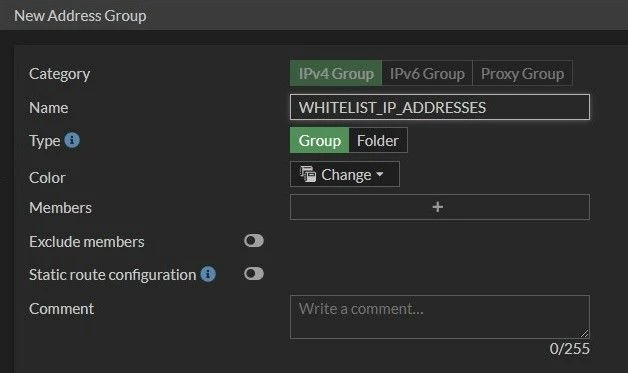
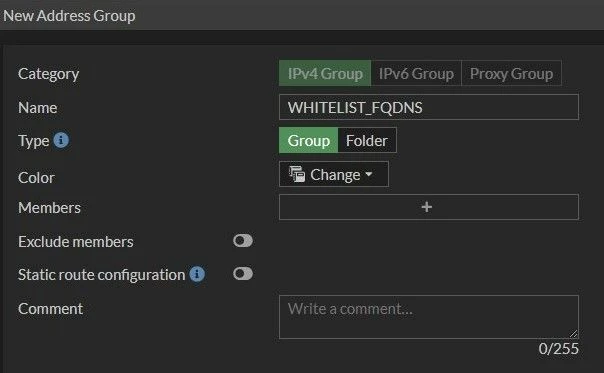
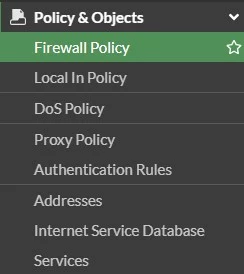
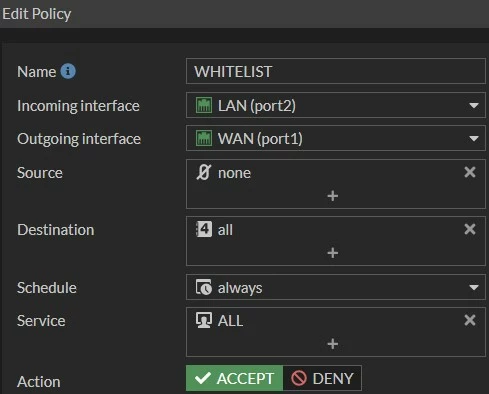
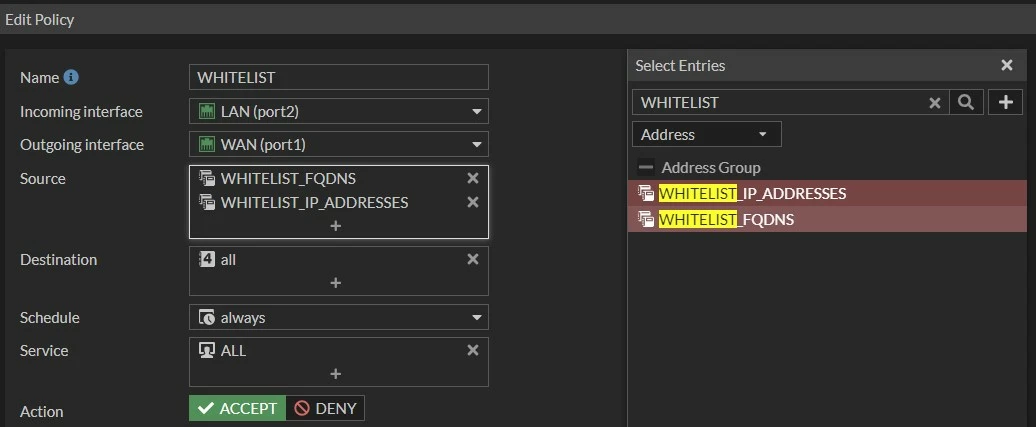
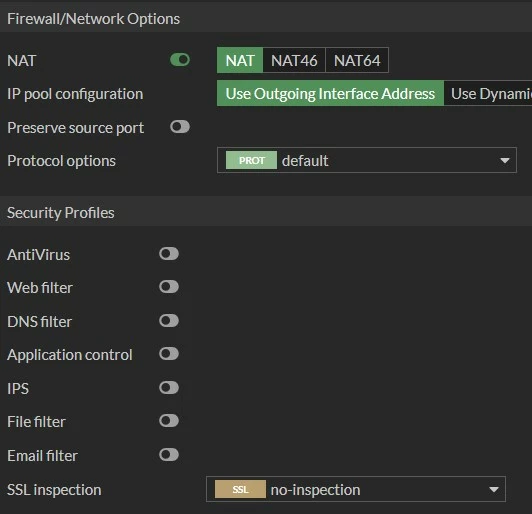
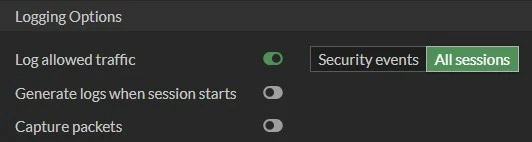
Once the traffic is confirmed to be matching the policy, the logging can be disabled.
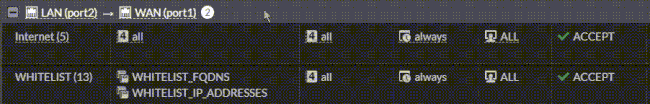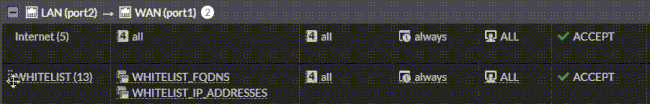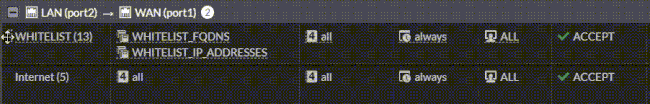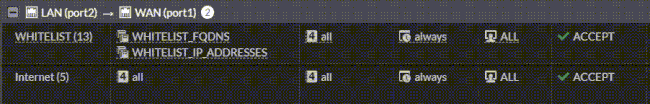
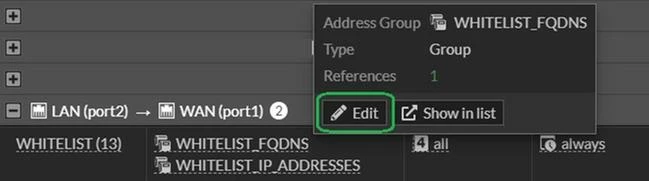
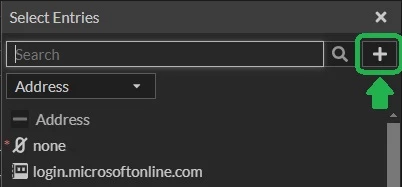
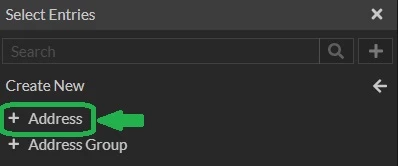
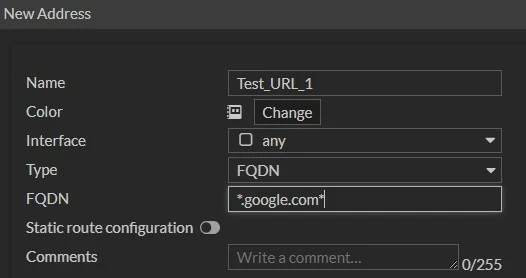
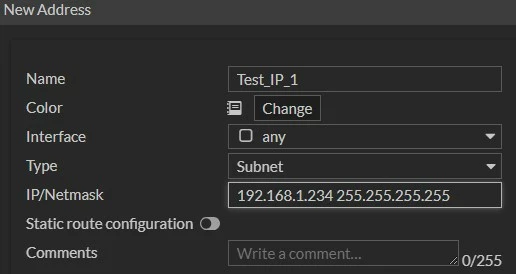
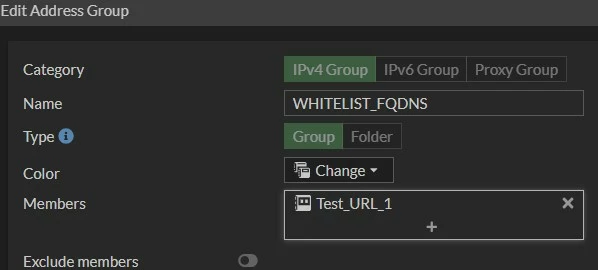
Relevant notes:
The firewall policy does not need to be modified when new members are added to the existing Address Group. For FQDN address objects, FortiGate must be able to resolve the configured FQDN to the corresponding IP addresses. Wildcard FQDN objects operate differently from standard FQDN objects. Standard FQDN objects are resolved directly by FortiGate, while wildcard FQDN entries are populated based on matching DNS traffic observed by FortiGate.
On FortiOS 7.4 and later, the 'Policy Match' feature can be used from the firewall policy page to identify the policy that matches specific traffic parameters. The source interface, source address, destination address, protocol, and destination port used for the lookup should represent the actual traffic being tested. Policy Match identifies the firewall policy that would match the specified traffic. It does not generate traffic or confirm destination reachability. Related articles: Technical Tip: Firewall policy lookups Technical Tip: Using a wildcard FQDN Technical Tip: How to disable SSL Inspection Technical Tip: FQDN based firewall policies are not working intermittently Technical Tip: Using Internet Service Database vs FQDN Address Objects in FortiGate Firewall Policy |


