Technical Tip: Web Filter Profile for incoming a Virtual IP connection
| Description | This article describes how to configure a Web Filter profile for incoming connection to a Virtual IP object |
| Scope | FortiGate. |
| Solution | Most of the time, a Web Filter profile is used to restrict outgoing connection from internal users to the Internet but there may be scenarios where users need to restrict incoming connection to the company's published web server.
Example scenario: Client - Internet - Edge FortiGate - Web Server
The Edge FortiGate will have Virtual IP configured to translate incoming connection to an internal web server. The internal web server will use a different FortiGate Web GUI for the simulation.
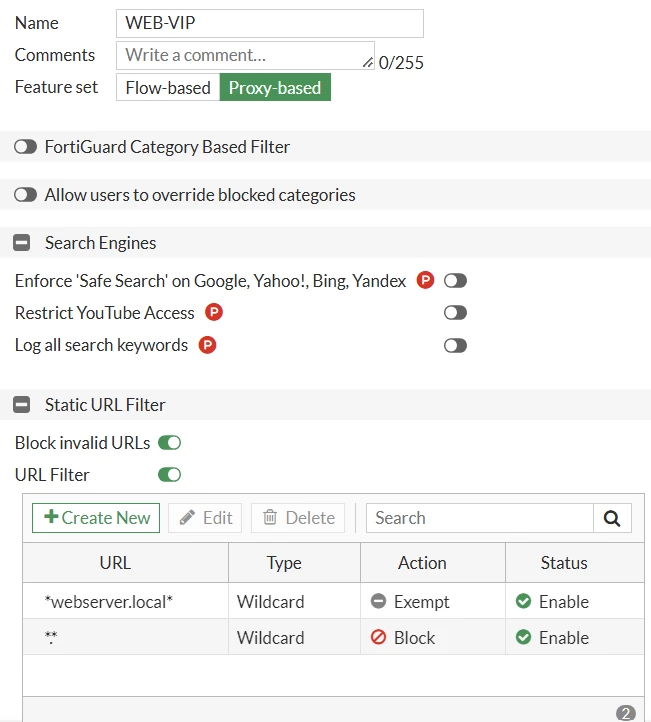
The end user will restrict incoming connections using only using Fully Qualified Domain Name (FQDN), and it will block any other access, for example using the resolved public IP address.
Virtual IP Configuration:
Web Filter Profile setting:
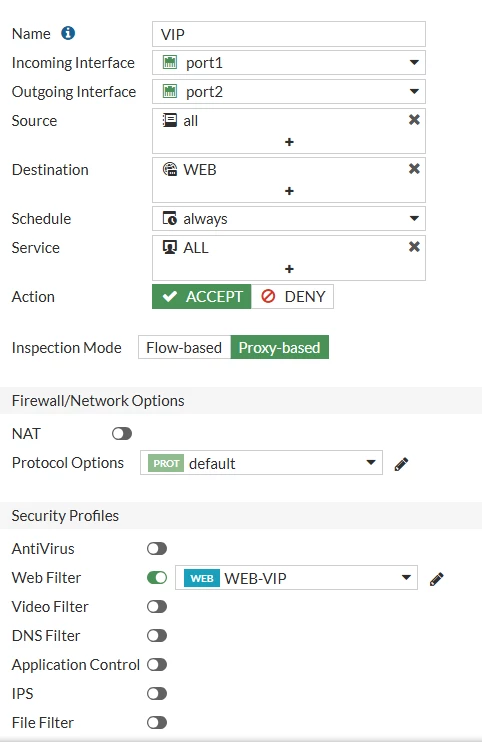
Firewall Policy configuration:
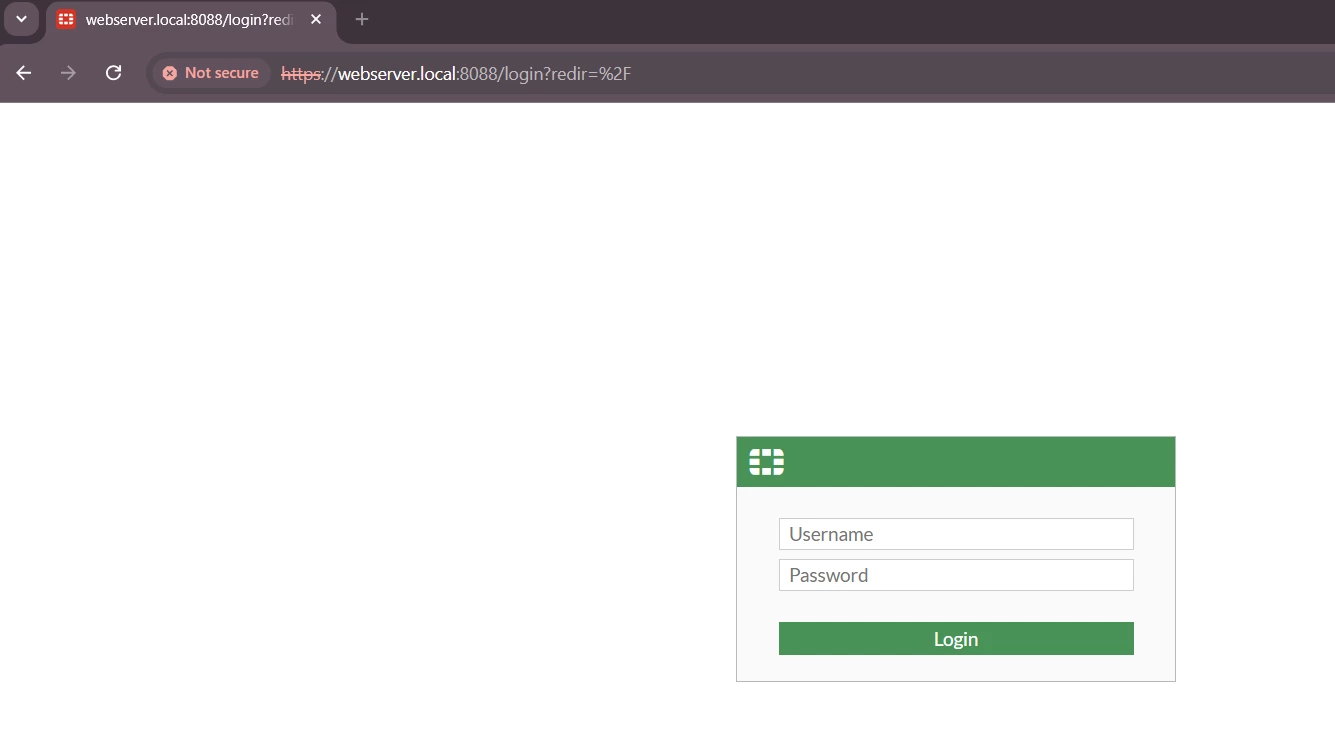
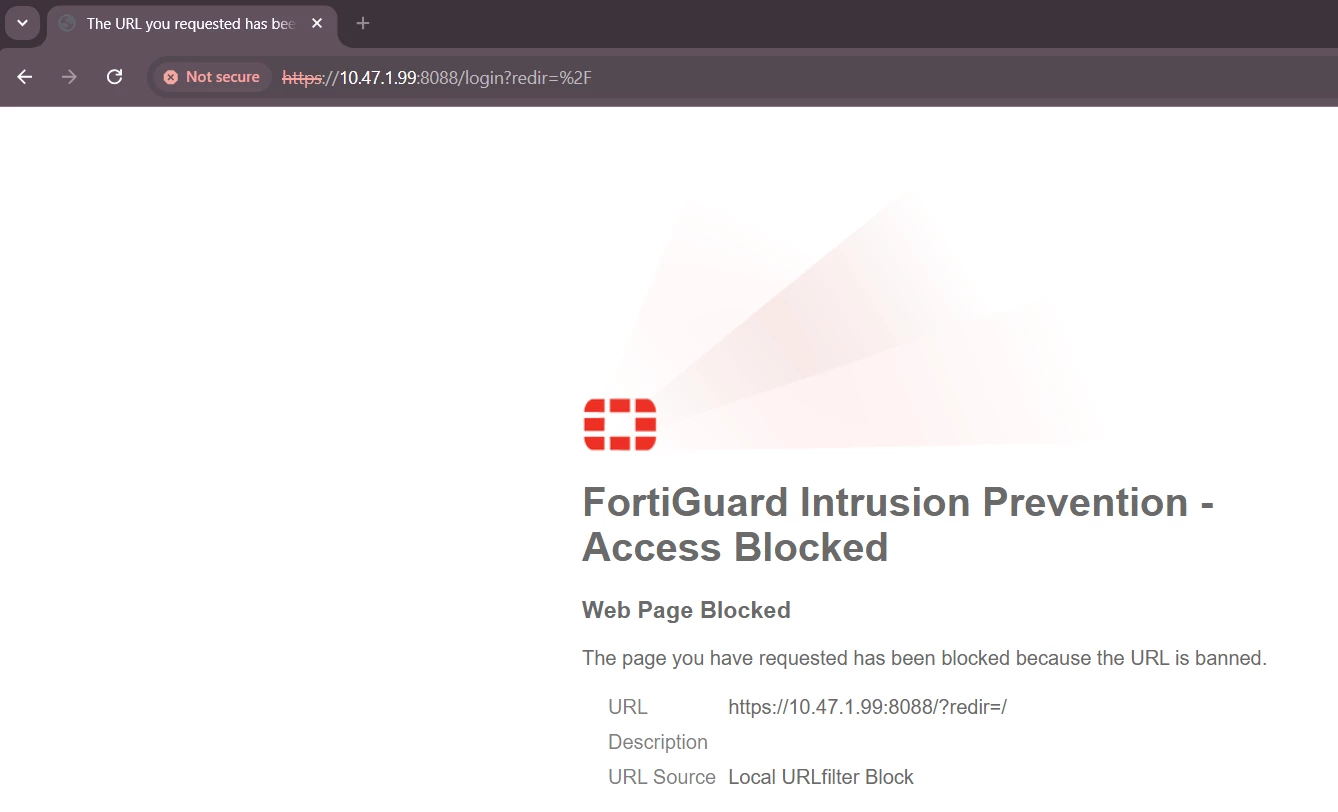
Once these are all configured, the result will be like below.
When using FQDN:
When using a public IP Address:
Web Filter profile for incoming connection to a virtual server also works when the virtual server 'server-type' is https. If the virtual server 'server-type' is SSL, the Web Filter profile does not work.
config firewall vip edit "test-server" set type server-load-balance set server-type https next end |