



Technical Tip: Verify SSL VPN split tunnel route on Windows and Linux
Description | This article describes how to verify the SSL VPN split tunnel route. |
Scope | FortiGate v7.2 through v7.6.2. |
Solution | The SSL VPN split tunnel is configured to use the firewall policy destination in the SSL VPN portal.
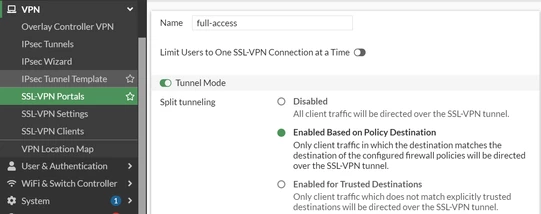
In the SSL VPN policy, the destination address is 192.168.28.0/24, so traffic destined to this subnet will be sent to the SSL VPN tunnel. In this example, traffic destined for other addresses will not be sent to the tunnel:
To verify the route on the split tunnel, run the following command if the client is a Windows device:
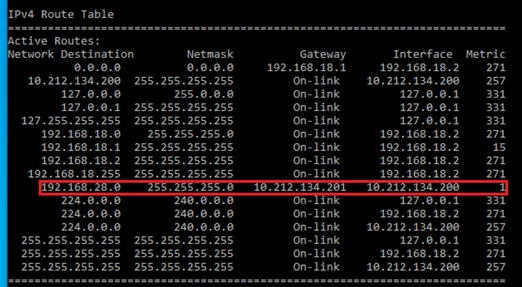
In the above routing table, the IP address 10.212.134.200 is assigned by the FortiGate to the FortiClient. In this example, the gateway 10.212.134.201 is the next IP address after the assigned IP 10.212.134.200. The routing table shows that the split tunnel has added a route to the client for the 192.168.28.0/24 subnet.
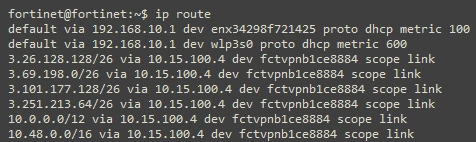
It is possible to run a similar command in Linux to list the routes provided by FortiClient. Use the following command in the terminal:
The routing table shows that some subnets use the tunnel interface 'fctvpnb1ce8884'
Related article: Troubleshooting Tip: Full tunnel and Split Tunnel endpoint route comparison |

