Technical Tip: Verification of FortiGuard Services Updates
Description
This article describes that the GUI status for FortiGuard services may appear correct and show all services in green, but it does not mean that scheduled updates are active. The green status only indicates that FDN servers can be reached.
Scope
FortiGate.
Solution
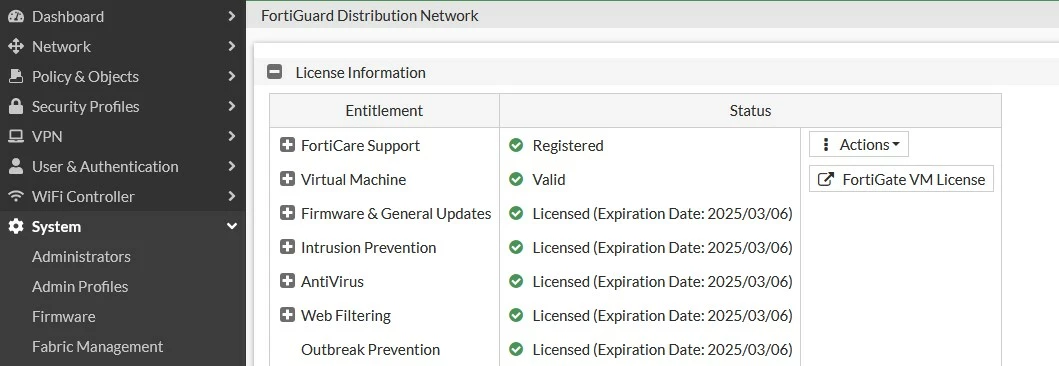
The scheduled updates would not be triggered just by enabling the services. It should also be accompanied by at least one firewall policy with a UTM profile that has antivirus and/or IPS enabled. If these conditions are not met, then scheduled updates are not activated.
The same applies to the Antispam and Web Filtering options.
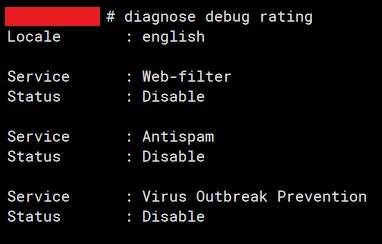
Without any firewall policy that has FortiGuard Web Filtering/Antispam, the command 'diagnose debug rating' will show:
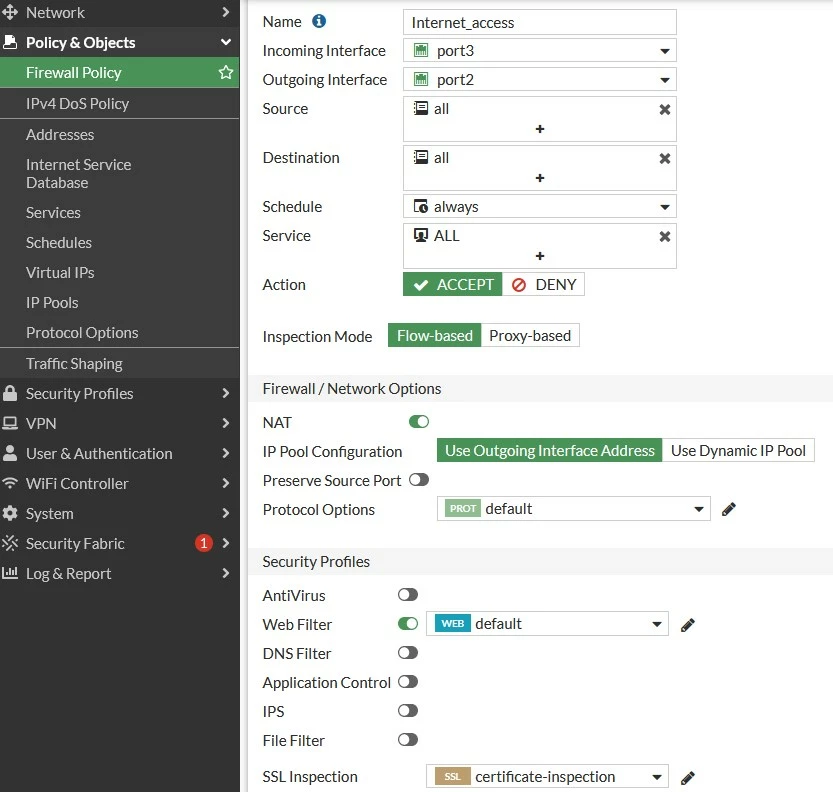
To change the status of the 'Web filter' service to 'Enable' as below, a Firewall Policy should be created a Firewall Policy from the internal network toward the Internet, which has a 'Web filter' Security Profile. Below is an example of such a policy:
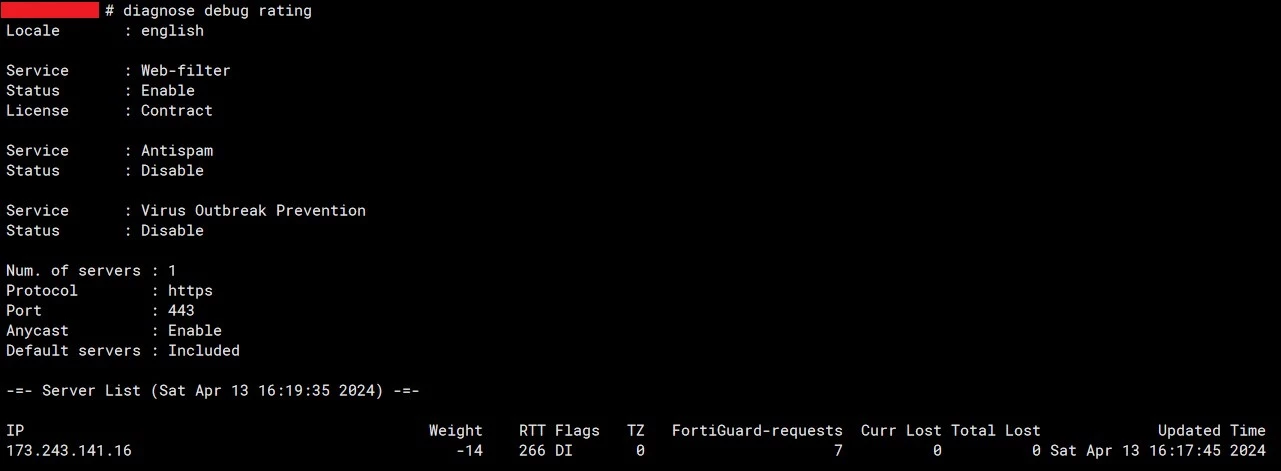
After adding the above Firewall Policy, the status of the 'Web filter' service will be changed to 'Enable', as below, and it has successfully sent an INIT request & established the connection with a rating server as indicated by flags 'DI':
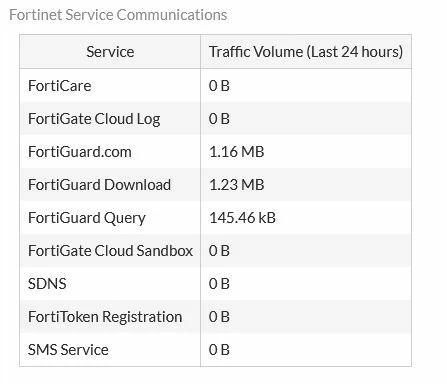
The Service updates can be verified from the Traffic Volume displayed under the System -> FortiGuard page: