Create Traffic Shaping Profile.
Traffic Shaping Profile configuration includes creating Class IDs (identifiers that can be used to apply Traffic Shaping Policies) and assigning Guaranteed Bandwidth, Maximum Bandwidth, and Priority per Class ID.
In this example, 2 Class IDs need to be created, each of which would allow the identification of the traffic for Agents and Management users.
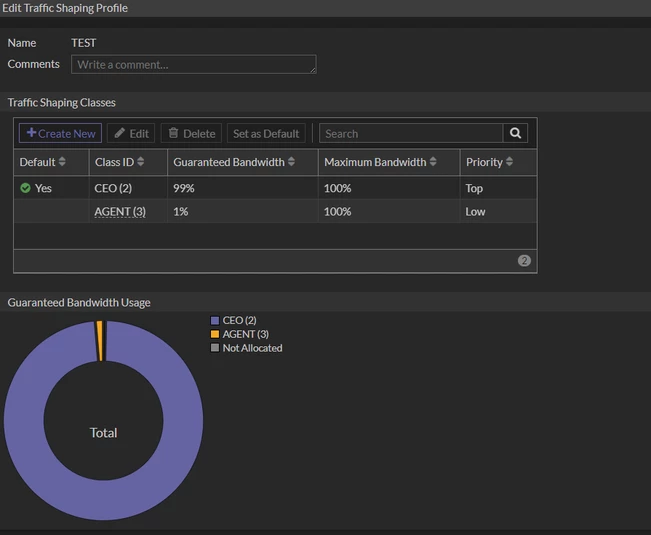
Traffic Shaping Profile
The Class ID named CEO will identify Management Users' traffic, and the Class ID named Agent will identify Agent Users' Traffic.
Guaranteed traffic means that all traffic tagged with this Class ID will always have that percentage of the total amount of Bandwidth available on the interface.
Maximum Bandwidth means that all traffic tagged with this Class ID can use that percentage of the total amount of Bandwidth configured on the interface.
The priority is how the traffic will be prioritized by FortiGate (Top, Critical, High, Medium, Low).
Class ID CEO Configurations:
Guaranteed Bandwidth: 99%.
Maximum Bandwidth: 100%. Priority: Top.
Default.
Class ID AGENT Configurations:
Guaranteed Bandwidth: 1%.
Maximum Bandwidth: 100%.
Priority: Low. Create a Traffic Shaping Policy.
The Traffic Shaping Policy will determine the traffic that is going to be tagged with a Class ID.
It is necessary to configure Source, Destination, Destination Interface, and Action. The action may be to apply a Traffic Shaper or assign a Shaping Class ID. In this case, the action will be to assign a Shaping Class ID. Traffic Shaping Policies work similarly to Firewall Policies, and the traffic is matched from top to bottom. 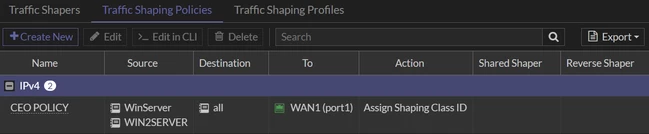
Traffic Shaping Policy 1
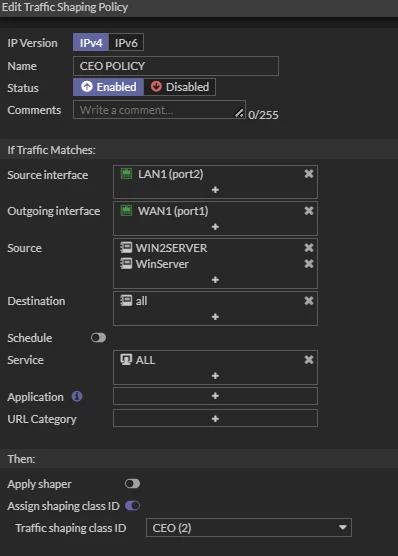
Traffic Shaping Policy 2
The primary goal in this scenario is to prioritize traffic based on Class ID. To achieve this, Traffic Shaping Policies are essential as they enable the assignment of a Class ID to specific traffic.
Since there are two distinct Class IDs, the creation of two Traffic Shaping Policies is necessary, each dedicated to assigning a unique Class ID. Configure WAN Interface.
Following the setup of Traffic Shaping Policies and Traffic Shaping Profiles, the subsequent task involves configuring the WAN interface. It is essential to establish the Inbound Bandwidth and specify the Ingress Traffic Shaping Profile. Additionally, it is possible to configure the Egress Traffic Shaping Profile and set the Outbound Bandwidth, with the specifics contingent on the particular traffic flow.
For user downloads, the traffic would be 'Inbound Traffic', and for user uploads, the traffic would be 'Outbound Traffic'.
In this example, the configurations would apply for Inbound Traffic, but the commands for Outbound Traffic can also be found below.
This can be done using CLI. config system interface
edit "port1"
set inbandwidth 100000
set outbandwidth 100000
set ingress-shaping-profile TEST
set egress-shaping-profile TEST
set inbandwidth 100000 <- Specify the bandwidth for the interface in kbps. The percentage configured on the Class ID will be calculated based on this value. outbandwidth 100000 <- Specify the bandwidth for the interface in kbps. The percentage configured on the Class ID will be calculated based on this value. ingress-shaping-profile TEST <- Name of the Shaping Profile created in the First Step. egress-shaping-profile TEST <- Name of the Shaping Profile created in the First Step.
With this configuration, traffic between Agent Users and Management Users will be prioritized. It is possible to verify this by downloading a file on an Agent Machine. It will utilize all available bandwidth. However, when a download is initiated on a Management User Machine, the download speed on the Agent Machine will decrease to 1%, while the Management User Machine will start utilizing all available bandwidth. Agent Machine would start using all the BW again after the Download on the Management User Machine has ended or if it is canceled. Note: If the shaping-profile mode needs to be changed from the default (policing) to queuing, this can only be done via the CLI, as in the example below: config firewall shaping-profile
edit "TEST"
set type queuing
next
end
Default type is set to 'Policing'.
If the type = 'queuing' and the FortiGate devices contain either NP6lite or NP6xlite chips, then ASIC offloading must be disabled on the appropriate firewall policy/policies (example below), otherwise the shaping-profile has no effect.
Since v6.4.4, policing mode is offloaded by default on NP6lite/NP6xlite devices. config firewall policy
edit 1
set auto-asic-offload disable
next
end
By default it is set to 'enable'.
When NPU offloading is enabled on FortiGates with NP7 or NP7Lite (SoC5) processors, the class ID limit for egress traffic is 2 - 11 and it could be extended up to 31 in the case that disable is set for NPU offloading, otherwise, setting the egress traffic class ID outside of these limits can result in unexpected behavior
If the type is set to queuing, ingress-shaping-profile cannot be used on the interface.
config system interface
    edit "wan"
        set inbandwidth 100000
        set outbandwidth 100000
        set egress-shaping-profile "TEST"
        set ingress-shaping-profile "TEST"
    next
end

config firewall shaping-profile
    edit "TEST"
        set type queuing
end
Error: 'type' can not be 'queuing' when this profile is used as 'ingress-shaping-profile'.
object check operator error, -651, discard the setting
Command fail. Return code -651
Use the following command to view network interface statistics for the traffic-shaper profile:
diagnose netlink interface list <interface name>
if=port1 family=00 type=1 index=5 mtu=1500 link=0 master=0
ref=32 state=start present fw_flags=10010000 flags=up broadcast run multicast
Qdisc=mq hw_addr=e0:23:ff:cc:76:de broadcast_addr=ff:ff:ff:ff:ff:ff
ingress traffic control:
bandwidth=10000(kbps) lock_hit=0 default_class=2 n_active_class=1
class-id=2 allocated-bandwidth=10000(kbps) guaranteed-bandwidth=100(kbps)
max-bandwidth=10000(kbps) current-bandwidth=19(kbps)
priority=high forwarded_bytes=750K
dropped_packets=0 dropped_bytes=0
egress traffic control:
bandwidth=10000(kbps) lock_hit=0 default_class=2 n_active_class=1
class-id=2 allocated-bandwidth=10000(kbps) guaranteed-bandwidth=100(kbps)
max-bandwidth=10000(kbps) current-bandwidth=156(kbps)
priority=high forwarded_bytes=3880K
dropped_packets=0 dropped_bytes=0
stat: rxp=197977 txp=205285 rxb=13377667 txb=13550687 rxe=0 txe=0 rxd=0 txd=0 mc=0 collision=0 @ time=1756716768
re: rxl=0 rxo=0 rxc=0 rxf=0 rxfi=0 rxm=0
te: txa=0 txc=0 txfi=0 txh=0 txw=0
misc rxc=0 txc=0
input_type=0 state=3 arp_entry=0 refcnt=32
| 



