



Technical Tip: Using the save option 'set cfg-save revert' to automatically reboot and revert to a previous configuration of a FortiGate
Description
Solution
The global setting parameter 'set cfg-save' dictates the way that configuration changes applied to the FortiGate are saved:
config system global
set cfg-save ?
automatic automatically save config.
manual manually save config.
revert manually save config and revert the config when timeout.
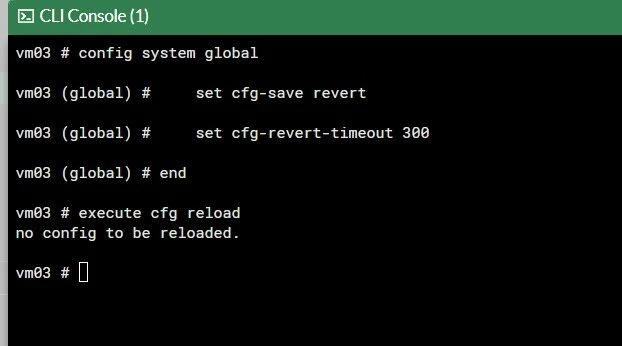
Configure Runtime-only mode using the following CLI commands.
config system global
set cfg-save revert
set cfg-revert-timeout 300
end
execute cfg reload
The default setting is 'automatic': In this mode, any changes applied after an 'end' or 'Apply' will be saved.
If set to 'revert', an additional global parameter is required, which is the timeout in seconds: 'set cfg-revert-timeout'.
The cfg-save revert option enables Runtime-Only behavior.
The cfg-revert-timeout value defines the time, in seconds, during which the configuration must be confirmed before an automatic rollback occurs.
In this example, the timeout is set to 300 seconds.
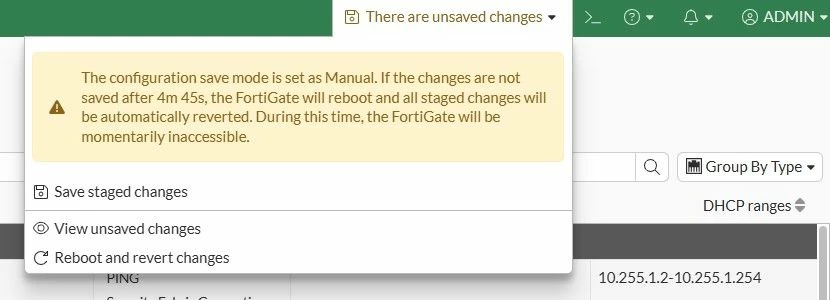
If the configuration is not confirmed within the configured timeout, the FortiGate automatically reloads the last saved configuration.
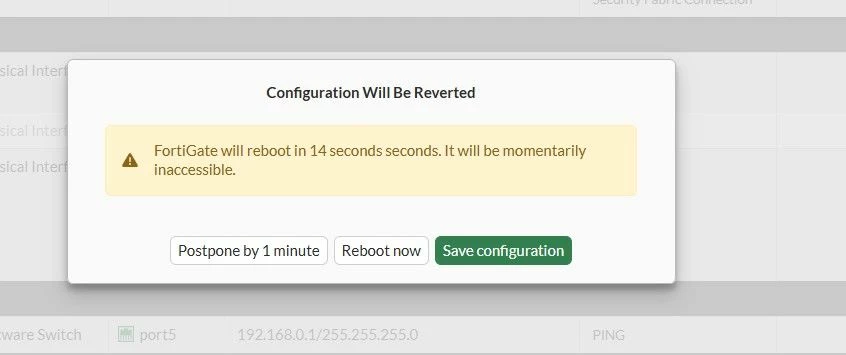
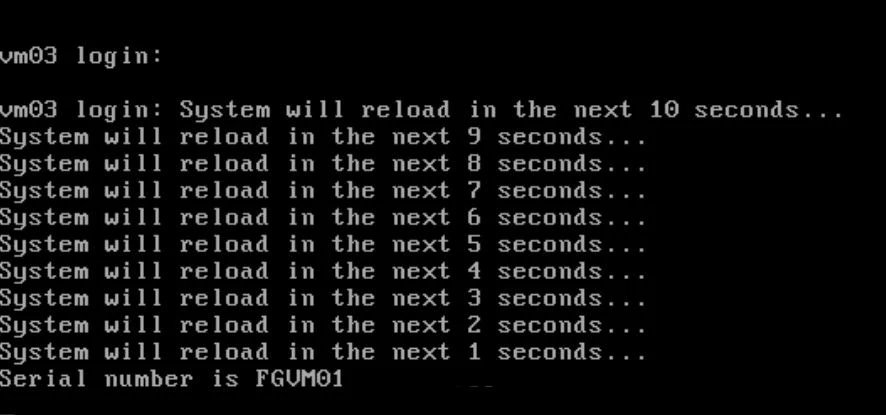
A warning CLI message will be displayed 10 seconds before the reboot:
System will reboot if no input is received in the next 10 seconds...
System will reboot if no input is received in the next 9 seconds...
System will reboot if no input is received in the next 8 seconds...
System will reboot if no input is received in the next 7 seconds...
Example:
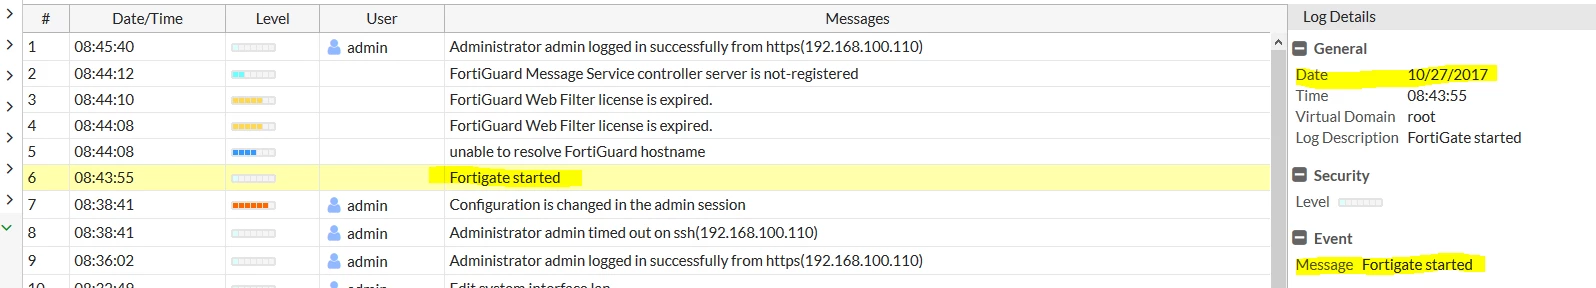
This example explains the use of the cfg-save revert command and its associated event log 'FortiGate Restarted' when a newly added configuration is not confirmed.
FG100D_Primary (global) # set cfg-save
automatic Automatically save config.
manual Manually save config.
revert Manually save config and revert the config when timeout.
FG100D_Primary (global) # show full-configuration | grep cfg
set cfg-save automatic
FG100D_Primary (global) # show full-configuration | grep cfg
set cfg-save revert <----- Changed from automatic to revert.
set cfg-revert-timeout 600 <----- (10 Minutes).
FG100D_Primary (lan) # set role
lan Connected to local network of endpoints.
wan Connected to Internet.
dmz Connected to server zone.
undefined Interface has no specific role.
FG100D_Primary (lan) # set role lan <----- Added a new role to the LAN interface configuration to generate a new change in the current configuration.
FG100D_Primary (lan) # end
FG100D_Primary (lan) # show full-configuration | grep role
set role lan <----- New configuration added to interface.
FG100D_Primary (lan) # show full-configuration | grep role
set role undefined <----- The newly added configuration of role on the interfaces was never added to the current configuration due to the 'timeout' of 600 seconds (10 Minutes) expired, and the newly added configuration was never confirmed, generating the event log 'Fortigate Restarted' under system events.
Starting FortiOS v7.0.2, this option is available on the GUI named 'Configuration save mode'.
More details on GUI support for configuration save mode.
Related articles:
Technical Tip: Configuration file save mode for configuration changes
Technical Tip: How to manually save the config using workspace mode
