Technical Tip: Use SD-WAN for local out traffic or Management traffic (DNS, NTP, sflow,netflow, LDAP, Radius etc)
| Description | This article discusses that Local-out traffic is defined as the traffic initiated by FortiGate, usually for management purposes.
For example, when it is necessary to ping a device from FortiGate, that is local-out traffic. When FortiGate connects to FortiGuard to download the latest definitions, that is also local-out traffic. |
| Scope | FortiGate v6.4 or later. |
| Solution |
config system dns | ntp | sflow | netflow config system central-management config system fortiguard config user radius | ldap | fsso config log fortianalyzer setting config log syslogd setting
Note:
Example:
***DNS*** config system dns
*** Central Management (fgfm tunnel) *** config system central-management set interface-select-method {auto |sdwan | specify} set interface <interface> end
*** NTP *** config system ntp config ntpserver edit <id> set interface-select-method {auto | sdwan | specify} set interface <interface> next end end
*** Authentication (TACACs+, RADIUS,LDAP) *** config log tacacs+accounting
*** Logging (syslog, sflow, netflow) *** config system {netflow | sflow | vdom-netflow | vdom-sflow}
***FortiGuard, FortiSandbox*** config system fortiguard | fortisandbox
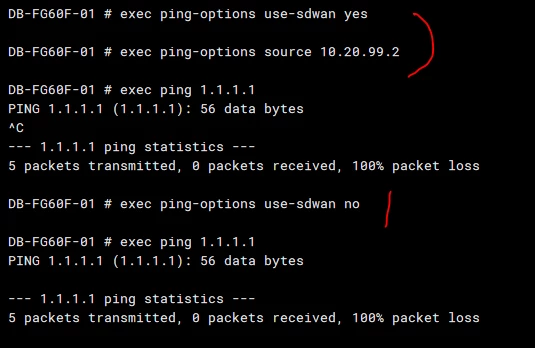
To enable SD-WAN for ping and traceroute:
execute ping-options use-sdwan yes execute traceroute-options use-sdwan yes
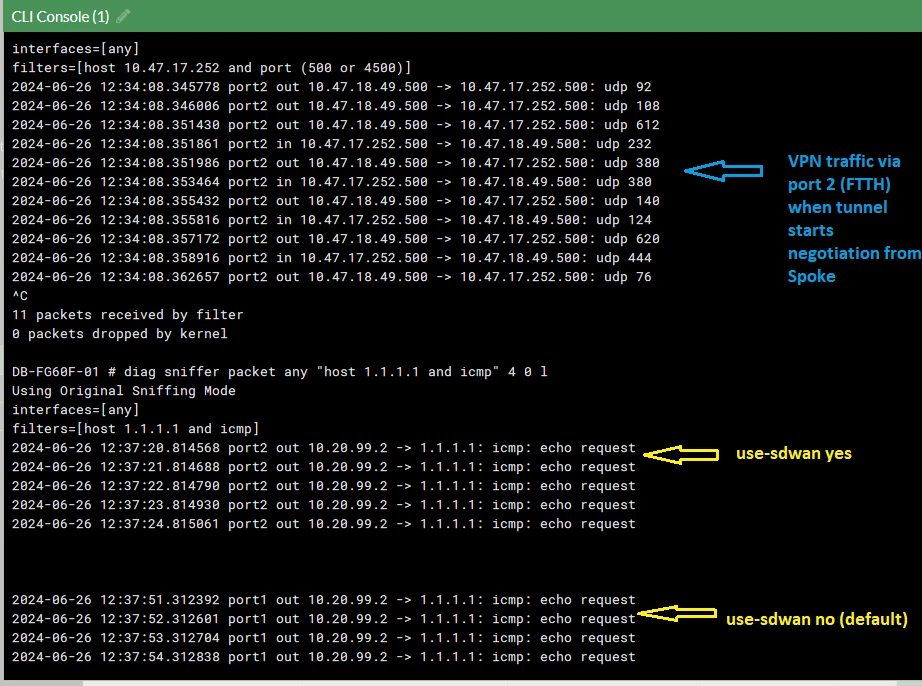
For example, 10.20.99.2 is the Firewall interface's IP address, traffic from it will be considered local-out traffic and by default, it does not follow the SD-WAN rule. If the 'use-sdwan' option is enabled, it will follow the SD-WAN rule:
Related articles:
|