pachavez
Staff & Editor
Staff & Editor
February 6, 2024

Technical Tip: Use local-in policy to restrict unauthorized login attempts to administrative access of FortiGate

  • April 16, 2026 at 11:02 AM
  • 0 replies
  • 25021 views
Description This article describes how to use local-in policies to restrict administrative access from attackers or malicious IPs trying to get into the FortiGate.
Scope FortiGate.
Solution

There are instances where unauthorized login attempts are coming from malicious IPs trying to get into the FortiGate.

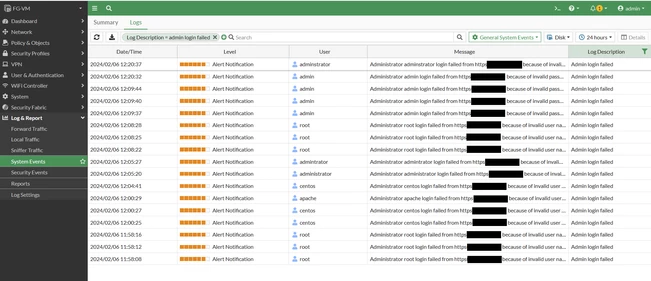
It is strongly recommended to restrict the login to those malicious IPs. Below are sample logs indicating brute force attempts from attackers.


brute force logs edited.png


To apply a local-in policy to restrict unauthorized attempts on administrative access (HTTPS, HTTP, SSH, SNMP) of the firewall.


Local-in Policy is configurable only from CLI for FortiOS v7.4 and below.
Starting v7.6, local-in policy can be configured from GUI and CLI: GUI support for local-in policies.


  1. Create a firewall address object for specific IPs, subnets, countries, and sources to restrict access to the administrative interface. In this example, a specific IP will be blocked:


config firewall address
    edit "Block_IP"
        set subnet 10.47.17.179 255.255.255.255
    next
end


  1. Create a local-in policy and apply the created firewall address. The default action of the local-in policy is 'deny'.


config firewall local-in-policy
    edit 1
        set intf "port1" <----- ISP port (Port going to the Internet).
        set srcaddr "Block_IP"
        set dstaddr "all"
        set service "ALL" <----- Define specific service/s.
        set schedule "always"

        set status enable
    next
end


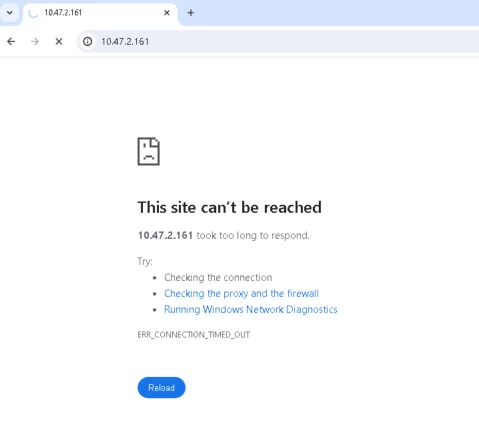
Once the local-in policy is applied, the attacker from the defined IP/subnet will no longer be able to reach the administrator login prompt.

 local-in 4.png


By default, local traffic logs in FortiGate are disabled. To enable local traffic logs, see Technical Tip: Local traffic logs tab shows no results.


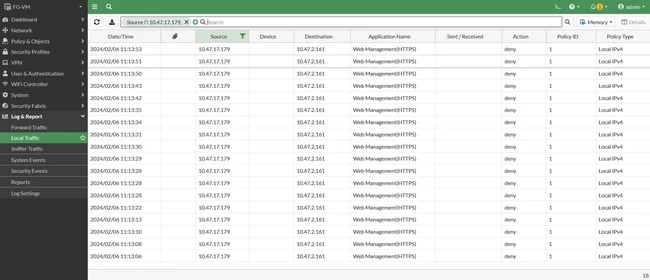
To view local-in policy logs, navigate to Log & Report -> Local Traffic:


local-in 3.PNG


To allow login attempts only from the United States or a specific country and block access from the rest of the world, follow this sample script, where login is permitted only from IP addresses belonging to the United States.


  1. Create a Geo-IP-Based Address for the United States: Ensure a Geo-IP address object for the United States is created. If it is not, follow the instructions in this document: Geography based addresses to create one.


  2. Configure Admin access control: Once the address object for the United States Geo-IP is created, use the following script to allow only United States-based IP addresses to access the admin login page. Starting from FortiGate v7.6.0, the Local-in-Policy can also be configured in the GUI. Refer to this document for reference: Technical Tip: Creating a Local-In policy (IPv4 and IPv6) on GUI.


Note:
Starting from v7.4.6 and in v7.6.x, SD-WAN zones can be selected as an interface in the firewall local-in policy. The interface/s part of that zone cannot be selected. In previous versions, only individual interfaces were available for selection. For more details, see the article: Technical Tip: SD-WAN zone in Local-in Policy.


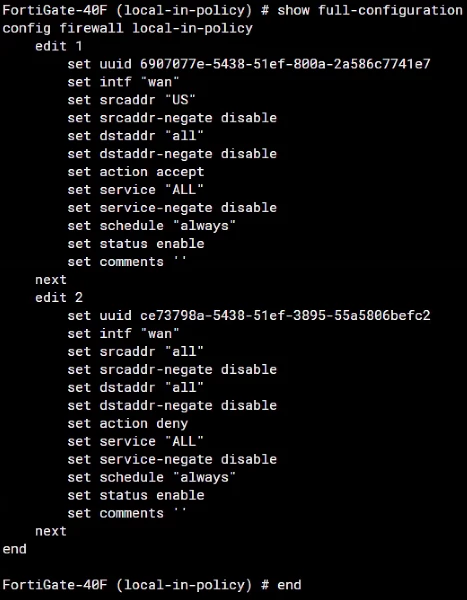
image - 2024-08-07T151310.306.png


Ignore the UUI Part in the previous screenshot.


Note:

In the script below, the United States Geo-IP address object is named 'US'. Adjust the name in the script to match the address object name if it differs.


    edit 1
        set srcaddr "US" <- Specify the address object name for the United States here.


  1. Verification: After running the above script, verify that the FortiGate admin login is accessible only from the United States and blocked from other countries.


  1. Troubleshooting: If issues are encountered, ensure that the Geo-IP database is up-to-date by following the instructions in this article: Technical Tip: Commands to verify GeoIP information and troubleshoot GeoIP database.


Run the following command lines on the CLI console:


To show the local-in-policies:


show firewall local-in-policy


Debug dropped management traffic:


diagnose debug flow filter addr <source-ip>
diagnose debug flow show console enable
diagnose debug flow trace start 10


A simpler way for the same requirement as above, where the FortiGate blocks HTTPS access from all non-US IP addresses, can be done by utilizing the 'src-addr-negate' option in the local-in policy, which is described in Technical Tip: How to configure a local-in policy to only allow specific subnet using srcaddr-negate enable option.


config firewall local-in-policy

    edit 1

        set intf "wan"

        set srcaddr "US"

        set srcaddr-negate enable <----- This command will negate the rule. It will block all non-US IP addresses.

        set dstaddr "all"

        set action deny

        set service "HTTPS" <----- If a different port is used, add a new service object by following the document: Creating service objects.

        set schedule "always"

        set status enable

    next

end


When using the 'United States' geographical address group in the srcaddr field, this will also exclude RFC 1918 private subnet ranges. For instance, if an administrator tries to access FortiGate on the LAN port using 192.168.1.99, it will be blocked as it is a private IP address, which would not be defined in the Geographical IP ranges for any country. 


The best option would be to have a Geo address 'US' as well as a local subnet in an address group, and then apply it in local-in-policy.


config firewall address

    edit "Lan"

        set subnet 192.168.1.0 255.255.255.0

end

config firewall address

    edit 'US'

        set type geography

        set country 'US'

end

config firewall addrgrp

    edit 'Allowed'

        set member 'Lan' 'US'

end


config firewall local-in-policy

    edit 1

        set intf "wan1"

        set srcaddr "Allowed"     

        set srcaddr-negate enable <----- This command will negate the rule. It will only allow IPs on the allowed subnet and then deny all IP addresses.

        set dstaddr "all"

        set action deny

        set service "HTTPS"

        set schedule "always"

        set status enable

    next

end


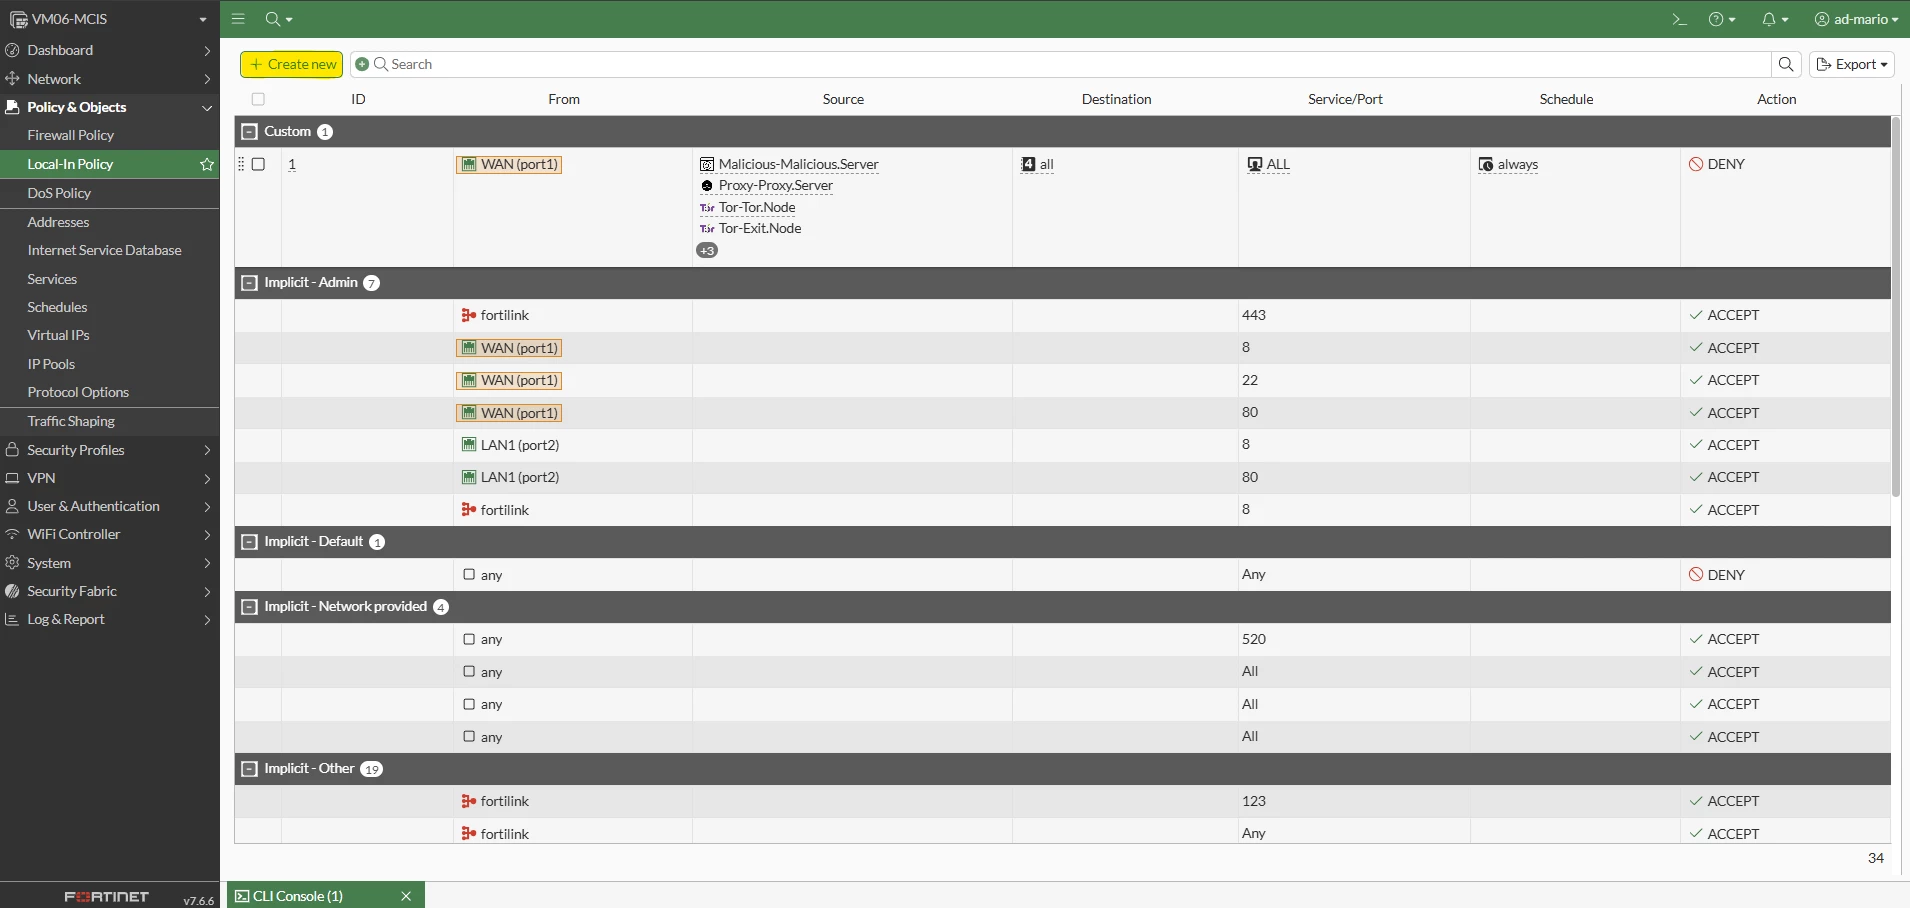
Starting from FortiOS v7.6.6, it is possible to create Local-In policies from the GUI.
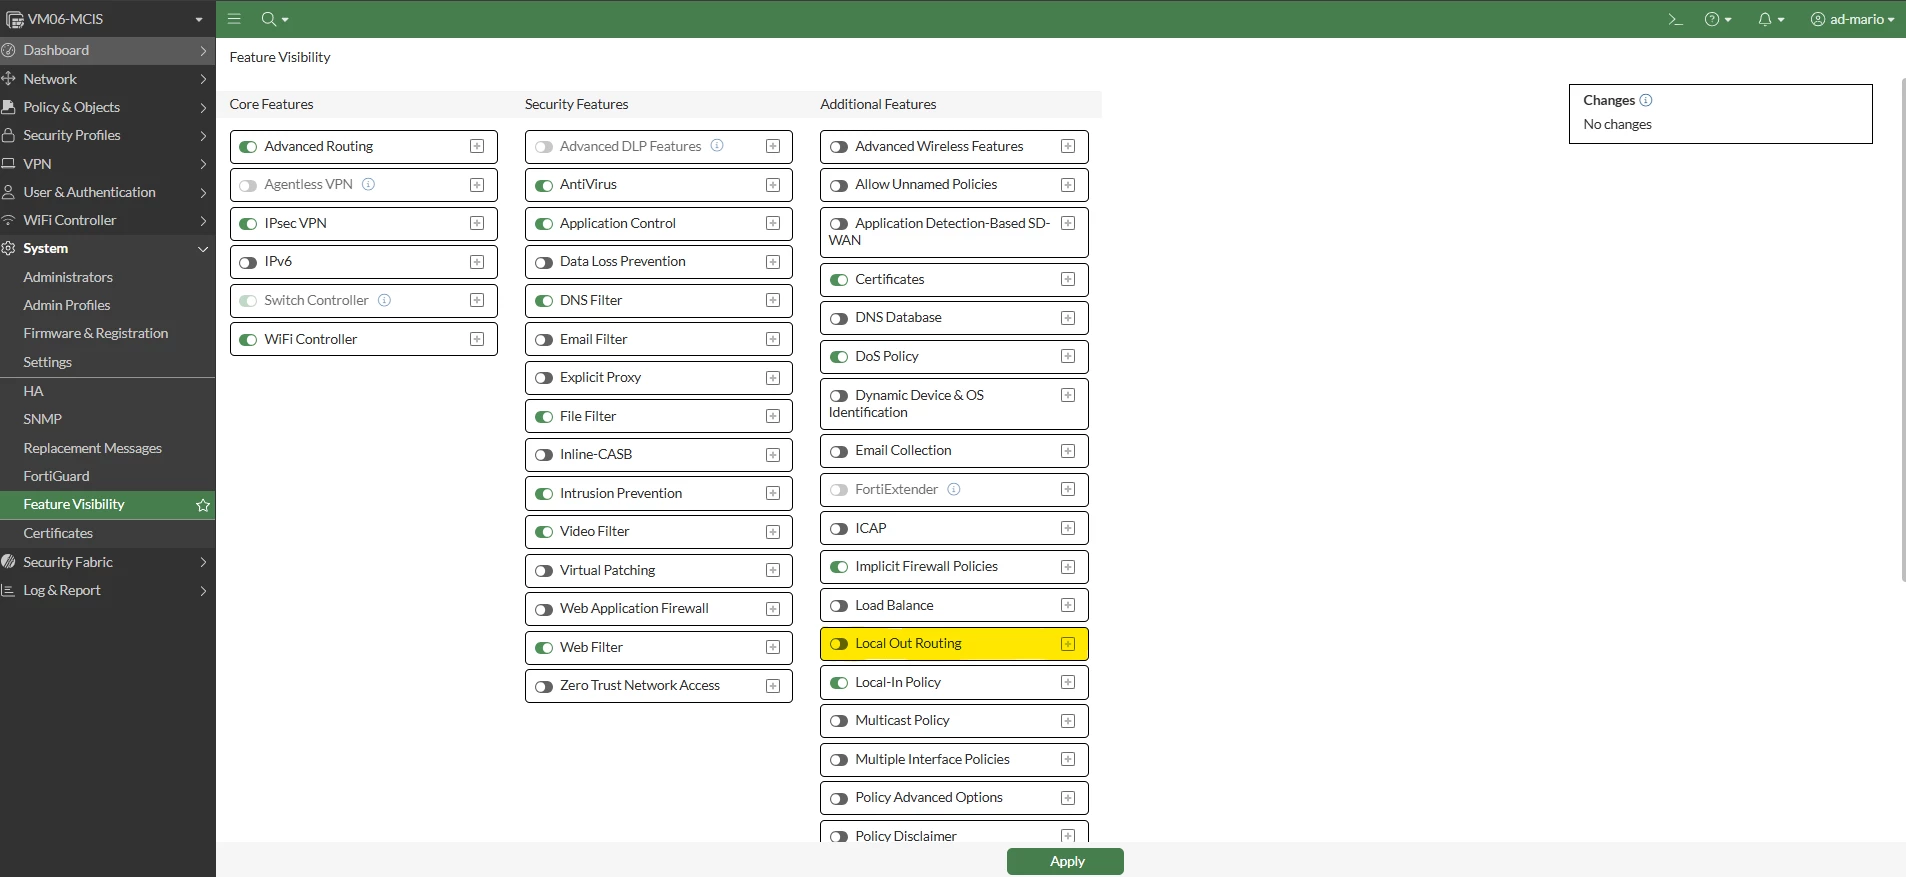
 

  1. It is necessary to activate this feature by going to System -> Feature Visibility -> Local-In-Policy.


Feature_visibility.png


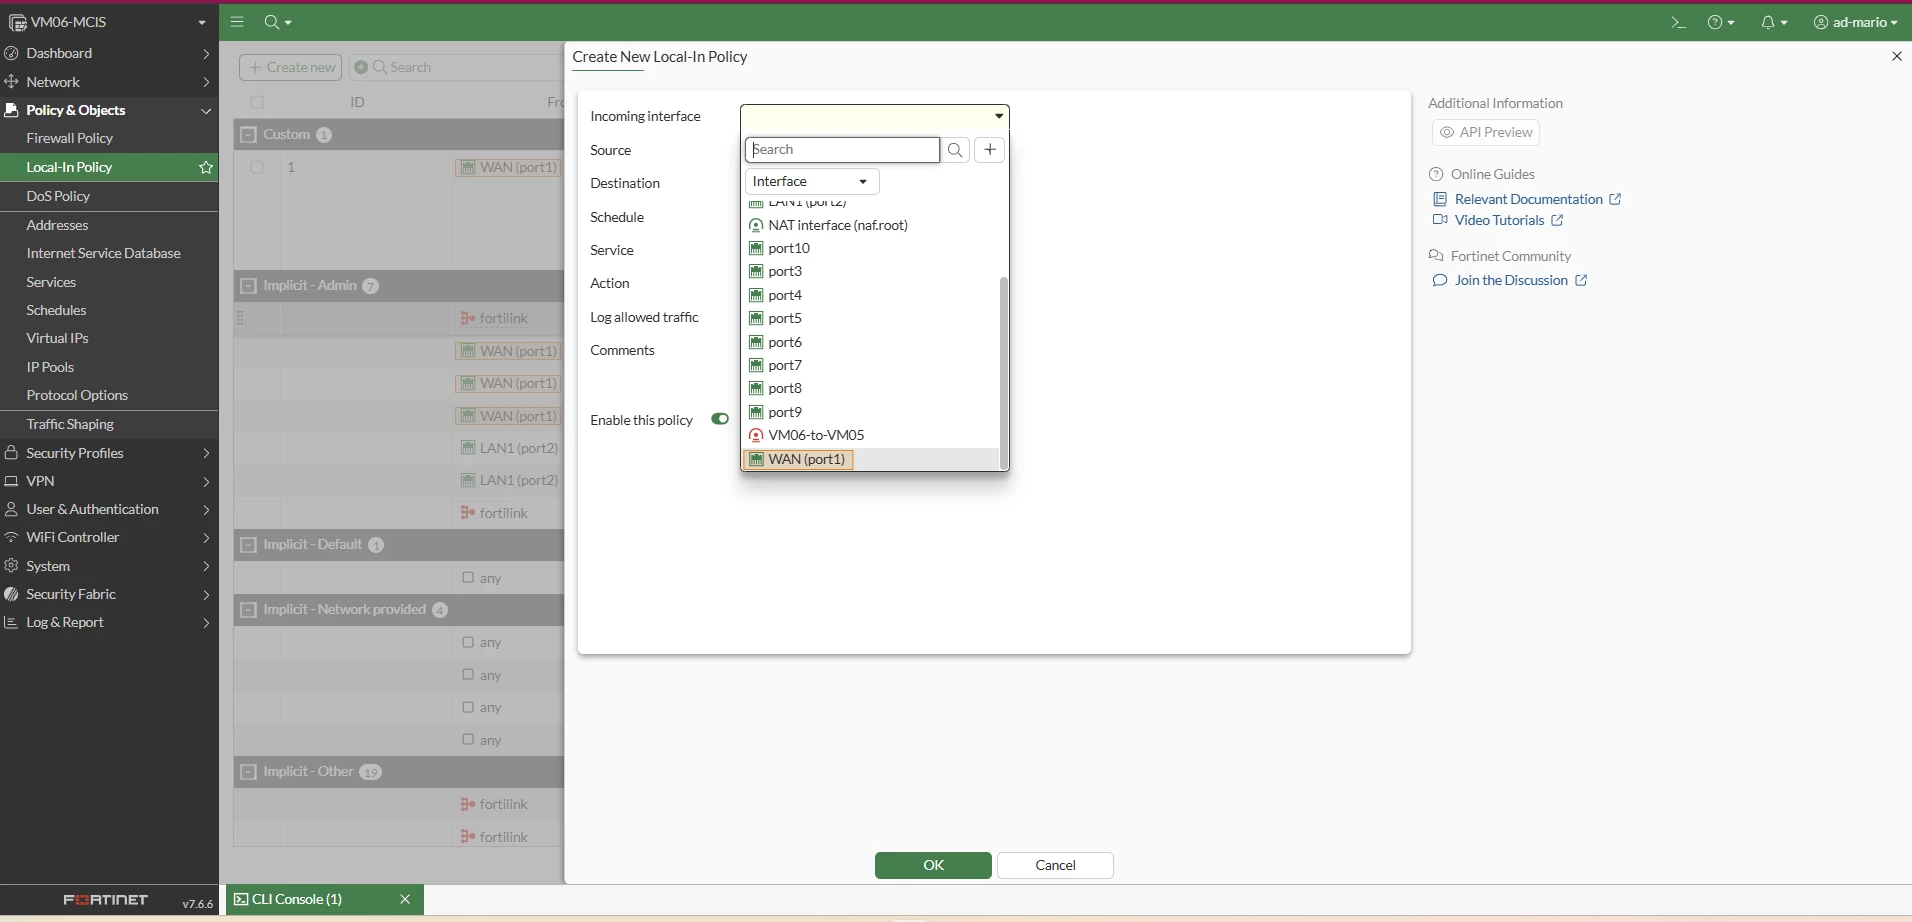
  1. Once Local-In-Policy is enabled, it is possible to create a new one.


    Create_New.png


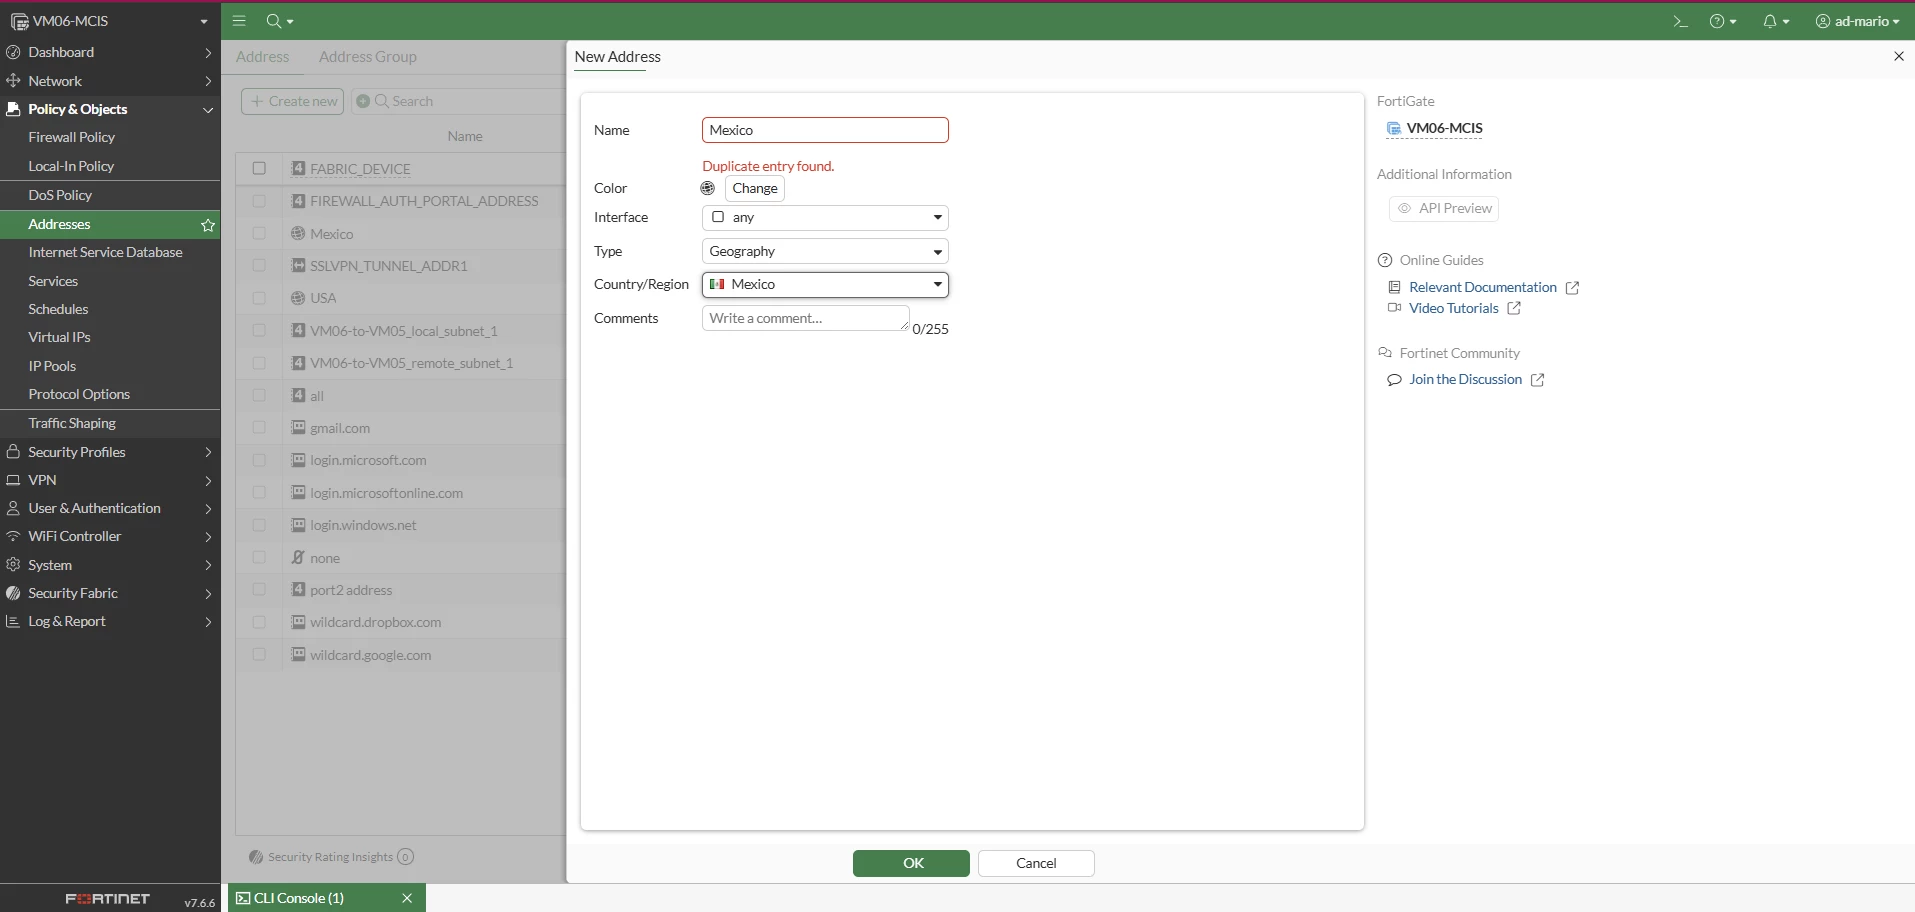
  2. As the first step, it is strongly recommended to know which countries or IP ranges are known and safe to be allowed, then select the incoming interface (WAN or SD-WAN Zone, depending on each case), add the interface, type Geography, and select the countries that will be allowed.


    Create_New_1.png


    Create_New_3.png


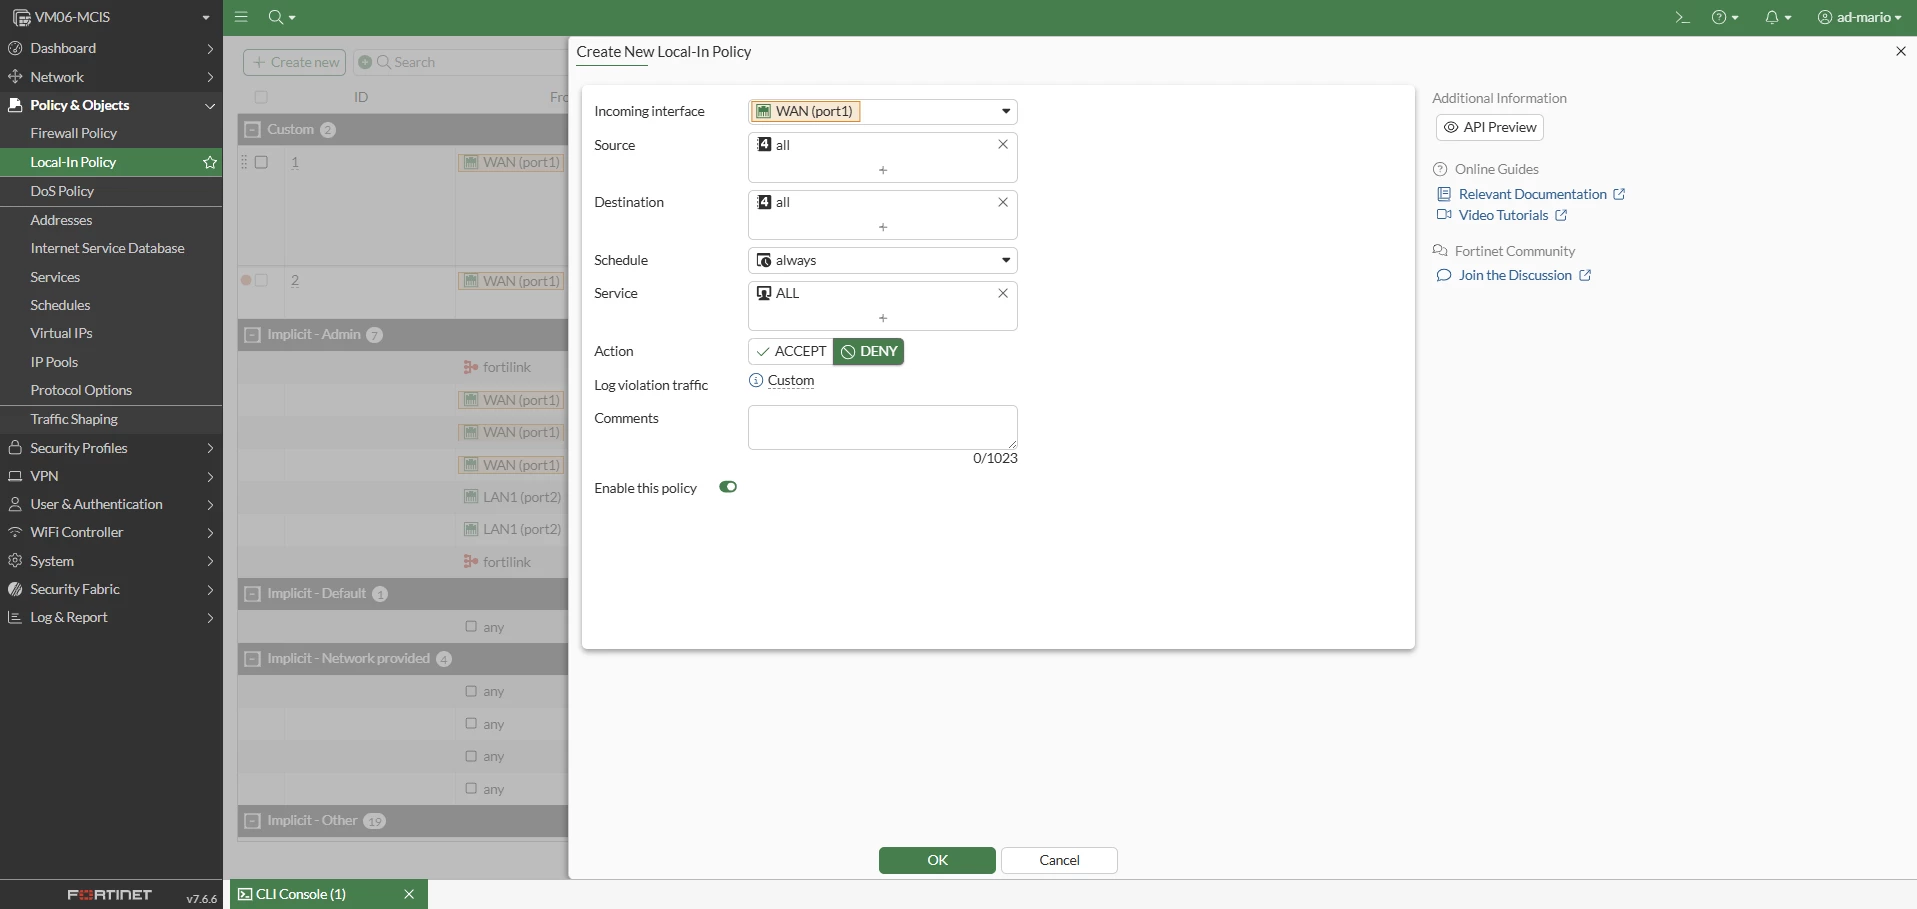
  3. Now that allowed countries have been defined, it will be necessary to create a 'Deny' policy, which will be used to deny all traffic coming from all other countries. Doing it this way, it will be possible to mitigate most of the login attempts from bots all around the world.


    Create_New_2.png


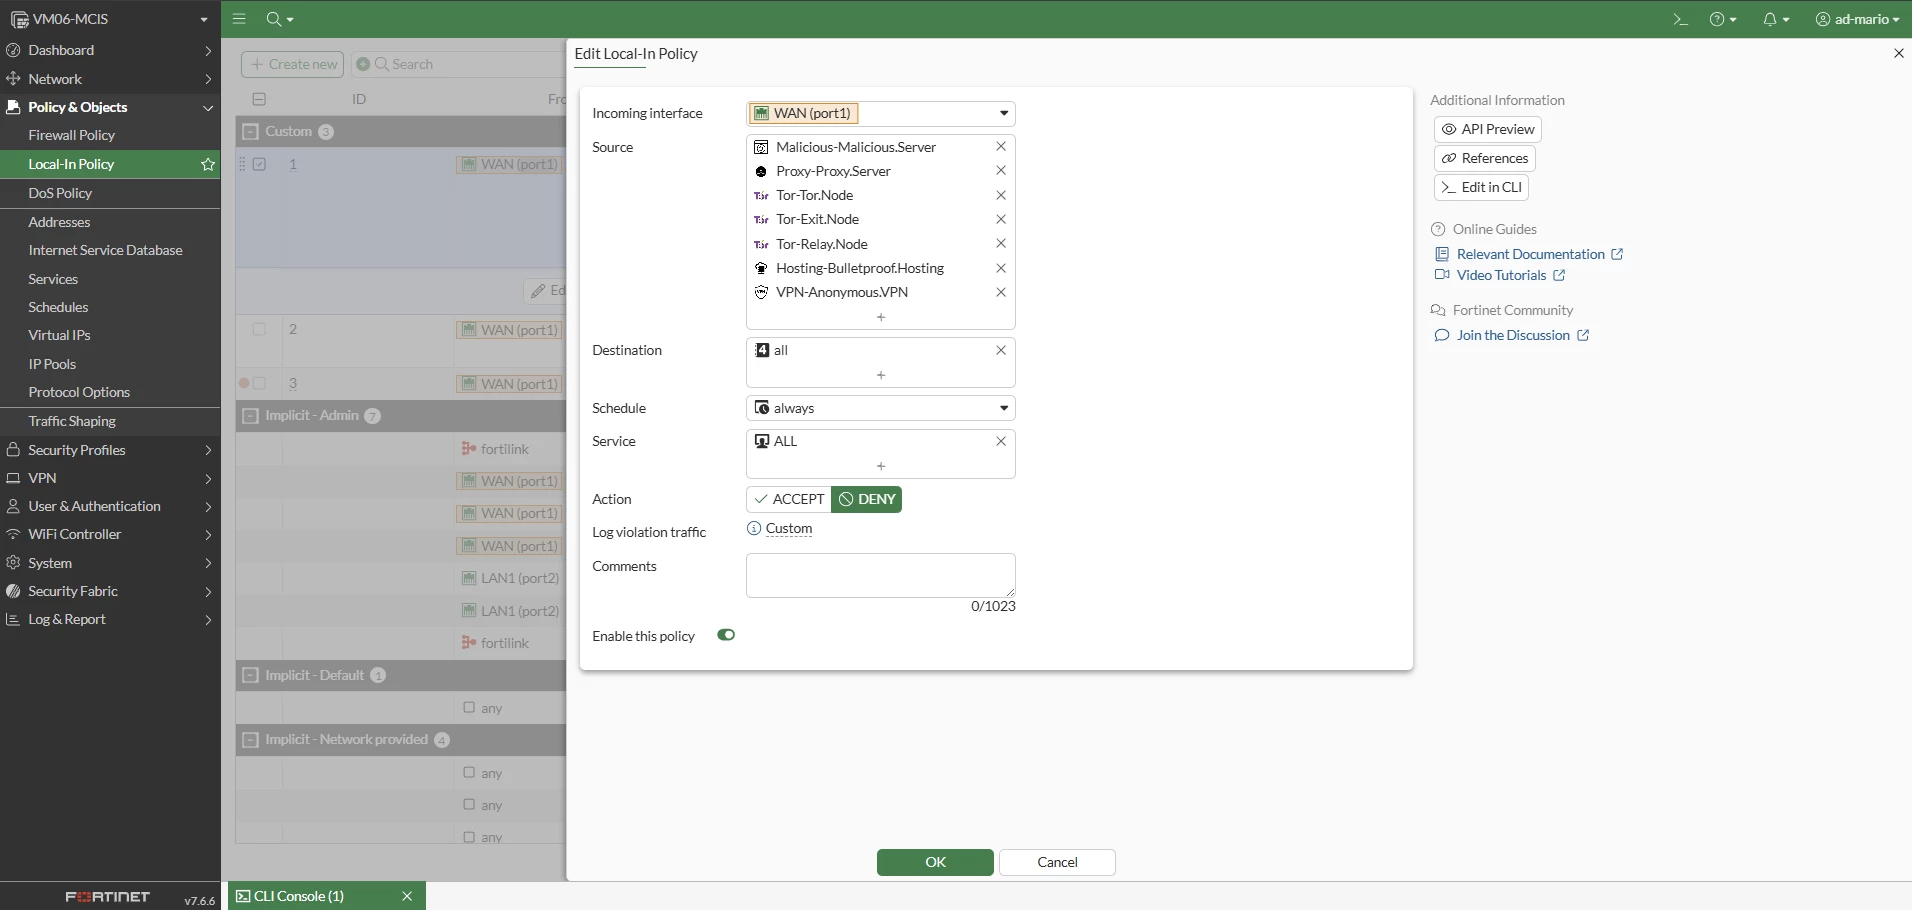
  4. As an additional step, a policy for identified malicious servers can be implemented.


Create_New_Malicious.png


Related article:
Technical Tip: Creating a Local-In policy (IPv4 and IPv6) on GUI

Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
Thought Leadership. Security Summit. Thursday, October 8th. Disney's Grand Californian Hotel & SPA, Anaheim, CA.
Security Operations Summit: Modernize SecOps. Operate AI-Native.AMER: November 4 | 9:00 AM PST. India and SAARC: November 5 | 10:00 AM IST. EMEA: November 5 | 10:30 AM CET. APAC: November 5 | 11:00 AM SGT