Setup used for this lab example:
The client 10.146.12.129 is connected to the FortiGate through L2TP.
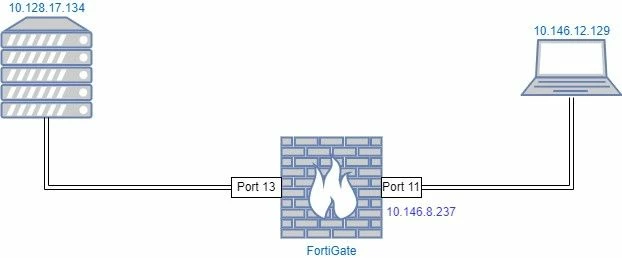 L2TP/IPSec details: L2TP pool:
config firewall address
    edit "l2tppool"
        set type iprange
        set start-ip 10.10.10.1
        set end-ip 10.10.10.254
    next
Phase1 configuration:
config vpn ipsec phase1-interface
    edit "l2tp-phase1"
        set type dynamic
        set interface "port11"
        set peertype any
        set net-device enable
        set proposal aes256-md5 3des-sha1 aes192-sha1
        set dpd on-idle
        set dhgrp 2
        set psksecret ENC *******
        set dpd-retryinterval 60
    next
end
Phase2 configuration:
config vpn ipsec phase2-interface
    edit "l2tp-phase2"
        set phase1name "l2tp-phase1"
        set proposal aes256-md5 3des-sha1 aes192-sha1
        set pfs disable
        set encapsulation transport-mode
        set l2tp enable
    next
end
L2TP enabled:
config vpn l2tp
    set status enable
    set eip 10.10.10.254
    set sip 10.10.10.1
    set usrgrp "group_l2tp"
end
The usrgrp group_l2tp is configured with one user for testing purposes. A static route is set to reach the destination 10.128.17.134 through port 13.
Two firewall policies are needed in this setup:
A Firewall policy to 'bridge' the IPsec interface to the physical/aggregate/VLAN interface.
config firewall policy
    edit 1
        set name "P11->L2TP"
        set srcintf "l2tp-phase1"
        set dstintf "port11"
        set srcaddr "all"
        set dstaddr "all"
        set action accept
        set schedule "always"
        set service "L2TP"
        set logtraffic all
    next
A Firewall policy to allow the traffic from the VPN client to the destination.
config firewall policy
    edit 2
        set name "l2tp-p1-p13"
        set srcintf "l2tp-phase1"
        set dstintf "port13"
        set srcaddr "l2tppool"
        set dstaddr "all"
        set action accept
        set schedule "always"
        set service "ALL"
        set logtraffic all
    next
These Firewall rules can be refined for better filtering.
6.4 branch behavior:
Once connected to the FortiGate, perform a ping to the destination 10.128.17.134 to see which interfaces are involved with L2TP.
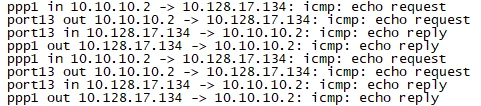 When a ping request is sent from the client, the interface's ppp1 receives the ping (in). This packet is forwarded to port13 (out) where the destination is.
The reply enters port13 and is forwarded to the ppp1 port.
After the upgrade to the v7.x branch, with all of the modification shown below, the behavior will differ: 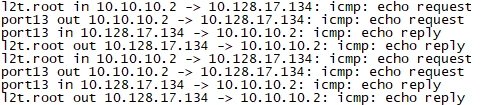 An interface named l2t.<vdom> (l2t.root in this example) that handles the traffic. This interface replaced the ppp1 seen in the version 6.4 example.
This will require some modifications to restore the l2tp service.
A new static route is required; this route needs to set the subnet used in the IP range related to the t2tp pointing on the interface l2t.<vdom>:
config route static
    edit 0
        set dst 10.10.10.0 255.255.255.0
        set device "l2t.root"
    next
Modification of the firewall policies:
config firewall policy
    edit 2
        set name "l2tp-p1-p13"
        set srcintf "l2t.root" <- Change the interface from phase1 to the l2t.<vdom>.
        set dstintf "port13"
        set action accept
        set srcaddr "l2tppool"
        set dstaddr "all"
        set schedule "always"
        set service "ALL"
        set logtraffic all
    next
Note that the firewall rules needed to bridge the IPsec interface and the physical port / aggregate are still required.
config firewall policy
    edit 1
        set name "l2tp-p1-p11bridge”
        set srcintf "l2tp-phase1"
        set dstintf "port11"
        set action accept
        set srcaddr "all"
        set dstaddr "all"
        set schedule "always"
        set service "ALL"
    next
No changes are required in the IPsec configuration either. Related document: L2TP over IPsec configuration needs to be manually updated after upgrading from 6.4.x or 7.0.0 to 7.0.1 and later | 




