Description | This article describes that when configuring VLAN interfaces on FortiGate, it is possible to encounter two common VLAN protocols: 802.1Q and 802.1AD, also known as QinQ (Double VLAN and clarifies the differences between these VLAN protocols and how they are configured on FortiGate. |
Solution | 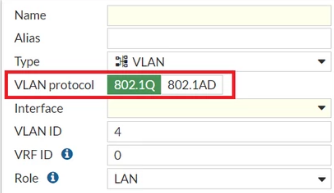
VLAN Protocol 802.1Q:
802.1Q is the most widely used VLAN tagging protocol. It allows the insertion of a 4-byte VLAN tag (or VLAN header) within the Ethernet frame. The VLAN tag consists of a 12-bit VLAN ID (VID), which can represent up to 4096 unique VLANs. (Maximum value is 4094).
Key Characteristics: Use Cases: 802.1Q VLANs are commonly used to segment and isolate traffic in local area networks (LANs). They are ideal for organizing network traffic within an enterprise network, separating departments, or creating isolated guest networks.
VLAN Protocol 802.1AD (QinQ): 802.1AD, commonly referred to as QinQ or Double VLAN tagging, extends the capabilities of 802.1Q. It allows the nesting of VLAN tags within another VLAN tag. QinQ effectively creates a 'VLAN within a VLAN', allowing for more extensive network segmentation. Supports a large number of VLANs due to nesting. The outer and inner VLAN tags each have their own VLAN IDs.
Key Characteristics: Tagging Method: QinQ adds a 4-byte VLAN tag, creating a nested structure. Configuration: QinQ requires configuring two sets of VLAN IDs: one for the outer VLAN and another for the inner VLAN. QinQ (802.1ad) is not supported on top of hardware‑switch ports; it must be used on regular physical or virtual interfaces.
Use Cases: Configuring VLAN Interfaces on FortiGate: When configuring VLAN interfaces on a FortiGate, it is possible to choose between 802.1Q and 802.1AD based on your specific networking requirements. FortiGate supports both VLAN protocols, allowing the creation of VLAN interfaces as needed for the network segmentation and isolation needs.
Related article: Technical Tip: 802.1ad QinQ real world scenario |





