dwickramasinghe1
Staff
Staff
April 25, 2025

Technical Tip: Troubleshooting an IPsec signature-based tunnel not coming up with a 'The peer's certificate is not verified' FortiClient error

  • April 25, 2025
  • 0 replies
  • 2995 views
Description This article describes how to handle the 'The peer's certificate is not verified' error on FortiClient with IPsec signature-based authentication.
Scope FortiGate, FortiClient, IPsec, Windows.
Solution

FortiClient can form a dial-up IPsec connection with FortiGate using signature-based authentication (certificates).

In some cases, the FortiGate IKE debugs gives minimal information as to why an IPsec tunnel is not coming up. For these types of scenarios, it is beneficial to verify the FortiClient logs and check to see if the FortiGate IPsec Server certificate is trusted by the endpoint.

This article assumes that the initial IPSEC configuration has been completed on both the FortiGate and FortiClient.

See Dialup IPsec VPN with certificate authentication | FortiGate / FortiOS 7.6.2 | Fortinet Document Library.

To verify if FortiClient is encountering issues with trusting the IPsec server certificate, check the IKE logs in the following location in Windows:

C:\Program Files\Fortinet\FortiClient\logs\trace\FortiIKE_x.log

Changing the FortiClient log level to debug is required for this step: see Technical Tip: How to enable debug log in FortiClient.

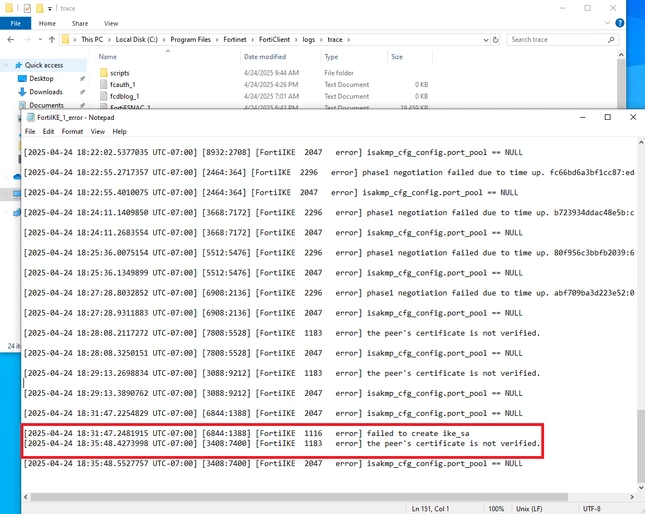
After checking the FortiIKE_X.log file, check to see if the following error shows up:

IPSECSignature.png
Error:
the peer's certificate is not verified


This error indicates that the FortiGate IPsec Server certificate is not trusted by the endpoint certificate authority store.

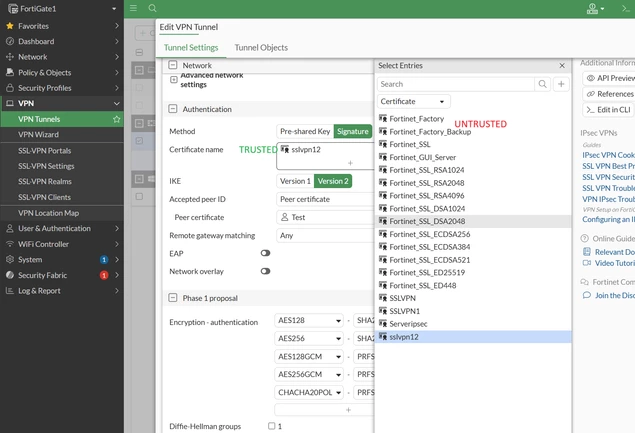
To resolve this issue, it is required to either upload the corresponding CA certificate onto the affected endpoint, or use a certificate from a trusted vendor on the FortiGate IPsec settings:

FortiGate GUI -> VPN -> VPN Tunnels -> *Select the desired tunnel* -> *Change the Signature certificate to a trusted one*.

TrustTheprocess.png
Related articles:

Technical Tip: Using IPsec VPN certificates and peer IDs for remote users

Dialup IPsec VPN with certificate authentication | FortiGate / FortiOS 7.6.2 | Fortinet Document Library

Technical Tip: How to enable debug log in FortiClient

    Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
    Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!