


Technical Tip: Troubleshoot and verify if traffic is hitting a Firewall Policy
Description
This article describes when there are many Firewall Policies for a specific interface pair, an easy way to see if a policy is actually hit by some traffic is to add the counter field in the GUI.
Scope
FortiGate, FortiOS.
Solution
- From the GUI, navigate to Policy & Objects -> Firewall Policy.
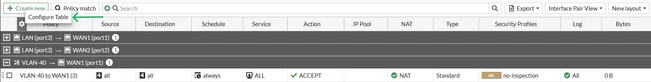
- Select the 'Configure Table' option as shown in the screenshot below:
-
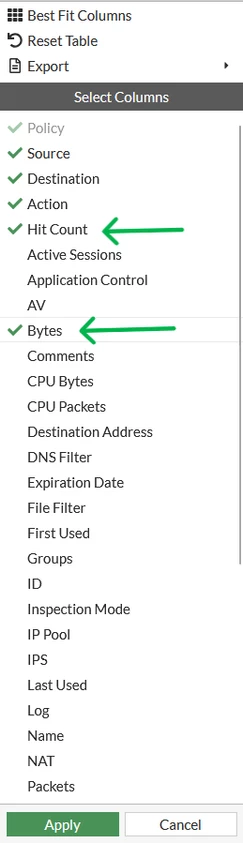
Select 'Hit Count' as well as 'Bytes' and then Apply:
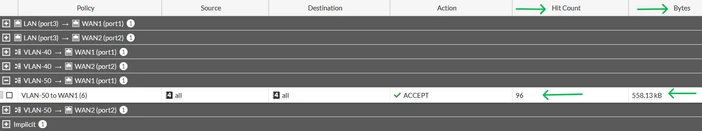
- Now verify that some packets hit this Policy will show the number of policy hits and Bytes as shown in the screenshot below:
For real-time troubleshooting for current traffic, validate the sessions table and policy match: Technical Tip: How to know wich policy ID is used in FortiGate session table
Note:
For accelerated traffic (ex. NP2 ports), only the start of the session packet will be counted, and this counter does therefore not reflect the real traffic count. For non-accelerated traffic, all packets will be counted.
Related articles:
Technical Tip: Information about traffic log counters for NP2 or NP4 offloaded sessions


