




Technical Tip: Strong Password 'Password Policy' feature
Description
This article describes that since FortiOS 4.0 MR1, there is a new feature that enables FortiGate administrator passwords to adhere to strict requirements. This includes proper aging attributes attached, so that passwords must be changed on a continual basis.
Scope
FortiGate.
Solution
To enable password options:
- Go to System -> Admin -> Setting.
- Select Enable for the Password Policy, and edit the options as required.
To enable using CLI:
config system password-policy
set status enable
end
For version V4.0 MR1:
#FGT (password-policy) # get
status : enable
apply-to : admin-password
minimum-length : 8
must-contain :
change-4-characters : disable
expire : 0
config system password-policy
set status [enable | disable] # default is disable
set apply-to [admin-password ipsec-preshared-key] # default is admin-password
set minimum-length xxx # default is 8
set apply-to [admin-password ipsec-preshared-key] # default is admin-password
set minimum-length xxx # default is 8
set must-contain [lower-case-letter upper-case-letter non-alphanumeric number] # default is NULL
set minimum-characters-change 4 #default is 0, when not zero, it requires to change at least N characters for password change
set admin-password-expire xxx # Unit=DAYS before expire. Default is 0, means never expire
set minimum-characters-change 4 #default is 0, when not zero, it requires to change at least N characters for password change
set admin-password-expire xxx # Unit=DAYS before expire. Default is 0, means never expire
end
config system admin
edit xxx
set password-expire YYYY-MM-DD HH:MM:SS # default 0, means never expire.
set force-password-change [enable | disable] # initially set to disable, when set to enable, user must change his password next time he logs in
next
end
For version V5.4 and above:
config system password-policy
set status enable # default is disable
set apply-to admin-password [admin-password ipsec-preshared-key] # default is admin-password
set minimum-length 8 # default is 8
set min-lower-case-letter 0
set min-upper-case-letter 0
set min-non-alphanumeric 0
set min-number 0
set change-4-characters disable
set expire-status disable Default is 0, means never expire
set reuse-password enable
end
config system admin
edit xxx
set password-expire YYYY-MM-DD HH:MM:SS # default 0, means never expire.
set force-password-change [enable | disable] # initially set to disable, when set to enable, user must change his password next time he logs in
next
end
set status enable # default is disable
set apply-to admin-password [admin-password ipsec-preshared-key] # default is admin-password
set minimum-length 8 # default is 8
set min-lower-case-letter 0
set min-upper-case-letter 0
set min-non-alphanumeric 0
set min-number 0
set change-4-characters disable
set expire-status disable Default is 0, means never expire
set reuse-password enable
end
config system admin
edit xxx
set password-expire YYYY-MM-DD HH:MM:SS # default 0, means never expire.
set force-password-change [enable | disable] # initially set to disable, when set to enable, user must change his password next time he logs in
next
end
Note:
In the latest FortiOS version, both options can be specified in the GUI, but in the CLI, it is necessary to enable both options manually.
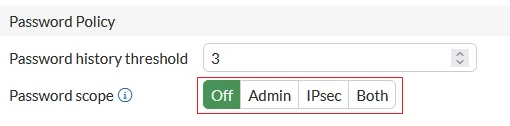
Selecting only 'Admin' affects only the Admin settings. Choosing only 'IPsec' changes only the IPsec settings. Selecting both impacts both Admin and IPsec settings
Related articles:

