



Technical Tip: SSL VPN to be explicitly enabled or disabled from GUI and CLI
Description
This article describes that from v7.0.1, the SSL VPN enable option is added in SSL VPN settings.
To connect to SSL VPN, it is necessary to toggle on 'Enable SSL-VPN' on the GUI/CLI, and the SSL VPN interface must be up.
Scope
FortiGate.
Solution
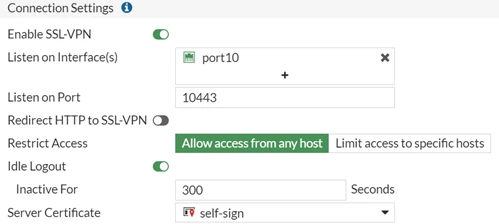
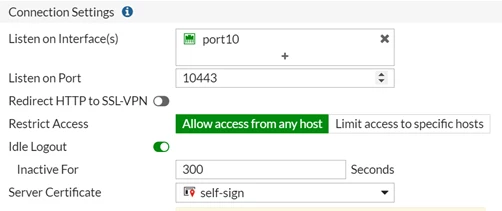
set status {enable | disable} -> Status is enabled by default.
end
Note:
At v7.4.8, SSL VPN is not supported on FortiGate G-series entry-level models. At v7.6.0, SSL VPN was removed from 2GB RAM models. Lastly, at v7.6.3, the SSL VPN tunnel mode was replaced with IPsec VPN, which now applies to all FortiGate models.
Starting version 7.4.4 and above, the SSL VPN feature cannot be enabled from the GUI. Enable SSLVPN settings through the CLI by running the following commands:
config system settings
set gui-sslvpn enable
end
In a multi-VDOM environment, execute the following commands:
config vdom
edit <vdom-name>
config system settings
set gui-sslvpn enable
end
end
Related documents:
SSL VPN not supported on Fortigate G-series Entry-level models

