



Technical Tip: SNMP Server unable to pull information from the FortiGate over IPSec tunnel
Description
This article addresses an issue where the FortiGate does not reply to SNMP queries over an IPSec tunnel.
Scope
FortiOS.
Solution
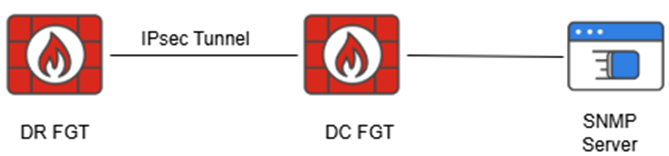
In this scenario, the DC FortiGate is forwarding SNMP queries to the DR FortiGate via the IPsec tunnel, but no response is received from the DR firewall.
Network diagram:
The packet sniffer taken on the DR FortiGate shows incoming traffic for UDP/161, but no outgoing response traffic is observed:

To troubleshoot the issue, review the following suggestions:
IPsec tunnel interfaces do not require an IP address to be assigned, but if an address is not set, then any outgoing traffic (such as SNMP response traffic) will use an IP address from the first available FortiGate interface (which may not be appropriate for the VPN tunnel; see also: Technical Tip: Configure an IP Address on an IPsec Tunnel Interface). To resolve this, navigate to config system snmp community in the CLI and specify an outgoing source IP address using the set source-ip option. For example:
config system snmp community
    edit 1
        config hosts
            edit 1
                set source-ip x.x.x.x
            next
        end
    next
end
Note: set source-ip to a local FortiGate address that is allowed to pass through the IPsec VPN phase2 selectors.
If the SNMP query is destined for a different FortiGate interface through the IPsec tunnel (such as a VLAN interface), then a firewall policy must be added to allow the traffic (e.g., IPsec VPN -> VLAN interface).
Verify that no local-in policy exists that blocks incoming SNMP traffic (see also: Technical Tip: SNMP traffic blocked due to a local-in policy violation).
Verify that trusted-hosts is either not configured for the local admin accounts or that the SNMP manager's IP address is included in the trusted-hosts list (see also: Technical Tip: SNMP access to FortiGate).
If SNMP is still not functioning as expected, then run SNMP debugs to gather further information:
diagnose debug disable
diagnose debug reset
diagnose debug application snmpd -1
diagnose debug enable
In the following example, SNMP debugs have an error message stating 'snmpd: name mismatch while ha is on':

To resolve this issue, disable the ha-direct option under config system snmp community:
config system snmp community
    edit 1
        config hosts
            edit 1
                set ha-direct disable
            next
        end
    next
end
Note: When ha-direct is enabled, the FortiGate is only expected to send/receive SNMP traffic using dedicated management ports and will not respond to SNMP traffic sent to non-dedicated management ports. Additionally, this setting must be enabled in order for HA cluster members to be queried individually via SNMP (as opposed to querying the HA Primary via the shared cluster addresses).
Once the ha-direct option is disabled, traffic flows through the tunnel, and the SNMP server successfully pulls the information.


